Credential Governance
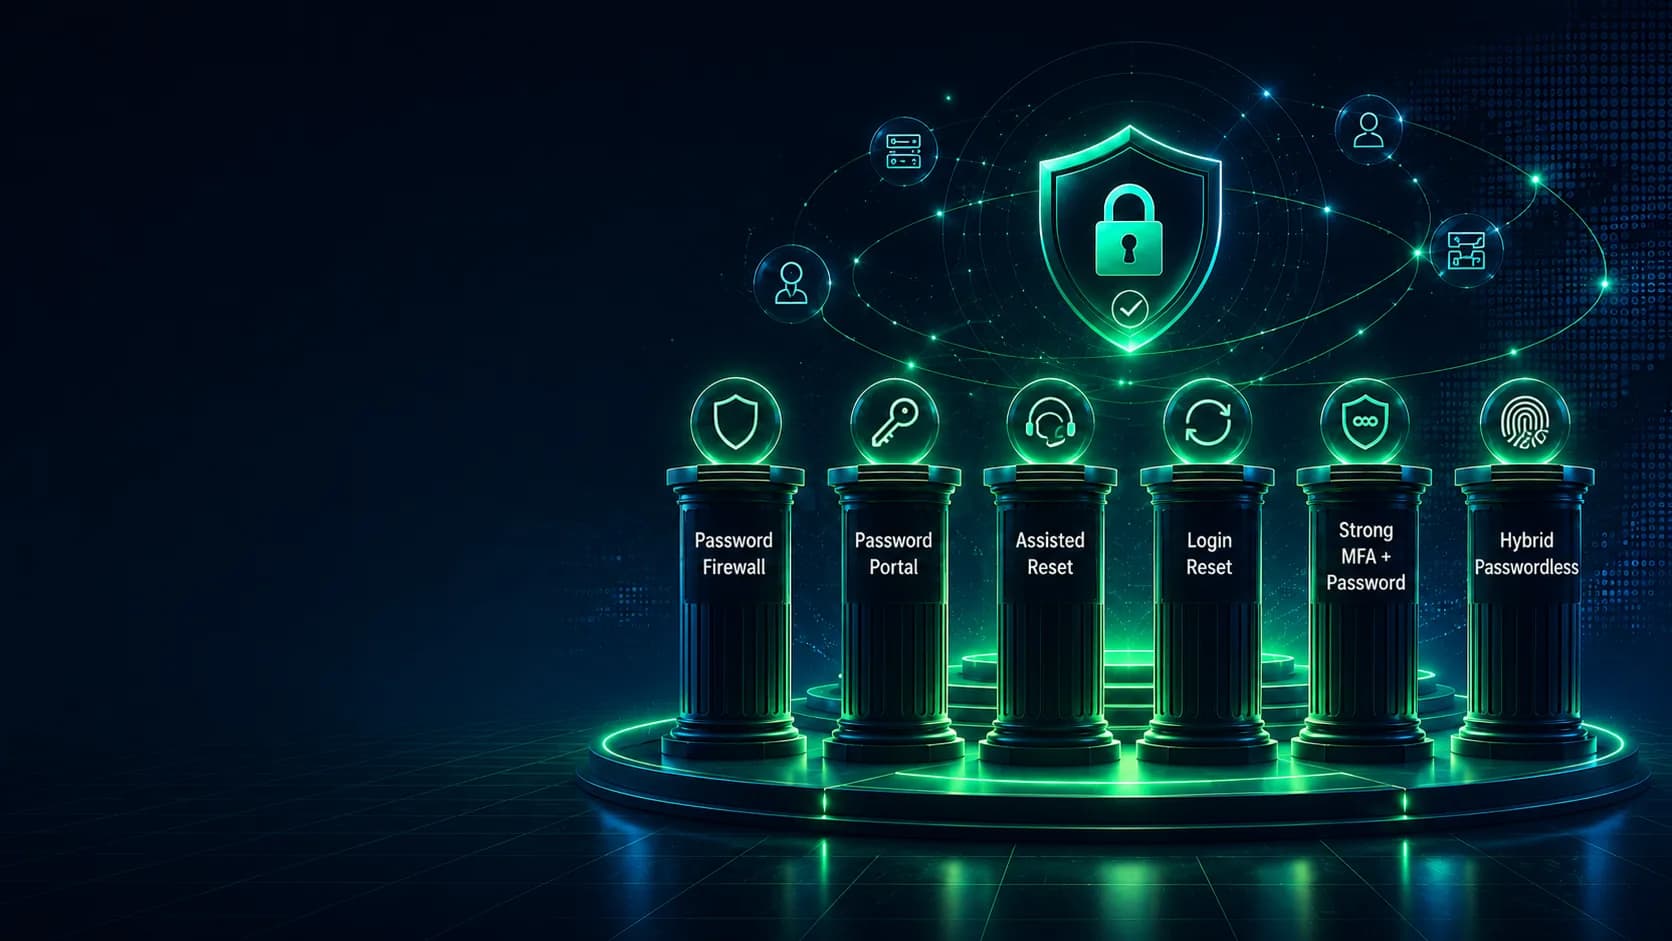
The 6-Pillar Framework for Password and Passwordless Identity
Password management is a point solution. Credential Governance manages every credential — passwords, keys, tokens, service accounts — from birth to retirement, across Active Directory, Entra ID, and legacy systems.

Protecting the world’s workforce since 1997 • Over 15 Million Licenses Sold
How It Works
How Credential Governance Works
Six pillars, one credential lifecycle — each governs a different moment where a password is set, recovered, or proven. Play any pillar's short explainer and follow the transcript as it speaks.
- Pillar 01TranscriptTap a word to play from there
Spring2026!
Capital letter.
Number.
Symbol.
Your directory calls it strong.
Attackers call it their first guess.
Rules that only check format let predictable, breached passwords walk right in.
Avatier Password Firewall closes that gap at the source.
A lightweight agent on every domain controller intercepts every password change, from users, admins, and systems, before it's ever written.
In milliseconds, it checks your policy, banned words, NIST common passwords, and Have I Been Pwned breach data, without the password itself ever leaving.
Spring2026!
Blocked.
One policy across Active Directory, Entra ID, and legacy systems.
Stricter rules for admins, set by group.
And every decision is logged as audit evidence, ready for your SIEM.
Built for the IT, IAM, and Active Directory teams who own password policy at large enterprises.
Avatier Password Firewall.
Pillar One of Credential Governance.
It complements MFA.
See it at credentialgovernance.com.
Password Firewall
Every password change is intercepted and checked against breach data and policy in real time — weak or exposed credentials are blocked before they ever reach Active Directory or Entra ID.
Explore Password Firewall - Pillar 02TranscriptTap a word to play from there
Every forgotten password becomes a ticket.
Every lockout becomes a call.
And your help desk pays for each one.
Avatier Password Portal changes that.
One secured place where your people fix their own credentials, any time, from anywhere.
Locked out on a Saturday?
She opens the portal right in Microsoft Teams, verifies with the MFA she already has, and unlocks her account.
Then sets a new password, checked against policy.
One change, synced in real time to Active Directory, Entra ID, Oracle, and her other systems.
Every step verified, enforced, and logged for audit.
No ticket.
No wait.
Up to 70% of password tickets… gone.
Built for employees, contractors, frontline, and remote teams, in 34 languages.
Avatier Password Portal.
Pillar Two of Credential Governance.
See it at credentialgovernance.com.
Password Portal
Users reset, unlock, and enroll themselves across web, mobile, Teams, Outlook, and AI voice — every request MFA-verified and breach-checked, with no help-desk ticket.
Explore Password Portal - Pillar 03TranscriptTap a word to play from there
The caller sounds urgent.
Says she's the VP, locked out, boarding a flight.
Reset it.
Now.
Agents get talked into resets.
Avatier Assisted Reset makes sure the system can't be.
The agent doesn't ask questions or make judgment calls.
One click, and a verification challenge goes straight to the real user's device.
The agent only sees the result: pass, or fail.
The real VP never asked for a reset.
She denies it.
Fail.
The reset never happens.
When the request is real, the user approves, the agent sees pass, and a guided, policy-scoped reset finishes the job.
Every assisted reset leaves a record: who asked, how they were verified, which agent helped, and what changed.
And it works with the service desk you already run.
Built for service desks, and the security teams who answer for them.
Avatier Assisted Reset.
Pillar 3 of Credential Governance.
See it at credentialgovernance.com.
Assisted Reset
When a user calls the help desk, the identity challenge routes to the user's own device — the agent only ever sees pass or fail, so a reset can't be social-engineered.
Explore Assisted Reset - Pillar 04TranscriptTap a word to play from there
Locked out at the login screen.
Hotel Wi-Fi, no VPN, and the help desk can't reach a laptop that won't let you in.
Avatier Login Reset puts recovery right on that screen, before you ever sign in.
Choose Unlock and Reset, right on that screen.
A locked-down, secure browser opens.
Verify with your MFA, then set a new password, checked against policy.
Network and cached credentials update together, so the laptop works, on the network or off it.
And on day one, a new hire is verified against HR data right at the login screen, before anyone hands them a temporary password.
Windows and Mac.
Active Directory, Entra ID, and hybrid.
Citrix and virtual desktops.
Built for remote, hybrid, and frontline workforces, and the IT teams who support them.
Avatier Login Reset.
Pillar 4 of Credential Governance.
See it at credentialgovernance.com.
Login Reset
Unlock and reset right at the Windows and Mac login screen, MFA-verified before the network — and cached credentials update automatically, so there's no second lockout.
Explore Login Reset - Pillar 05TranscriptTap a word to play from there
Your password just got phished.
Now someone else has it, and they're heading for your servers.
Windows login trusts a password.
One stolen credential, and an attacker can move from machine to machine.
Avatier Strong MFA Login hardens Windows login itself.
MFA comes first, before the password is even asked for.
So the stolen password goes nowhere.
Not the workstation, not the file server, not RDP into the domain controller.
And every failed attempt alerts security.
For the real admin, it's three gates: her MFA, a breach-checked password, and an optional corporate factor, like an employee ID.
Critical accounts can even stack two methods.
Cached credentials stay in sync, so laptops keep working off the network.
Windows, RDP, Citrix, and virtual desktops.
No TPM chip or PKI lock-in.
Built for admins, critical servers, and the security teams who protect them.
Avatier Strong MFA Login.
Pillar 5 of Credential Governance.
See it at credentialgovernance.com.
Strong MFA Login
Three gates on every server and workstation login: an MFA challenge first, a Firewall-checked password second, an optional corporate factor third — and a miss at any gate alarms security.
Explore Strong MFA Login - Pillar 06TranscriptTap a word to play from there
Seven fifty-five A.M.
Same nurse.
Same shared kiosk.
Same forgotten password…
Two very different mornings.
In this one, passwordless means a phone she isn't allowed to carry on the floor.
Locked out.
She calls the help desk… and waits.
In this one, she presses Ctrl+Alt+Del.
Avatier Hybrid Passwordless Login appears right on the Windows login screen.
She picks her account.
No password to type.
She verifies with the MFA her company already uses: a hardware token, a passkey, or Avatier's Identity Challenge Card.
No special hardware required.
No password to remember.
And if her directory password is ever locked or forgotten, Avatier resets it and syncs it across her other systems… more than 87 of them, like SAP, Oracle, and Entra ID.
Then she moves… to Citrix, a virtual desktop, another shared station.
The credential moves with her.
Nothing to carry.
Underneath, the directory password is still governed: synchronized, validated, breach-checked.
Passwordless for her.
Governed for IT.
Built for shared workstations, Citrix and virtual desktops, and sites where phones are banned.
Hybrid Passwordless Login.
Pillar Six of Credential Governance.
See it at credentialgovernance.com.
Hybrid Passwordless Login
The credential travels with the user across shared workstations, Citrix, and VDI; your existing MFA becomes the passwordless factor — no special hardware, TPM, or PKI required.
Explore Hybrid Passwordless Login
Outcomes
What Credential Governance Delivers
- Up to 70% reduction in help desk password tickets
- 100% MFA enforcement on every credential event
- Zero successful social-engineering resets
- Audit-ready evidence for SOC 2, ISO 27001, NIS2, DORA, and CMMC
- Rollout in days, not months — no TPM, no PKI
Password Management vs Credential Governance
| Password Management | Credential Governance | |
|---|---|---|
| Scope | Password storage only | Full credential lifecycle |
| Policy enforcement | At the vault, after the fact | At the source, in real time |
| Help desk security | Manual verification, easy to social-engineer | MFA-verified workflow, zero exceptions |
| Login recovery | Requires IT ticket | Embedded in Windows & Mac login screen |
| Passwordless coverage | Surface only — passwords buried beneath | Hybrid — passwordless with governance |
| Audit evidence | On request, manual export | Immutable, real-time |
| Rollout | Weeks to months, TPM/PKI required | Days, hardware-agnostic |
Fits Your Stack

Microsoft
Entra ID, Active Directory, Intune, Teams, Outlook, Copilot.

Okta
Okta Verify and Workforce Identity integration.

CyberArk
PAM integration for privileged credential governance.

ServiceNow
Native connector for ticketing and CMDB updates.

HR systems
Workday, BambooHR, SuccessFactors for lifecycle triggers.

Existing IAM
Ping, SailPoint, Saviynt — coexistence, not rip-and-replace.
The picture at a glance
Avatier is the only vendor that covers every category
NP Accel mapped 25+ identity vendors against 11 product categories. Avatier markets all 11. Microsoft markets 7. Okta 6. CyberArk 3. Every other competing vendor leaves visible gaps the buyer has to fill by stitching three to six products together from three to six vendors.
Frequently Asked Questions
Common questions about Avatier Credential Governance, answered.
What is Credential Governance?
Credential Governance is a unified framework from Avatier that manages every enterprise credential — passwords, keys, tokens, and service accounts — across its full lifecycle, with continuous policy, MFA-verified workflows, and audit-ready evidence. It unites six pillars: Password Firewall, Password Portal, Assisted Reset, Login Reset, Strong MFA Login, and Hybrid Passwordless Login. Available in 34 languages and certified to SOC 2 and ISO 27001.
How is credential governance different from IGA?
Identity Governance and Administration (IGA) governs who has access to what — provisioning, role mining, recertification. Credential Governance governs the credential itself — issuance, rotation, attestation, recovery, and revocation across Active Directory, Entra ID, and legacy systems. The two complement each other. IGA platforms like SailPoint and Saviynt handle access entitlements; Credential Governance handles the lifecycle of the secret used to assert that access.
How is it different from a password manager?
A password manager (LastPass, 1Password, Bitwarden) stores and auto-fills user-chosen passwords on a device. Credential Governance enforces password policy at the source — every change is validated against NIST, Have I Been Pwned, and custom dictionaries before it reaches Active Directory or Entra ID. It also handles MFA-verified resets across web, mobile, Teams, Outlook, and AI voice; help desk workflows; and Windows login-screen recovery. A password manager is a tool; Credential Governance is the framework.
Do I need to replace Okta, Entra, or CyberArk?
No. Avatier Credential Governance fits alongside existing IAM and PAM investments, closing gaps those platforms don't cover. Okta and Microsoft Entra ID govern access; CyberArk governs privileged accounts. Credential Governance governs the credential itself — every issuance, rotation, attestation, and revocation across Active Directory, Entra ID, and legacy systems — with MFA-verified workflows, breach-database checks, and audit evidence for SOC 2, ISO 27001, NIS2, DORA, and CMMC.
How do I block breached passwords in Active Directory?
Install the Avatier Password Firewall agent on each Active Directory domain controller. The agent intercepts every password-change request and validates it against the Have I Been Pwned breach database, NIST Common Passwords, and your enterprise's policy in under a second. If the password is compromised, the change is rejected with real-time feedback. See the Password Firewall pillar for how the agent deploys, governs new domain controllers automatically, and extends to Entra ID.
How do I prevent a Scattered Spider attack on my help desk?
Scattered Spider, Octo Tempest, and copycat groups target help-desk agents, social-engineering them into resetting passwords or MFA without proof of identity. MGM ($100M), Caesars ($15M), Clorox ($380M), and Change Healthcare ($22M) breaches all started this way. Avatier Assisted Reset routes every agent-initiated reset through an MFA challenge sent to the user — bound to your existing identity provider. The agent never sees the factor and cannot bypass.
How long does deployment take?
Most customers deploy Avatier Credential Governance in under a week. The Password Firewall agent installs on domain controllers in minutes per DC, with auto-detection and auto-deployment to new controllers. Password Portal, Assisted Reset, and Login Reset deploy via MSI, GPO, or Intune in hours. No TPM, no PKI, no hardware refresh — Avatier is hardware-agnostic and runs on any Windows device, Mac, Citrix, or Azure Virtual Desktop.
What compliance frameworks does Credential Governance support?
Credential Governance generates immutable, audit-ready evidence for SOC 2 Type II, ISO 27001, NIST 800-63-3, CMMC, GDPR, HIPAA, NIS2, and DORA. Every credential event — change, reset, rotation, attestation, revocation — is logged with tamper-evident timestamps and exportable to SIEM platforms (Splunk, Microsoft Sentinel, Chronicle). Live certification artifacts are available at trust.avatier.com, Avatier's SafeBase trust center.
How does Avatier handle 34-language support?
Avatier Credential Governance ships with native support for 34 languages — including English, Spanish, French, German, Japanese, Portuguese, Chinese, Korean, Italian, Dutch, Hindi, Arabic, Swedish, and Hebrew — across web, mobile, Microsoft Teams, Outlook, and AI voice, including the call-center workflow. Right-to-left layouts (Arabic, Hebrew) and CJK fonts (Chinese, Japanese, Korean) are fully supported, with brand and product names preserved in their English form.
Why "Credential Governance" instead of "password management"?
Password management is a point solution — it stores passwords, sometimes rotates them, and stops there. Credential Governance is a category. It manages every enterprise credential — passwords, API keys, certificates, service accounts, tokens — across its full lifecycle: issuance, attestation, rotation, recovery, revocation, and audit. Regulators (NIS2, DORA, NYDFS 500.17, SEC disclosure rules) increasingly require demonstrable lifecycle control, not just hygiene. Password management was sufficient in 2015. It isn't in 2026.
Further reading
Related from the Credential Governance library
Self-Service Account Unlock with Avatier: No Reset, No Ticket
A locked-out user who still knows the password needs the lock cleared, not a new password. How Avatier handles self-service account unlock in the portal, at the login screen and in AI assistants.
Read more
Active Directory User Management, Governed with Avatier
Enable, disable, rename, move, expire: everyday Active Directory account changes add up. How to run each one through policy, approval and a record with Avatier User Management.
Read more
Locked Out Off VPN: Remote Password Reset with Avatier Login Reset
A remote worker forgets or resets a domain password off VPN and is stuck at the login screen with stale cached credentials. How Avatier Login Reset brings MFA-verified recovery home.
Read moreSee Credential Governance in Action
Book a 30-minute demo with an Avatier solutions architect.