B2B External Identity & Guest Access: The 2026 Enterprise Guide
B2B external identity and guest access is the discipline of governing partner, vendor, contractor, and guest identities that are not employees. The 2026 enterprise guide to what external access is, the controls that keep it safe, and the lifecycle that keeps it from becoming a breach path.
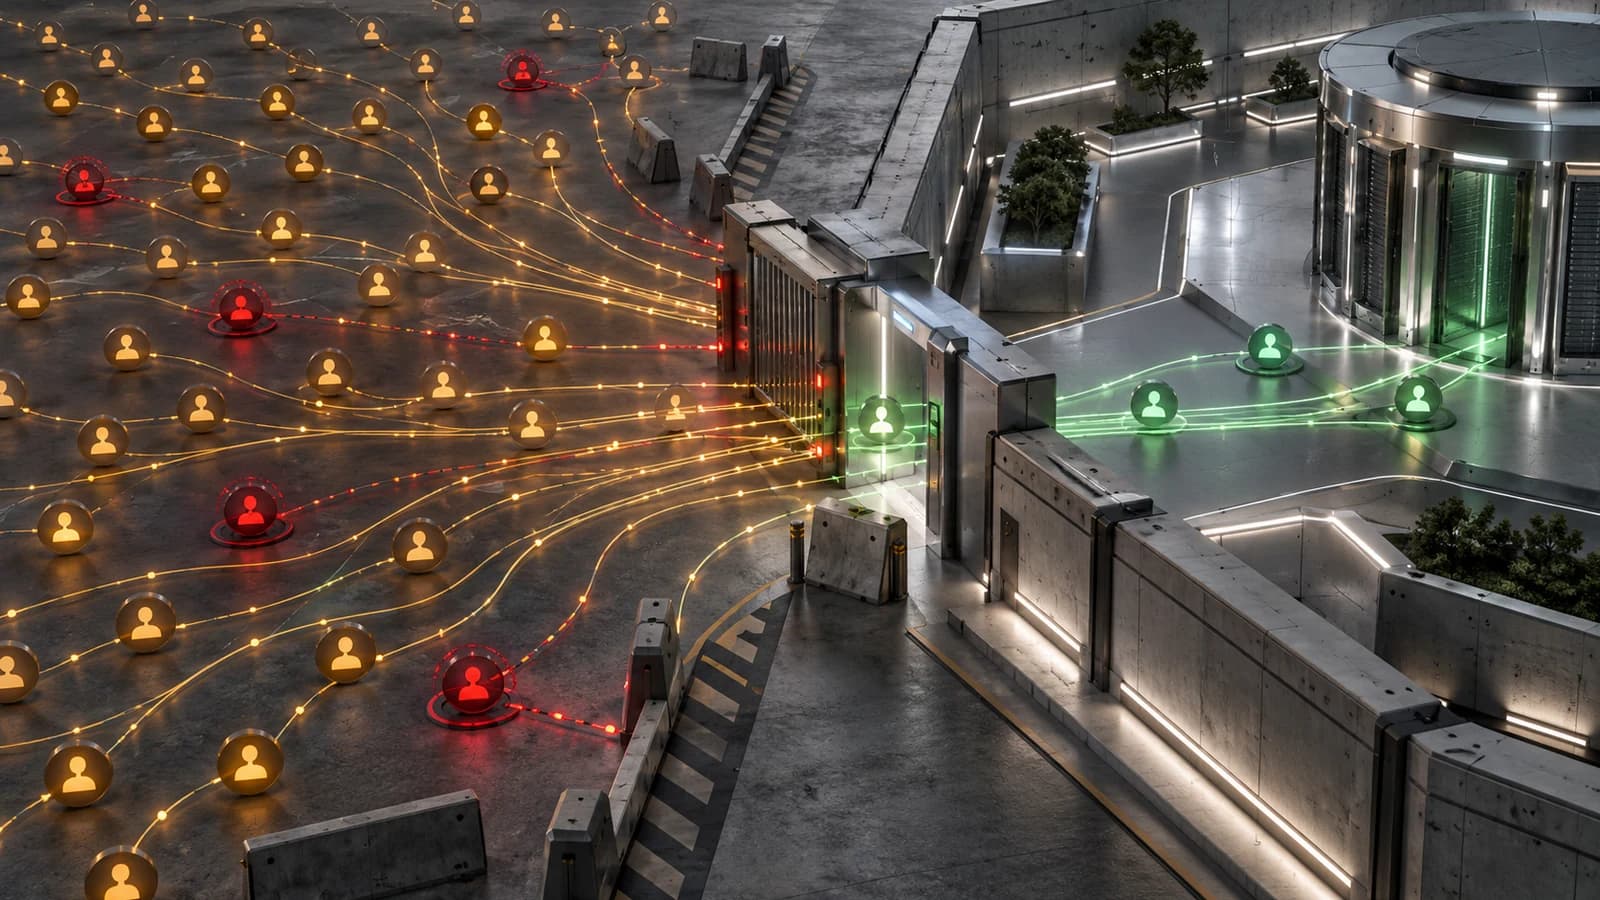
B2B external identity and guest access is the discipline of governing partner, vendor, contractor, and guest identities that are not employees. The 2026 enterprise guide to what external access is, the controls that keep it safe, and the lifecycle that keeps it from becoming a breach path.
- B2B external identity and guest access is the practice of governing partner, vendor, contractor, and guest identities that are not employees, and it is a distinct discipline from workforce IAM because those identities have no HR record, no fixed tenure, and no default reason to exist in your systems.
- The core difference is lifecycle ownership: an employee is provisioned and managed through a full, HR-driven lifecycle, while a guest is scoped, time-boxed, and tied to a sponsor inside your organization who is accountable for why the access exists and when it should end.
- Four controls keep external access safe — a named sponsor and an approval step, scoped least-privilege entitlements, a mandatory expiry date, and periodic recertification — and each one directly counters a way that guest access otherwise drifts out of control.
- The guest access lifecycle runs invite and verify, then scope access, then monitor use, then expire and offboard, and treating it as a real lifecycle rather than a one-time grant is what keeps external identities from accumulating silently.
- Orphaned or never-expiring guest access is one of the most reliable breach paths in the enterprise, because a live credential with no owner and no expiry is exactly the kind of access an attacker looks for and an audit is least likely to catch.
Every enterprise has a perimeter that is far larger than its payroll. Business partners log into shared portals, vendors connect to procurement systems, contractors work inside engineering tools for the length of a project, auditors need read access to financial records for a few weeks, and a supplier's engineer joins a support channel for a single incident. None of these people are employees, yet all of them hold access to systems the organization is responsible for protecting. B2B external identity and guest access is the discipline of granting that access deliberately, keeping it minimal and temporary, and removing it cleanly when it is no longer needed.
This is not a niche corner of identity management. For most enterprises the number of external identities rivals or exceeds the workforce, and unlike employees these identities arrive without the machinery that normally keeps identity honest: no HR system creates them, no role model decides their access, and no termination event removes them. Left to the same processes built for employees, external identities either cannot be provisioned at all or, more often, get created and then quietly forgotten. This guide covers what external identity and guest access are, why they are distinct from workforce IAM, the controls that keep them safe, the lifecycle that governs them end to end, and why the failure mode — orphaned, never-expiring guest access — is one of the most dependable breach paths in the enterprise.
What B2B external identity and guest access means
An external identity is any identity that belongs to a person outside your organization but needs access to systems you control. The category is broad on purpose: business partners collaborating on shared work, vendors and suppliers plugged into procurement or logistics systems, contractors and consultants doing time-limited work inside your applications, professional-services staff from a software vendor, auditors and regulators who need temporary visibility, and one-off guests who join a single meeting, channel, or document. What unites them is that they originate outside your walls — frequently inside another company's directory entirely — and they need a specific, limited slice of your environment for a specific, limited reason.
"Guest access" is the common shorthand for the lightest end of this spectrum: access granted to someone explicitly not a member of your organization, usually scoped to a narrow purpose and expected to be temporary. The distinction between a guest, a partner, and a contractor is mostly one of duration and breadth — a guest might have access for a day, a contractor for a project, a partner for the life of a business relationship — but the governance principle is the same. They are outsiders you are choosing to admit, and that admission has to be accountable, minimal, and reversible.
External identity has become its own field of practice because the modern enterprise runs on collaboration across organizational boundaries. Work no longer happens inside a single company's four walls; it happens across supply chains, partnerships, outsourced functions, and shared platforms, and every one of those relationships creates identities that need to reach into someone else's systems. The organizations that handle this well treat external access as a first-class thing to govern. The ones that handle it badly treat each grant as a favor — a quick account created to unblock someone — and never look at it again.
Why external identity is distinct from workforce IAM
Workforce identity and access management is built on three assumptions, and external identities violate all three.
The first assumption is an authoritative source of truth. Employee identity flows from an HR system: a person is hired, a record is created, and that record drives account creation and, later, deactivation. External identities have no such source. A partner's engineer does not appear in your HR feed, so no system automatically knows they exist or, crucially, knows when they stop being relevant. The event that ends an employee's access — a termination processed in HR — has no equivalent for a contractor whose project simply wraps up.
The second assumption is a role model. Workforce access is typically governed by mapping jobs to bundles of entitlements, so a person's role determines what they can reach. External identities do not fit that structure. A vendor's support engineer is not a "role" in your organization; a guest auditor does not map to any internal job. Forcing external identities into workforce roles tends to over-grant them, because those roles were designed for the breadth an employee needs, not the pinhole an outsider should get.
The third assumption is a manager. Every employee has one — someone accountable for them, who reviews their access and owns their offboarding. External identities have no internal manager by default. They belong to another organization, and inside yours they belong to no one unless you deliberately assign an owner. Access that belongs to no one is access that never gets reviewed and never gets removed.
Because external identities break all three assumptions, they need their own governance model: a sponsor in place of a manager, scoped grants in place of role inheritance, and an explicit expiry in place of a termination event. Running guests through the employee pipeline unmodified is how organizations end up with thousands of external accounts that no process is responsible for ending. The disciplines of automated user provisioning still apply — external accounts should be created consistently and configured correctly — but they have to be wired to external triggers and rules rather than the HR-driven flow that governs employees.
Employee versus guest: managed lifecycle versus scoped, time-boxed, sponsor-tied access
The clearest way to understand external identity is to put an employee and a guest side by side. An employee has a managed lifecycle. They enter through HR, are provisioned automatically based on their role, receive broad standing access to do their job, are reviewed periodically as part of the workforce, and are deprovisioned when a termination event fires. The system does the work: the identity is created, maintained, and ended by processes that assume the person is a long-term member of the organization.
A guest has none of that by default, so each piece has to be supplied deliberately. A guest is scoped: rather than inheriting a role built for an employee, they are granted only the specific access their purpose requires. A guest is time-boxed: instead of standing access that persists until a termination event, their access carries an expiry date from creation, so it ends on its own even if nobody remembers to remove it. And a guest is sponsor-tied: instead of a manager who owns them, they are attached to a named internal employee who requested or approved the access and is accountable for confirming it is still needed.
Those three properties — scoped, time-boxed, sponsor-tied — are the entire difference. They are not about trusting guests less as people; many external partners are highly trusted. They are about the fact that external access has no natural owner and no natural end, so both must be manufactured. Where employee access is safe because the system manages it, guest access is safe only because you explicitly governed it. Remove the scope and a guest is over-privileged; remove the expiry and a guest is permanent; remove the sponsor and a guest is orphaned. All three failures happen constantly, and all three are avoidable.
The controls that keep external access safe
Four controls, working together, are what turn a risky pile of outsider accounts into governed external access. Each one directly counters a specific way that guest access otherwise drifts out of control.
Sponsorship and approval
Every external identity should be tied to a named internal sponsor and pass through an approval step before it is created. The sponsor is the accountable owner — the answer to the auditor's inevitable question: who inside this organization is responsible for this person being here? Because external identities have no manager and no HR record, the sponsor takes on that role: they approve the initial grant, receive the recertification requests over time, and inherit the responsibility to end the access when the engagement is over. Running external requests through a proper self-service access request workflow — routed to a sponsor rather than a manager — is what turns "someone made an account for a vendor once" into an auditable decision with an owner.
Scoped least-privilege entitlements
External identities should receive the minimum access their purpose requires, and nothing more. In practice this means giving them their own narrow entitlement sets rather than dropping them into broad groups designed for employees. A contractor working on one application should reach that application and its related data — not the general employee collaboration suite, not systems adjacent to their task, not standing access they might "need later." Least privilege is doubly important at the boundary because the credential is managed outside your control and, if compromised, you want the blast radius to be as small as possible.
Time-boxed expiry
Every external grant should carry an expiry date from the start. This is the single most powerful control in external identity, because it changes the default. With expiry, access ends automatically unless someone deliberately extends it; without expiry, access persists forever unless someone deliberately removes it — and someone rarely does. Time-boxing matches access to the shape of the relationship: a guest gets days, a contractor a project window, a partner a renewable term. Where the technology allows, just-in-time access takes this further, granting elevated permissions only while they are actively used and reclaiming them immediately after. External access should be temporary by construction, not by good intentions.
Periodic recertification
Even scoped, time-boxed access needs to be reviewed while it is live, because relationships change faster than expiry dates. Periodic recertification sends each external identity's access back to its sponsor on a schedule and asks a direct question: is this person still engaged, and do they still need this access? Entitlements that are no longer required get removed; identities whose engagement has ended get revoked. Recertification is the safety net that catches what time-boxing and sponsorship missed — the contractor still technically within their window but finished two months ago, the partner whose scope quietly expanded. An effective review is a real decision, not a rubber stamp; the difference between the two, and what makes reviews withstand scrutiny, is the subject of what an auditor actually wants from an access review.
The guest access lifecycle
External access is best understood not as a grant but as a lifecycle with four stages. Each stage has an owner and a purpose, and the discipline is in making sure the last stage actually happens.
Invite and verify. The lifecycle begins when a guest is created. This is where sponsorship and identity verification belong: the external person is invited, their identity is confirmed to a degree appropriate to what they will access, and a named internal sponsor is attached from the outset. Getting this stage right means no external identity is ever created without an owner and a verified starting point.
Scope access. Once the identity exists, it is granted access — and this is where least privilege is enforced. The guest receives the specific entitlements their stated purpose requires, ideally with an expiry attached to each grant, and nothing adjacent. Scoping at creation is far easier than clawing access back later, so granting little and expanding only on request pays off across the whole lifecycle.
Monitor use. While the access is live, it should be watched. Activity gets logged, unusual behavior gets flagged, and — just as importantly — access that is granted but never used gets surfaced. Unused external access is a strong signal that the grant was too broad or is no longer needed, and a candidate for early removal.
Expire and offboard. The lifecycle ends when the access does. At the expiry date, or when the engagement closes, the access is removed and the account is deactivated and cleaned up. This is the stage organizations skip, and skipping it is what produces every orphaned account in the environment. Reliable offboarding is a governance function in its own right; the mechanics of ending access cleanly, completely, and on time are covered in automated deprovisioning and offboarding, and they apply to external identities with even more urgency than to employees, because nothing else will catch a guest who is never removed.
The lifecycle framing matters because it reframes external access as something always moving toward an end, rather than a favor granted once and forgotten. When every external identity is somewhere on this arc, and the final stage is guaranteed to fire, guest access stops accumulating.
Why orphaned or never-expiring guest access is a top breach path
The failure mode of external identity has a name: orphaned access. It is access that has outlived its purpose — the contractor whose project ended six months ago, the partner whose contract lapsed, the vendor account created for a one-time integration that no one remembers. Orphaned external access is not an edge case; it is the predictable result of granting guest access without an expiry and without recertification. Grant enough accounts that way, over enough years, and an organization accumulates a shadow population of live credentials that belong to no one.
This is dangerous for reasons that compound. An orphaned external identity has no owner, so no one is watching it or will notice if it is misused. It has no expiry, so it stays live indefinitely. And it sits at an organizational boundary, which means the credential may be managed loosely on the other side, shared among people you cannot see, or left behind on an unmanaged device when the external person moved on. Each of those is a problem on its own; together they describe an ideal target. A live, unwatched, externally held credential grants an attacker a foothold that blends in with legitimate traffic and raises no internal alarms, because as far as your systems know, a valid partner is simply logging in.
Attackers understand this better than most organizations do. Compromising an external identity is often easier than compromising an employee — the account may sit outside your strongest controls, the person behind it may not be subject to your security training, and the credential may be reused across the external party's own environment. Once inside, an attacker using an orphaned account operates with legitimate access that no one is accountable for, which is exactly why it takes so long to detect. A great deal of the identity risk in incident reports traces back not to sophisticated attacks but to access that should not have existed anymore.
The defense is the whole discipline described in this guide, stated plainly: no external identity should exist without a sponsor, a scope, an expiry, and a review. When those four controls are enforced consistently — and the lifecycle guarantees that the offboarding stage actually fires — orphaned access has nowhere to accumulate. The organizations that suffer external-access breaches are almost never the ones that governed these identities and lost anyway; they are the ones that never governed them at all.
Bringing external identity under governance
Governing B2B external identity does not require a separate universe of tooling. It requires applying the core disciplines of identity governance — provisioning, access request, entitlement scoping, certification, and deprovisioning — with rules built for outsiders rather than employees: guest accounts created consistently, requests routed to a sponsor instead of a manager, narrow purpose-built entitlements instead of workforce roles, expiry built into every grant, recertification sent to sponsors on a schedule, and access reliably removed when an engagement ends. An identity governance platform ties these together so that every external identity carries a sponsor, a scope, an expiry, and a review, with an audit trail showing who approved what and when it ended.
Avatier approaches external identity as an extension of the same governed lifecycle it applies to the workforce, adapted to the reality that guests, partners, and contractors have no HR record and no internal manager. Identity Anywhere lets external access be requested, sponsored, and approved through the same self-service and workflow layer used for employees, provisions and deprovisions external accounts through lifecycle automation, scopes them to least-privilege entitlements rather than broad workforce roles, and brings them into access certification so sponsors periodically confirm the access is still warranted. The aim is a single governed model in which no identity — internal or external — holds access without an accountable owner and a defined end.
That posture rests on an audited assurance program. Avatier is SOC 2 Type II with zero exceptions, ISO/IEC 27001:2022 certified, PCI DSS v4.0.1 compliant, and CSA STAR Level 1, with a platform aligned to NIST 800-53 Rev. 5, built FedRAMP-aligned, delivered as a signatory of CISA's Secure-by-Design Pledge, and FIDO2-compatible for phishing-resistant authentication. You can review the current attestations and status at the Avatier Trust Center. External identity is where an organization's trust boundary is most exposed, which is why the assurance around the platform governing it matters as much as the controls themselves.
Conclusion
B2B external identity and guest access lives at the edge of the organization, where the tidy assumptions of workforce IAM stop holding. Partners, vendors, contractors, and guests arrive with no HR record, no role, and no manager, so they need a governance model of their own: a sponsor who owns them, a scope that limits them, an expiry that ends them, and a review that keeps them honest. Run those controls across a real lifecycle — invite and verify, scope access, monitor use, expire and offboard — and external access becomes what it should be: accountable, minimal, and temporary. Skip them, and it becomes what it too often is: a growing population of orphaned credentials that no one owns and attackers reliably find. The difference between the two outcomes is not sophistication. It is whether the organization decided to govern the identities it admits from outside, or simply let them in.
ABOUT THE AUTHOR
More from Access Management
Identity Federation Explained: The 2026 Foundational Guide
Identity federation is a trust relationship between separate identity providers so that one login works across domains and organizations. The foundational 2026 reference on what federation is, how it differs from SSO, and the protocols that carry it.
Identity Verification and Proofing: The 2026 IDV Guide
What identity verification and proofing actually are, how they differ from authentication, the four proofing methods, and how remote onboarding really works — establishing who someone is before you ever hand them a credential.
Device Trust and Posture in Access Decisions 2026
Device trust factors the health of the endpoint — managed vs unmanaged, patch level, disk encryption, EDR status — into every access decision, so that a correct password on a compromised laptop no longer buys the same access as a correct password on a verified device. The 2026 enterprise reference on posture-driven access outcomes: healthy allows, risky limits or steps up, non-compliant blocks.