Locked Out Off VPN: Remote Password Reset with Avatier Login Reset
A remote worker forgets or resets a domain password off VPN and is stuck at the login screen with stale cached credentials. How Avatier Login Reset brings MFA-verified recovery home.
IT operations leaders cutting password reset and identity verification ticket volume.
Showing 41

A remote worker forgets or resets a domain password off VPN and is stuck at the login screen with stale cached credentials. How Avatier Login Reset brings MFA-verified recovery home.

A group membership request is routine work that leaves sprawl behind when nobody sets an end date. How to run each change with an owner, a policy, and a record, and how Avatier does it.

MFA at the SAML layer leaves Windows login, RDP and server logons on a password alone. Avatier Strong MFA Login binds the factor you already own to every password authentication event.

Password spraying tries a few common or breached passwords across many accounts, spread thinly enough to dodge lockout. The defense is to screen every new password before it can be set.

The Avatier MCP server is live at mcp.avatier.com. Connect Claude, Claude Code, GitHub Copilot, Cursor or Gemini CLI and run governed identity actions in plain language, with the same verification, policy and approvals as the Avatier console.

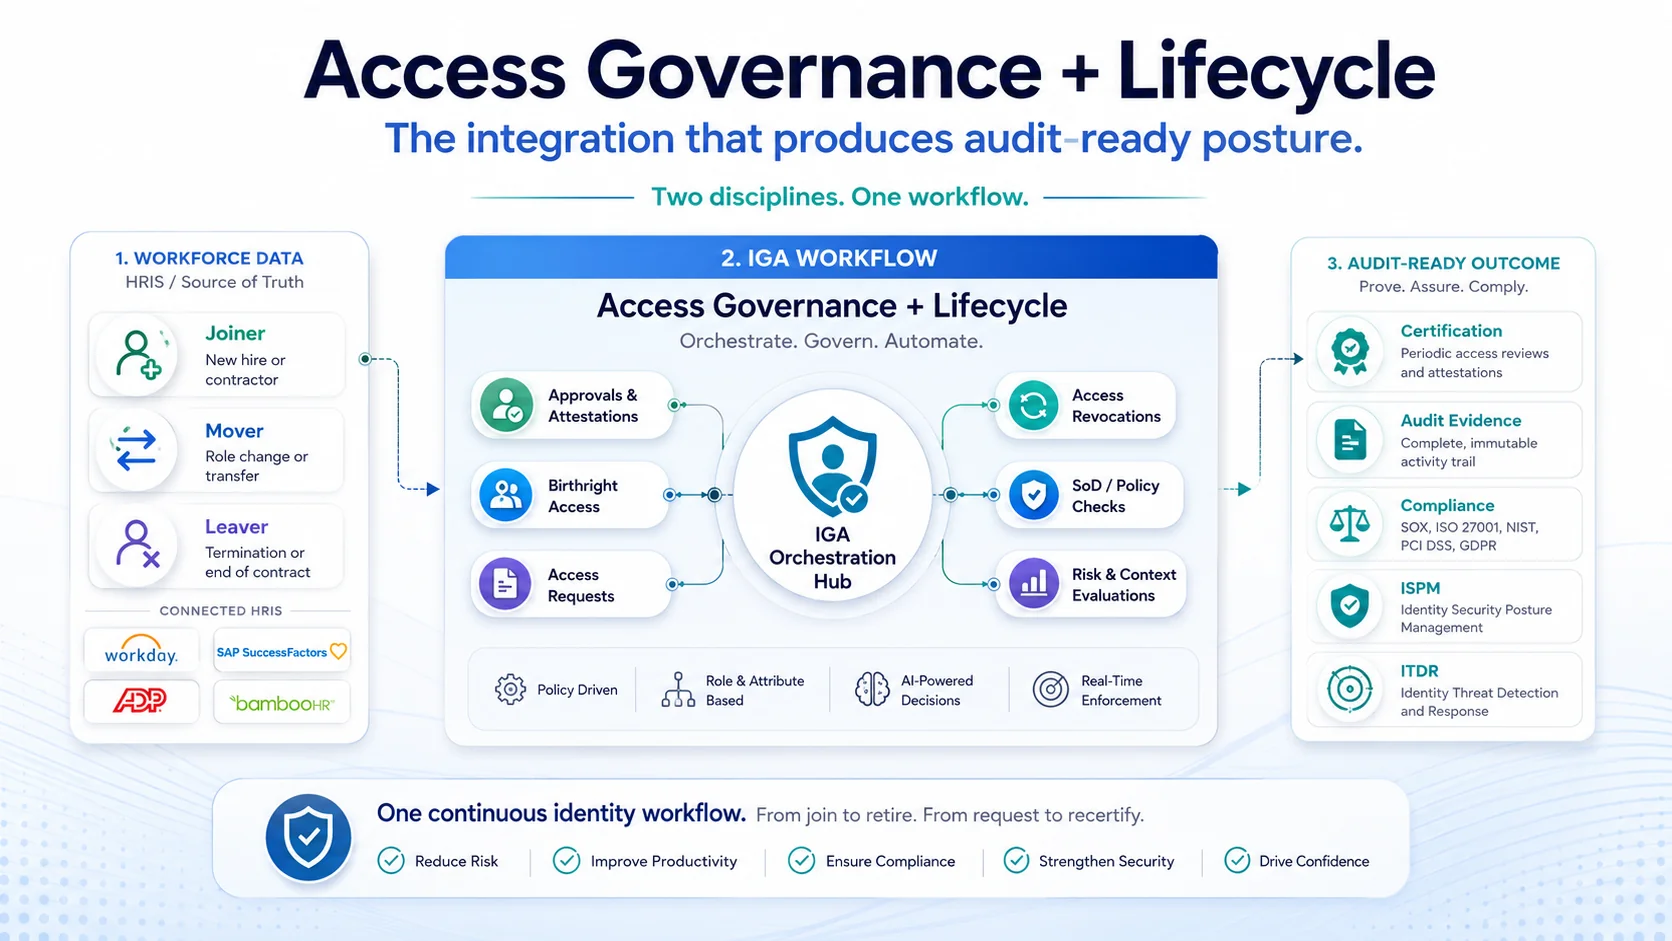
Joiner-mover-leaver automation runs every lifecycle change as a governed identity action. Why movers are where access piles up, and how Avatier runs changes through policy.

Help desk social engineering works because an agent has to judge whether a caller is real. The defense is to move that decision to the user's own device, so the agent sees only pass or fail.

AI service desk automation resolves unlocks, resets, access and group changes by conversation, through governed identity actions. What to automate, what to route, and how Avatier does it.

You already know the groups have sprawled. This is the remediation program that reverses it: discovery, ownership assignment, consolidation order, and deletion with a rollback window.

A correctly built access request portal still goes unused when the storefront layer is missing — this is the 2026 playbook for browse, search, bundled checkout, status transparency, and re-request.

Fulfillment time is the elapsed interval between a user asking for access and that access actually working — and most organizations measure it wrong, because they stop the clock when the ticket closes. This is the 2026 method for defining the clock, attributing the wait, and deciding which delays are worth engineering out.

What identity verification and proofing actually are, how they differ from authentication, the four proofing methods, and how remote onboarding really works — establishing who someone is before you ever hand them a credential.

Device trust factors the health of the endpoint — managed vs unmanaged, patch level, disk encryption, EDR status — into every access decision, so that a correct password on a compromised laptop no longer buys the same access as a correct password on a verified device. The 2026 enterprise reference on posture-driven access outcomes: healthy allows, risky limits or steps up, non-compliant blocks.

Deprovisioning is the revoke side of the identity lifecycle: a leaver event that cascades revocation across every connected system so no active account, live session, or token outlives the person.

A single impersonation call to a help desk — not a firewall failure — triggered a 2023 casino-industry breach that cost roughly $100 million, and the fix is verification discipline, not new firewalls.

Federal agencies pass FISMA audits every year and still get breached — the identity governance gaps assessors keep missing are the same ones attackers exploit.

Mandatory password rotation on a fixed calendar is no longer best practice — NIST SP 800-63B favors length and breach screening over forced expiration, and here's what to do instead.

RACF grants access through groups, not users: ADDGROUP builds it, CONNECT enrolls the user, PERMIT binds it to a resource. How assignments, nested membership, and access decisions resolve in 2026.

LDAP is the read-optimized directory protocol still sitting under most enterprise IAM stacks — here is how its structure, bind and search, LDAPS, replication, and schema actually work in production.

Connecting a modern IAM platform to the applications you already run is a connector problem before it's a strategy problem — SCIM, LDAP/AD, SAML/OIDC, and API or agent connectors, matched to what each app can actually speak.

RACF enforces password complexity, expiration, history, and lockout through SETROPTS PASSWORD suboperands — RULEn, INTERVAL, HISTORY, and REVOKE. The 2026 reference on the exact syntax, why PCI-DSS and SOX still mandate it even as NIST 800-63B moves the industry away from rotation and composition rules, and where RACF-level enforcement alone stops being enough.

RACF user provisioning becomes reliable when create, entitle, and deprovision actions trigger directly off HR events instead of tickets — here's how that pattern actually works on the mainframe.

AI-driven adaptive controls cut security friction by moving verification into passive signals instead of adding prompts — the 2026 reference on invisible security.

SCIM is the RESTful, JSON-based standard that automates identity provisioning and deprovisioning between a source of truth and downstream apps. What it is, how it works, and where it fits in IGA.

Self-service access requests only work when the full workflow is designed as one governed loop — request capture, policy-driven approval routing, automated provisioning, and closed-loop access confirmation. This is the 2026 practitioner guide to implementing an access request system that is fast for users and defensible under audit: the request-to-access pipeline, the design decisions that keep self-service from becoming rubber-stamp risk, and the operational discipline that makes it hold up.

Self-service password management lets workforce users reset and recover their own credentials through a verified, audited workflow instead of a help-desk call. This 2026 expert guide is the orienting evaluation lens — what the category actually is, what 'good' looks like, the questions to ask when you evaluate it, and the failure modes to screen for — with deployment mechanics, general how-to, and vendor comparison handled in dedicated companion pieces.

A break-glass account is a pre-provisioned, tightly governed emergency credential that grants high-privilege access when normal authentication paths are unavailable — during an outage, an admin lockout, or a disaster-recovery scenario. The 2026 reference on what break-glass means in technology, when to invoke it, and the approval, auditing, time-boxing, and rotation controls that keep the emergency credential from becoming a standing back door.

Password resets are usually the single largest category of help-desk contacts — and the most reducible. This 2026 update covers the help-desk KPIs that actually matter for identity and password support, how to baseline them, and the specific levers — self-service reset, password synchronization, MFA-verified reset, and passwordless — that cut reset ticket volume and cost. Plus the hardened path for the tickets that remain, and an honest look at what the KPIs do not tell you.

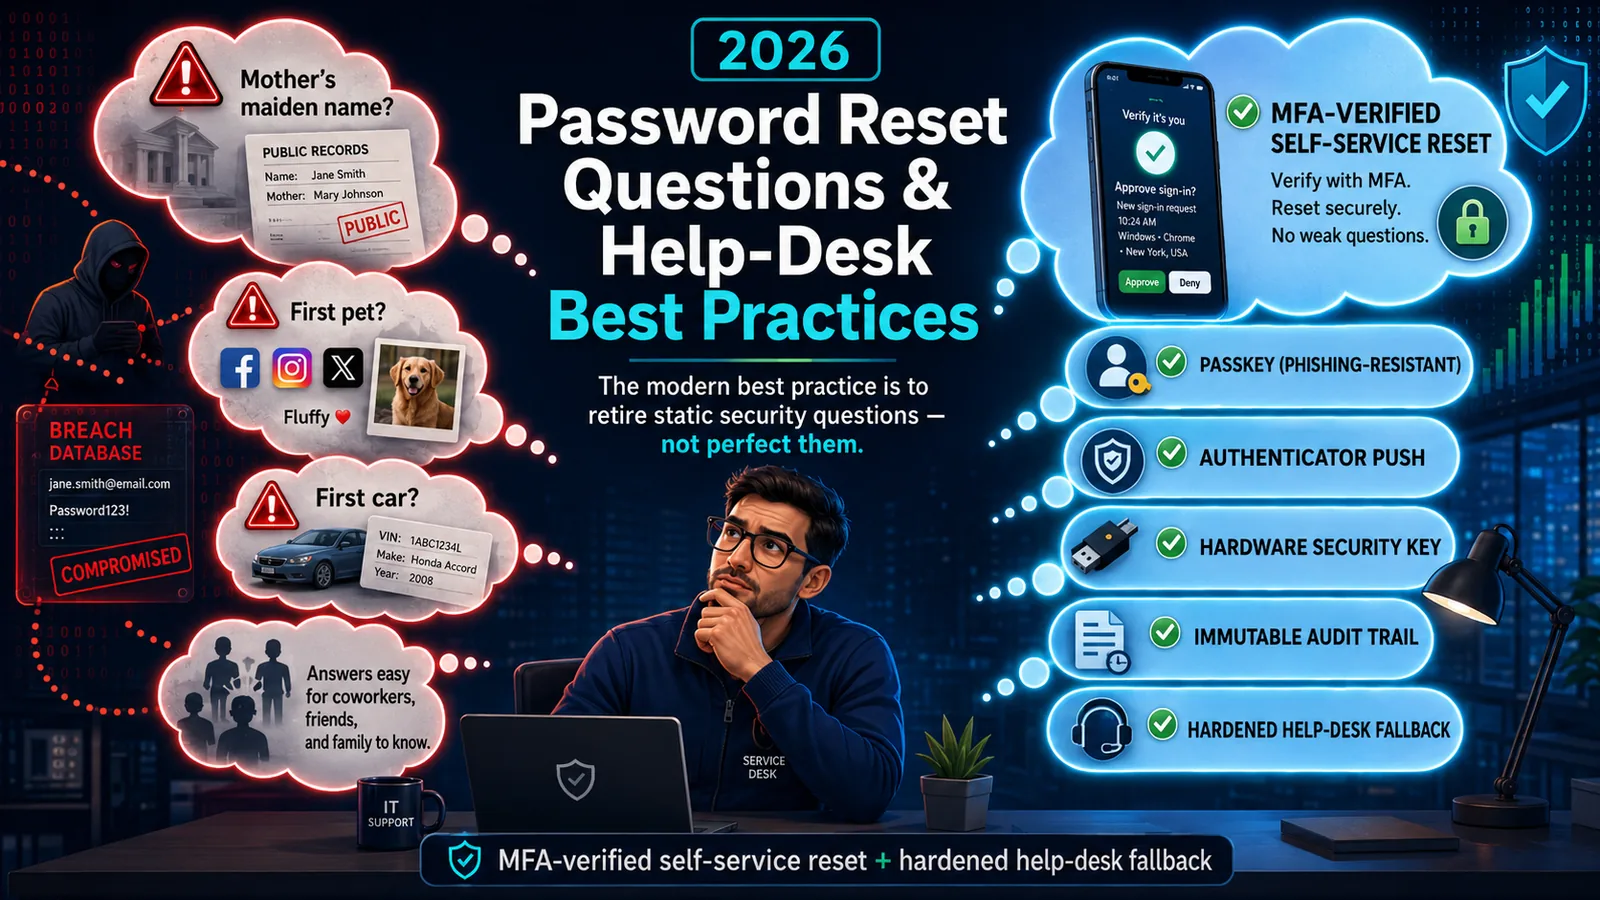
Static security questions are the weakest link in password reset — OSINT-discoverable, shared, and breach-exposed. The 2026 best practice: retire them for MFA-verified self-service reset.

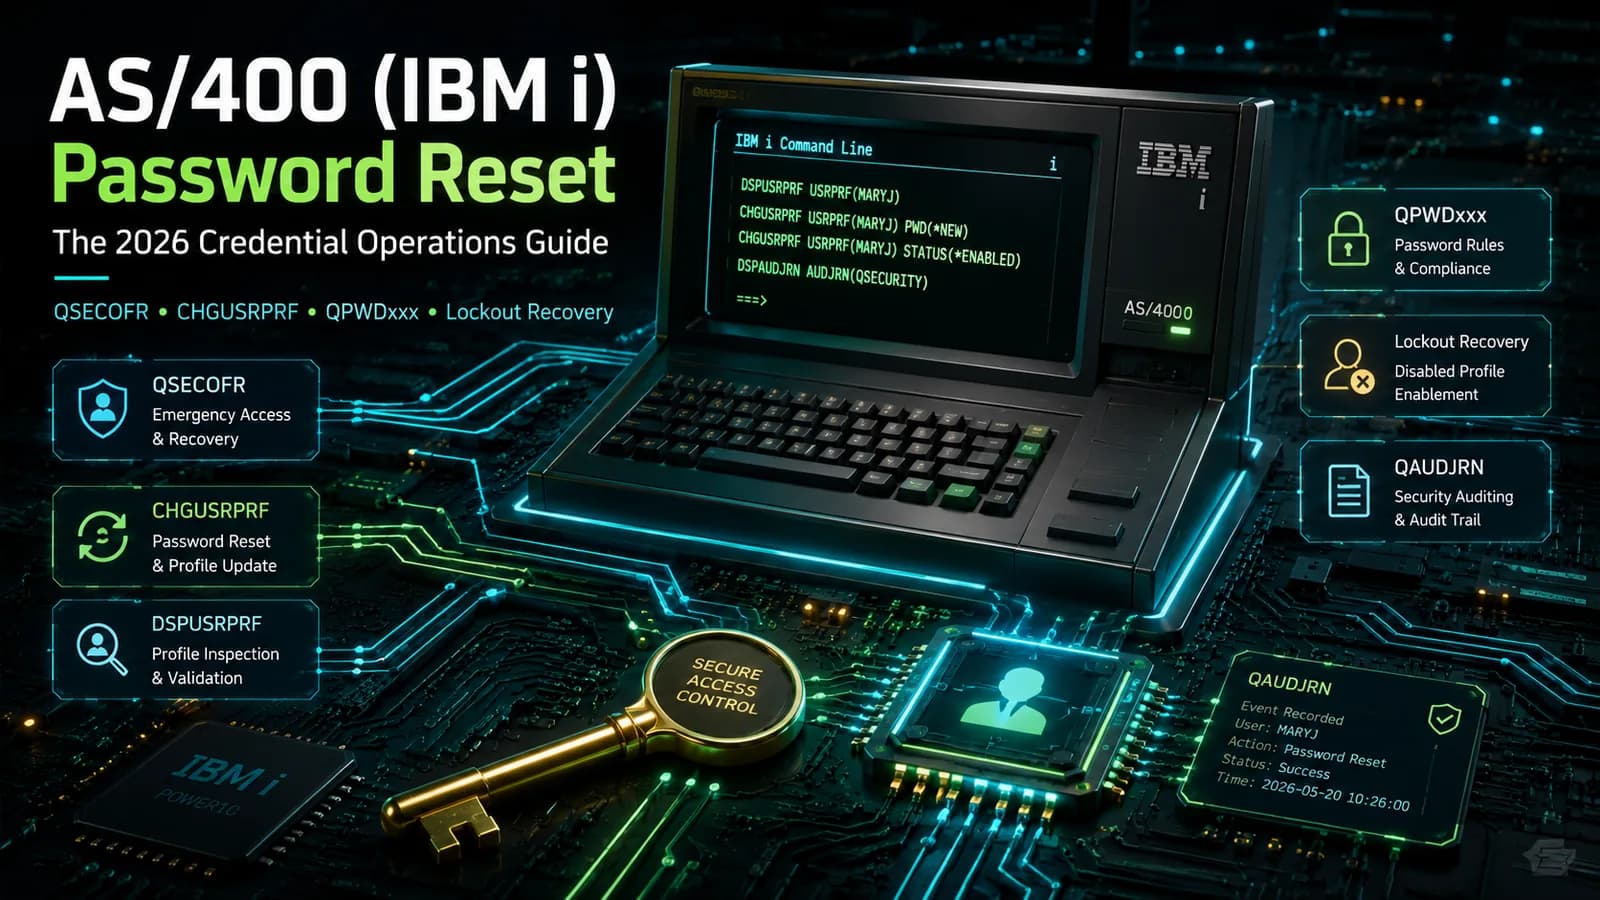
How password reset works on AS/400 (IBM i) — QSECOFR, user profiles, CHGUSRPRF, the QPWDxxx system values, disabled-profile recovery, and the hardening that keeps reset from becoming the weakest link.

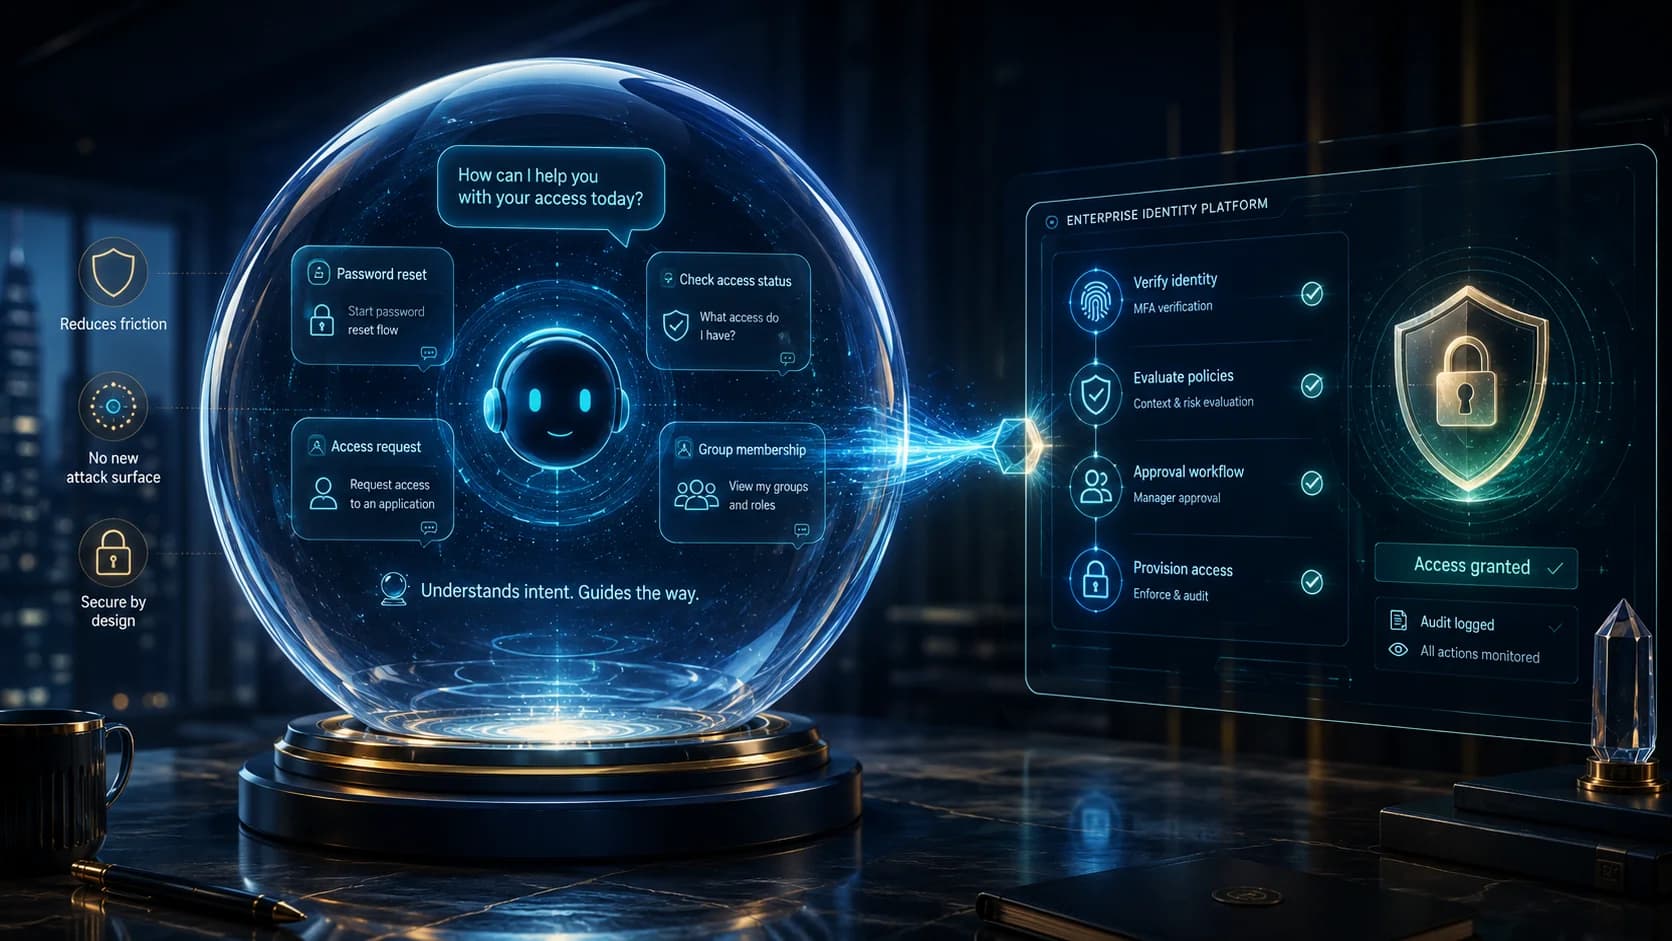
A chatbot that resets passwords is trivial to build and a genuinely bad idea — because the hard part of a password reset was never the conversation, it was proving who is asking. The 2026 reference on conversational identity done properly: the four workflows worth deflecting to chat, why identity verification must live outside the language model, the prompt-injection and social-engineering surface a naive deployment opens, and the deflection math against a $480-per-employee support baseline.

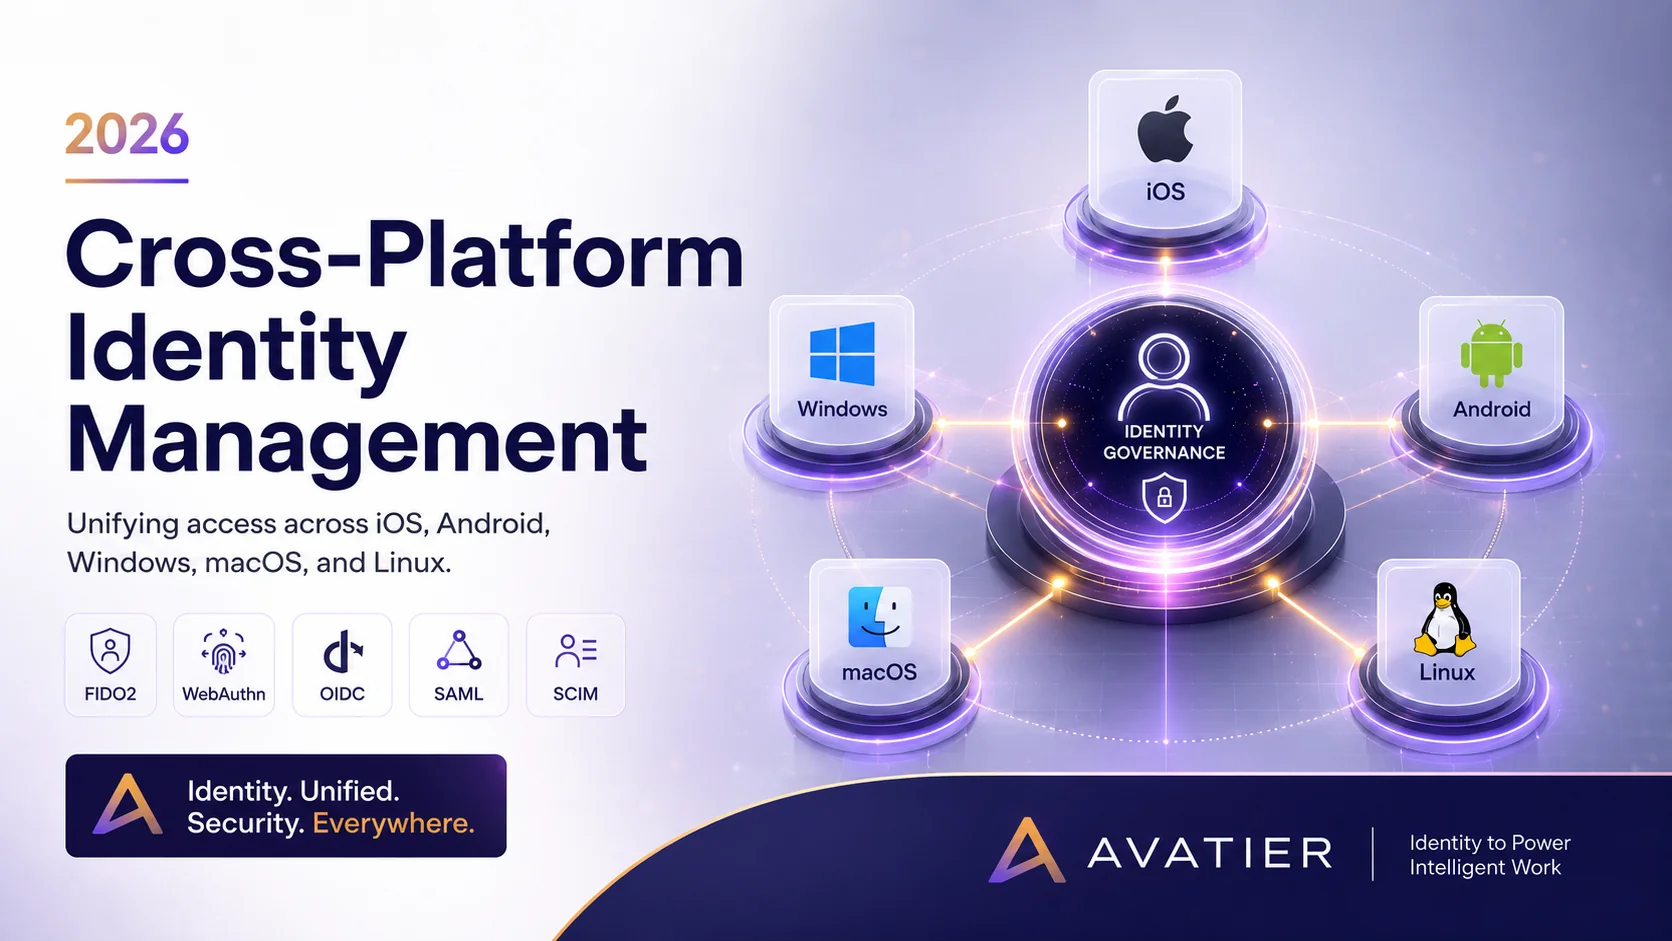
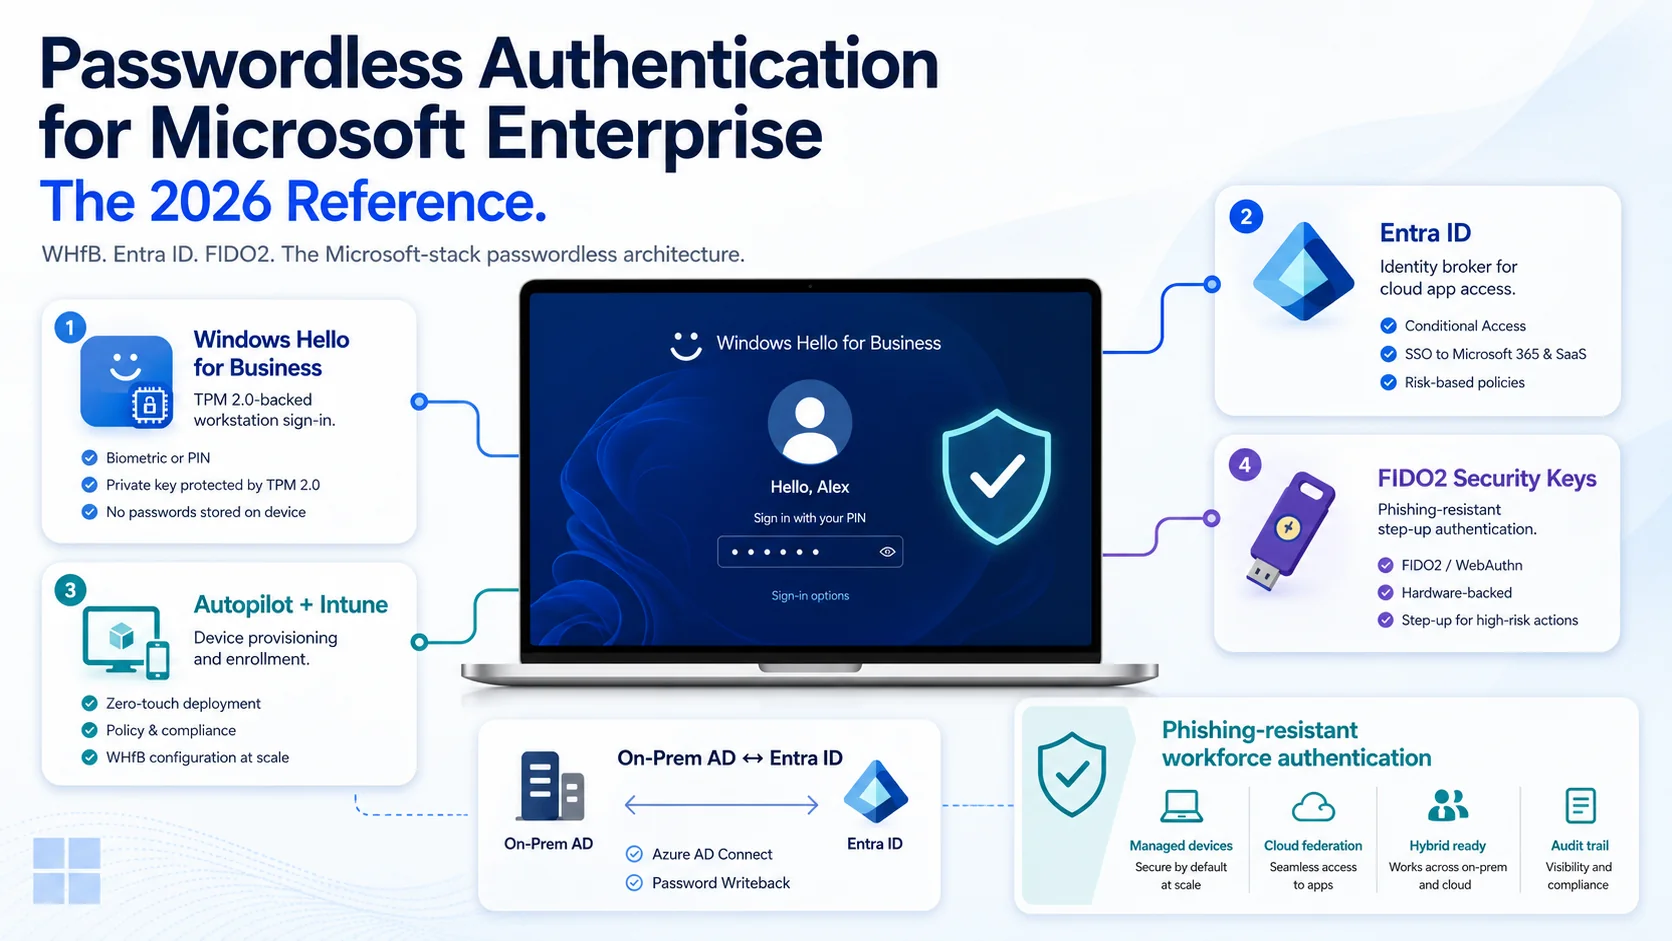
The average enterprise workforce now authenticates from three or more platforms daily — iOS, Android, Windows, macOS, Linux, and shared frontline devices — and every platform ships its own credential store, biometric stack, and passkey ecosystem. The 2026 reference on unifying identity across all of them: the platform-agnostic architecture, the passkey fragmentation problem nobody warned you about, per-platform security capability mapping, the workforce segments platform-bound authentication leaves behind, and the deployment discipline that produces one identity experience instead of five.
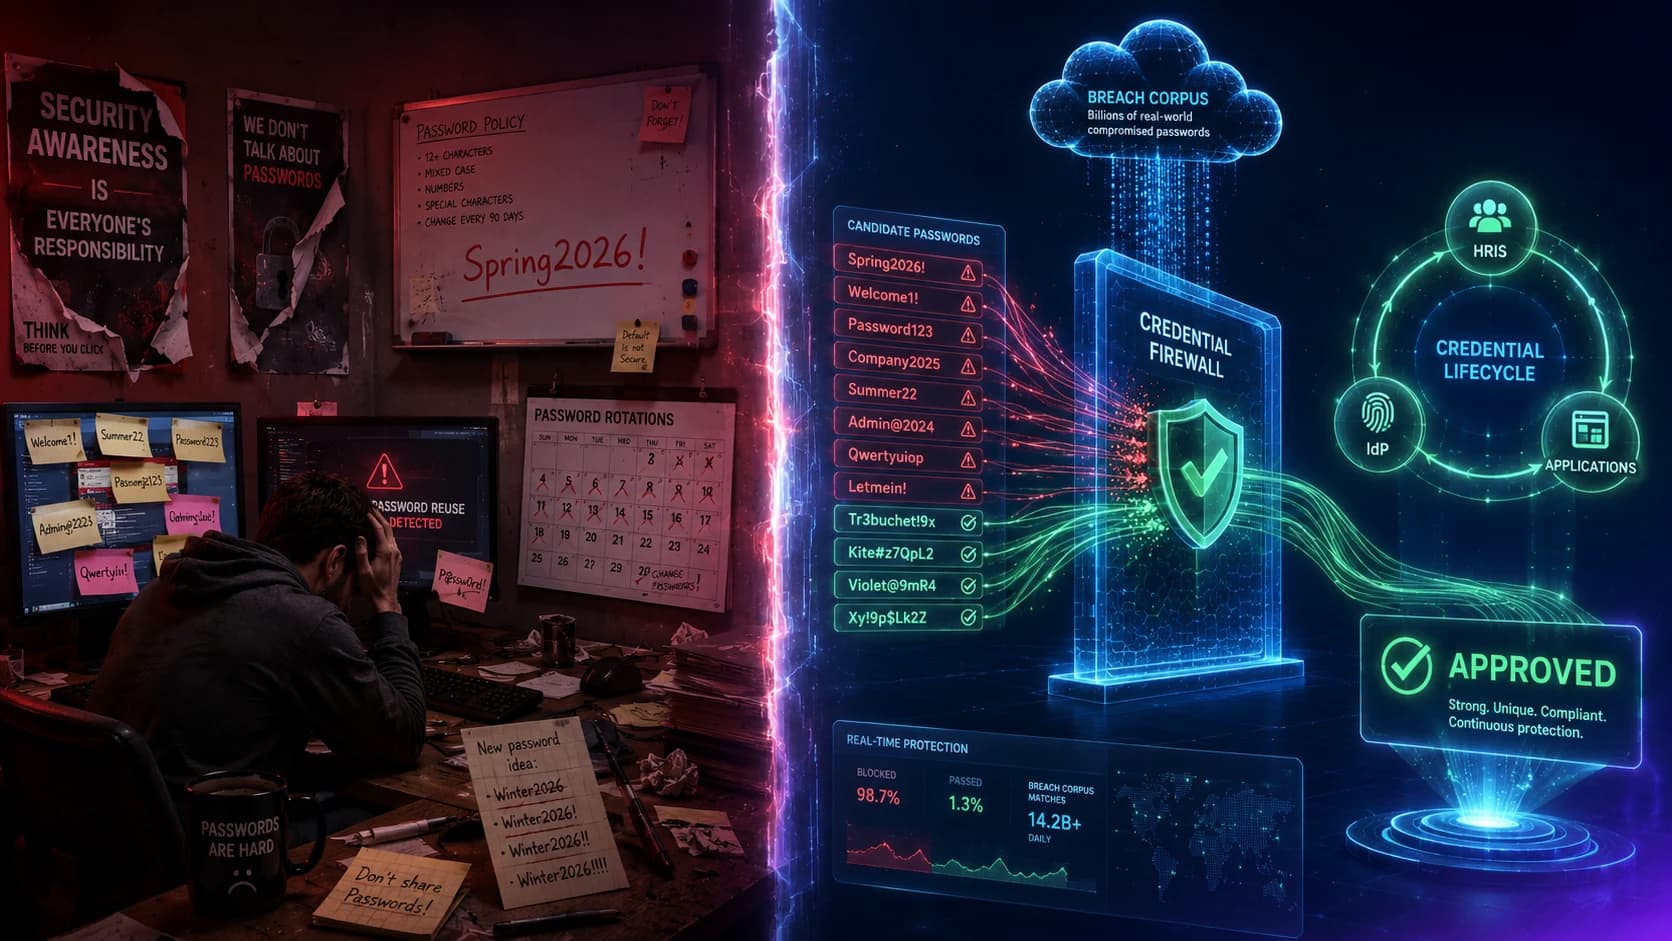
Why weak passwords persist in 2026 despite decades of training — and the policy-enforcement, credential-firewall, and lifecycle controls that eliminate them at scale.

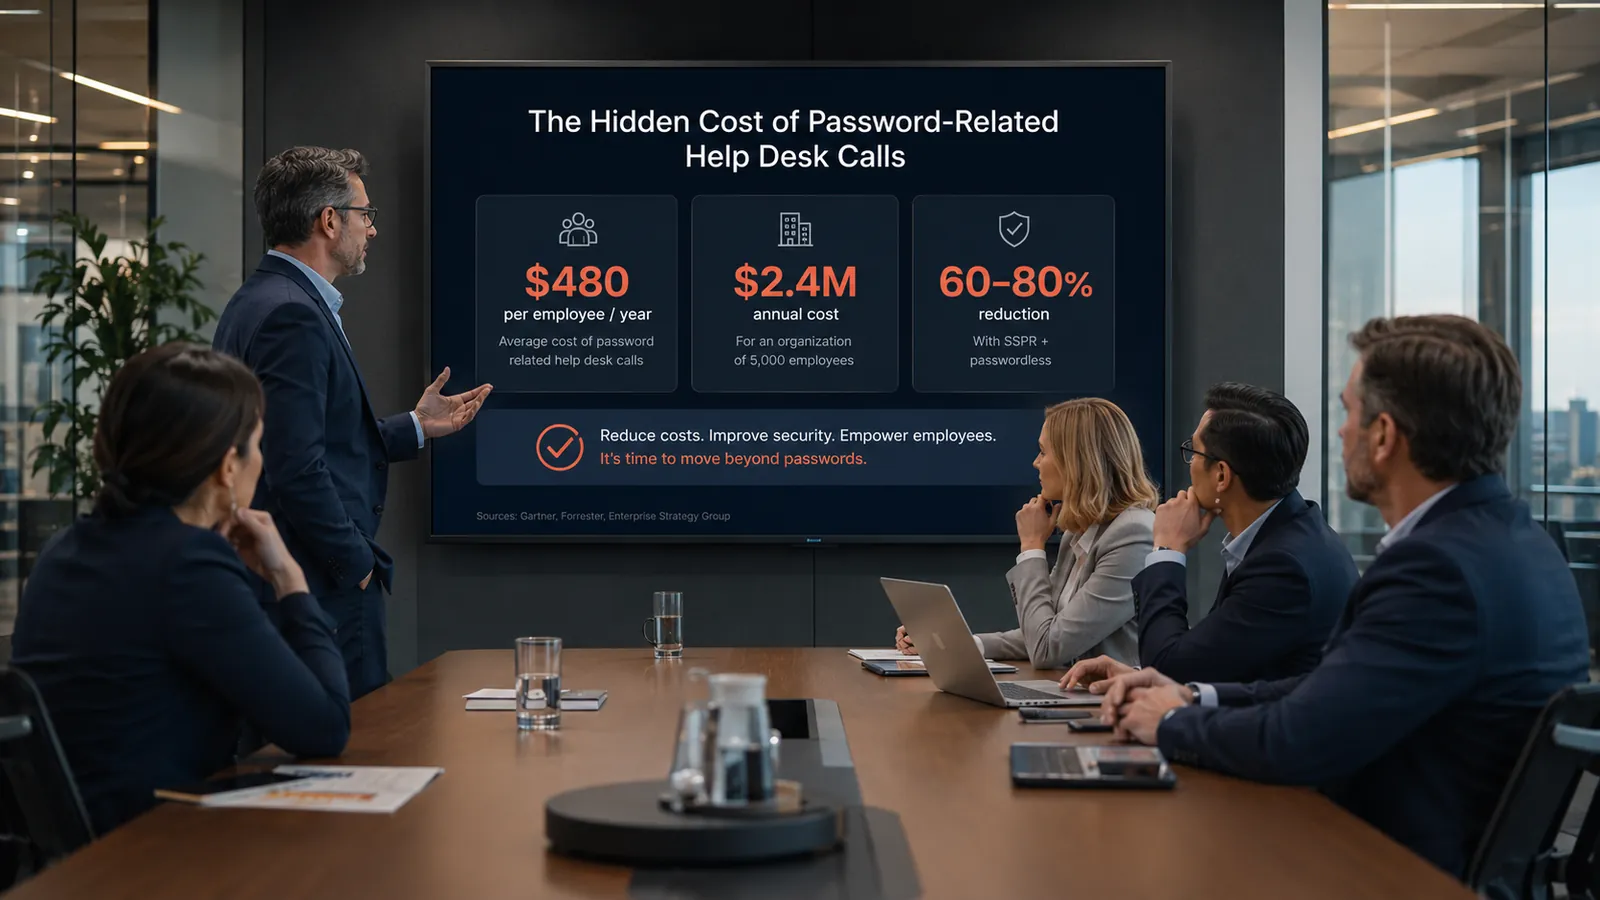
Password-related help desk calls cost the average enterprise $480 per employee per year — a hidden line item that dominates IT operational cost at scale and produces $2.4M in annual burn for a 5,000-employee enterprise. The 2026 enterprise reference on the specific cost components, the volume drivers that scale the number by industry, the SSPR and passwordless architectural interventions that reduce it 60-80%, and the CFO-defensible ROI model that justifies the reduction investment.

Self-service password reset (SSPR) is the operational lever that moves enterprise password reset economics from $70-per-ticket help-desk-only to 60-80% ticket-volume reduction — when deployed with modern authenticator-based verification, coverage across the domain workstation and frontline segment cases, and audit-trail integration that satisfies SOX / PCI-DSS / HIPAA. The 2026 enterprise reference on SSPR deployment architecture, the five configuration elements that determine effectiveness, and the vendor-neutral comparison discipline for SSPR selection.

Active Directory login reset for domain-joined Windows workstations is the specific reset architecture where users can't reach a self-service portal because they can't log in at all. The 2026 enterprise reference on the pre-login reset architecture, the Windows CredentialProvider integration, the on-premises AD versus Entra ID hybrid patterns, the compliance requirements that shape domain reset workflow, and the deployment discipline that keeps AD reset defensible under SOX and PCI-DSS audit.
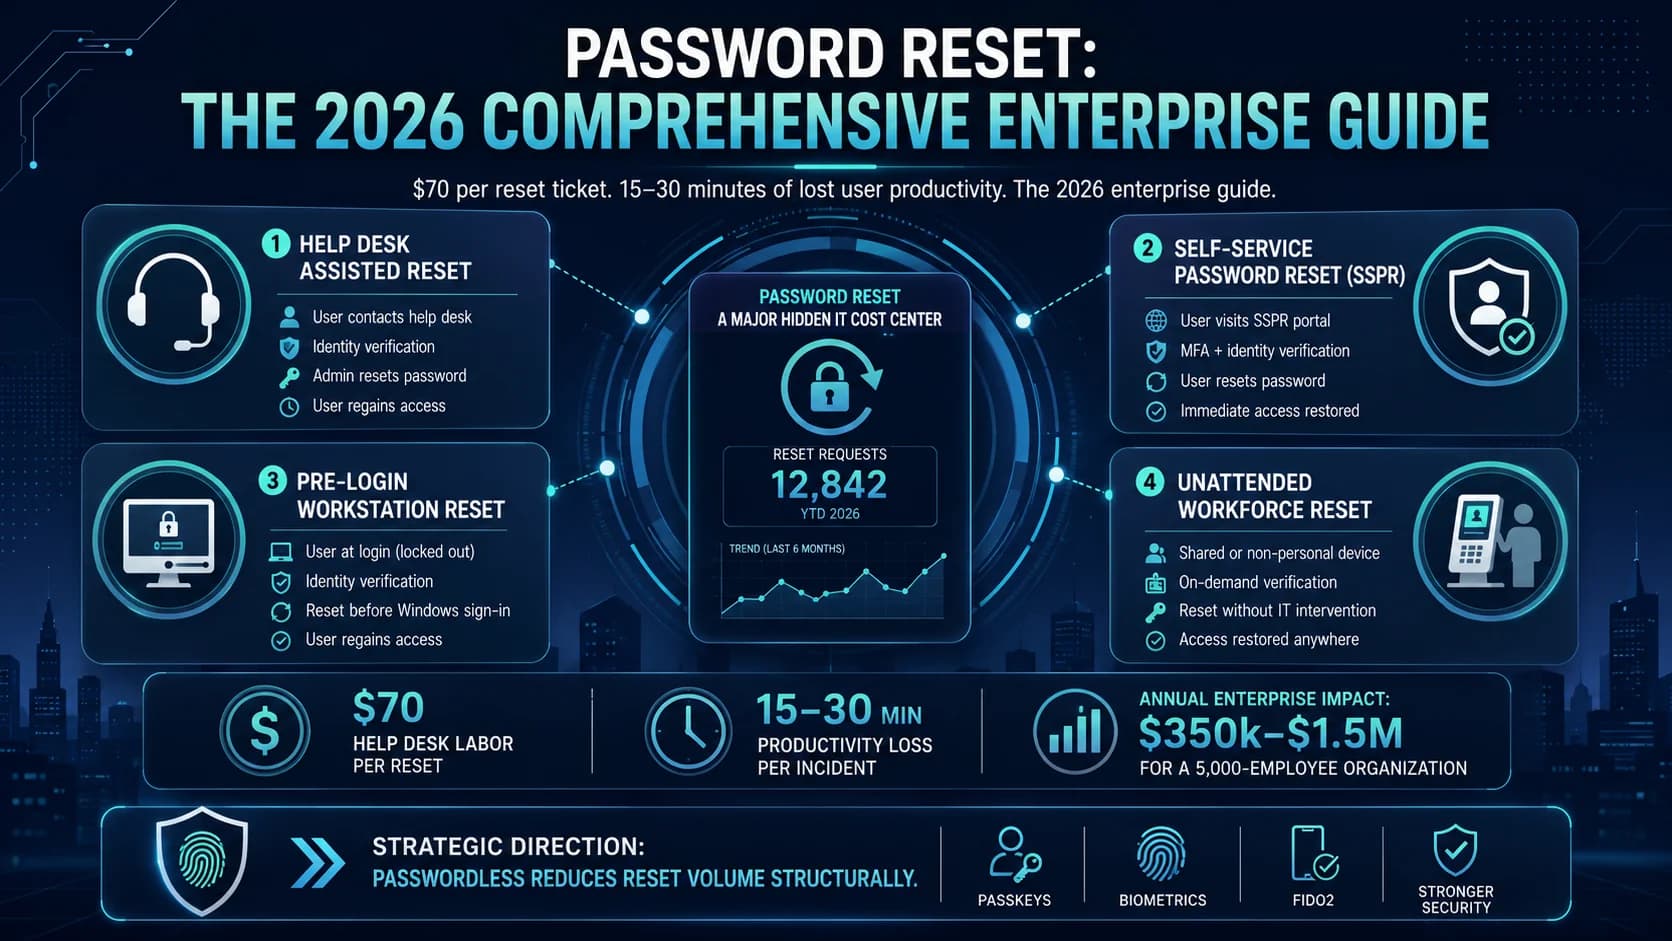
Enterprise password reset is one of the largest hidden cost centers in enterprise IT — help desk labor at $70 per reset ticket, workforce productivity losses at 15-30 minutes per user per incident, and the security surface every recovery flow creates. The 2026 comprehensive reference on the reset cost economics, the four workflow architectures, the compliance implications, the self-service reset (SSPR) discipline that reduces ticket volume 60-80%, and the passwordless migration path that eliminates the reset problem structurally.

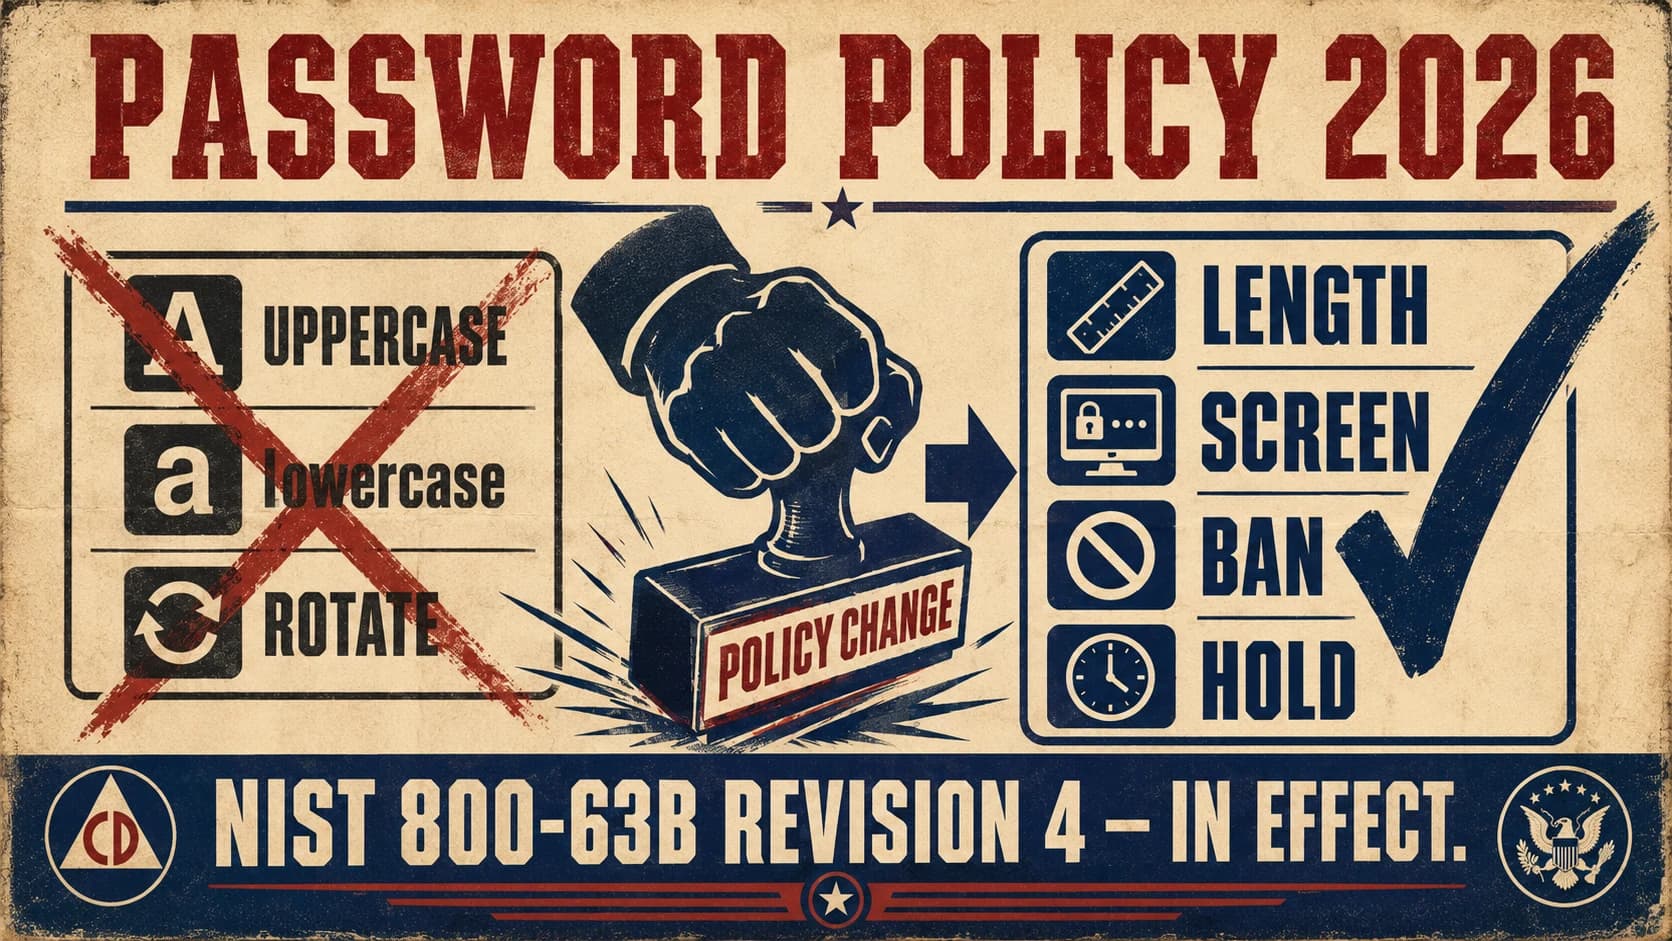
The password policy that actually reduces risk is not the password policy most enterprises still enforce. NIST 800-63B Rev. 4 (finalized 2025) dismantles the composition rules and periodic-reset mandates that defined the 2000s and codifies a fundamentally different discipline — length over complexity, breach-corpus screening, banned-list enforcement, no forced periodic rotation. The 2026 enterprise reference on the modern password policy, the AAL1/2/3 assurance-level mapping, the enforcement architecture that operationalizes it, and the migration path from the legacy policy every enterprise still carries.

The $15-per-password-reset figure that's been quoted for two decades undercounts the true cost meaningfully. The 2026 enterprise reference on the five cost components that make up the actual per-reset price, why each one undercounts, how to compute the number for your own organization, and the savings model when reset automation is deployed properly.

Temporary passwords are the recovery credential class that most enterprises still issue, share insecurely, and persist beyond their intended scope. NIST 800-63B Rev. 4 raised the bar in 2025, and the 2026 architectural pattern moves further — away from temporary passwords toward workflow-verified recovery. The enterprise reference on what's required, what's recommended, and where temporary passwords genuinely still belong.

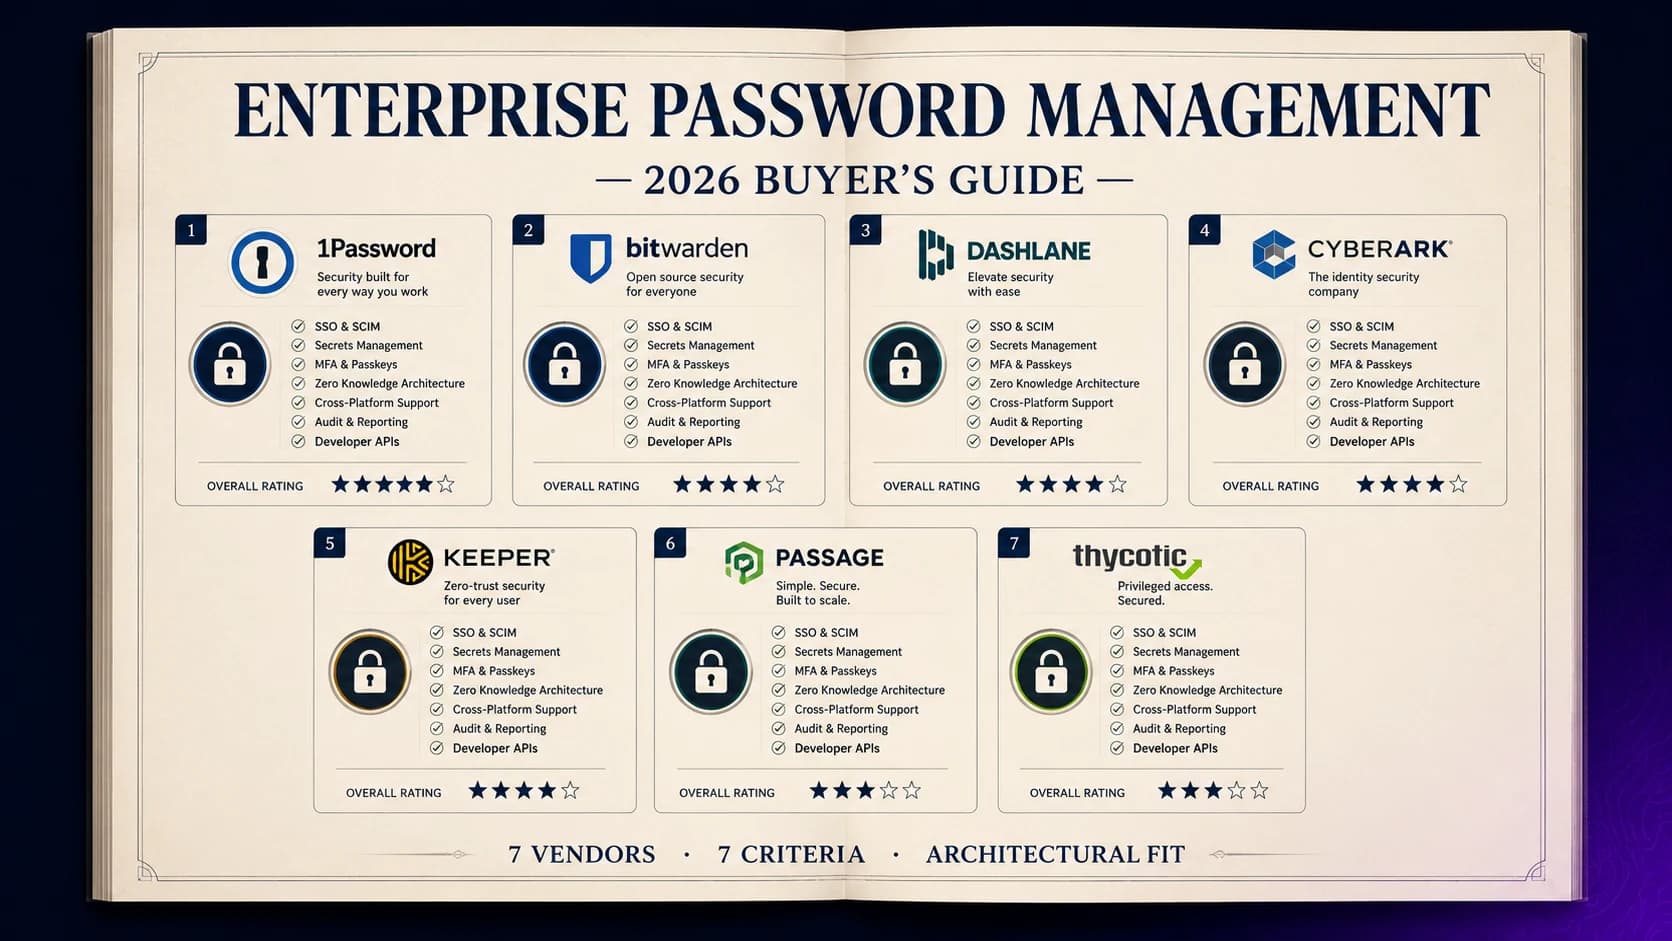
Enterprise password management software handles the password reality enterprises can't yet escape — legacy applications, frontline workers, contractor populations, and the long tail of systems that won't go passwordless this decade. The 2026 buyer's guide compares the major vendors, the evaluation criteria that actually matter, and the architectural fit decisions for different workforce profiles.
Savings Calculator
Enter your company size and see how much your help desk spends on password resets — and how much Avatier Credential Governance saves.
Avatier Credential Governance reduces your cost by
Over 1 year