Active Directory User Management, Governed with Avatier
Enable, disable, rename, move, expire: everyday Active Directory account changes add up. How to run each one through policy, approval and a record with Avatier User Management.
Identity governance, identity lifecycle, user provisioning, and IGA program design.
Showing 78

Enable, disable, rename, move, expire: everyday Active Directory account changes add up. How to run each one through policy, approval and a record with Avatier User Management.

A Secure Outcome is a completed, verified, policy-compliant identity activity. The categories, the six fields each one records, and why it is the unit Avatier customers pay for.

A group membership request is routine work that leaves sprawl behind when nobody sets an end date. How to run each change with an owner, a policy, and a record, and how Avatier does it.

Contractors and vendors need real access for a limited time, and their accounts outlive the engagement. How to bound third-party access to the engagement and prove it ended, with Avatier.

Joiner-mover-leaver automation runs every lifecycle change as a governed identity action. Why movers are where access piles up, and how Avatier runs changes through policy.

Identity reporting for executives means one evidence set, answered three ways. What the CISO, CFO and security team each need, and how Avatier Ledger's Persona Briefings deliver it.

A shadow AI agent acts with borrowed credentials and no owner. How shadow agents get access, how to find them, when to govern or retire one, and the sanctioned path Avatier provides.

AI can prepare, route, and evidence access reviews, but a named reviewer still decides. Where AI belongs in certification, the evidence auditors test, and what Avatier ships.

Before any per-action conversation makes sense, someone has to count. How to define the unit, find the counts, de-duplicate across sources, and produce a 12-month baseline you can defend.

Dynamic groups replace hand-maintained membership lists with rules over identity attributes. The 2026 guide to writing those rules, choosing an evaluation cadence, handling the people the rule gets wrong, and detecting drift.

Deprovisioning an AI agent retires its identity, credentials, and tool access when its purpose ends. The triggers, a seven-step offboarding runbook, and how Avatier supports it.

Pay Per Identity Action™ is Avatier's outcome-based identity pricing model: you pay only for completed, verified, policy-compliant identity outcomes, not for seats, modules, or services hours.

Agentic identity is the governed identity an AI agent acts under. How it differs from human and machine identity, how delegated authority works, and the lifecycle that keeps agents accountable.

MCP identity governance controls which identity, through which AI assistant, may invoke which identity tool, under what policy, and with what evidence. How it works and how to put it in place.

Privilege creep is access quietly accumulating beyond what a role needs — the entitlements that never get removed when people change jobs, cover for others, or run one-off projects. The practical 2026 guide to discovering the excess, revoking it, and keeping it from rebuilding.

An orphaned account has no valid owner; a dormant account has an owner but no recent activity. Both hold real access nobody is watching. The practical 2026 guide to finding, remediating, and preventing the accounts your lifecycle process leaves behind.

What CIAM actually is, what it has to handle that workforce IAM never does, the four building blocks that make it work, and the constant balancing act between a login your customers will tolerate and one an attacker cannot walk through.

Zero trust for identity means never trusting a request by default and verifying every one against live signals — identity, device posture, location, and risk. The foundational 2026 reference on what that actually requires.

Most enterprises run on-premises Active Directory and Microsoft Entra ID at the same time, bridged by identity synchronization. This is the 2026 reference on why the hybrid estate exists, where the sync bridge fails — duplicate identities, sync gaps, conflicting policy, password and hash drift — and the path to inventorying both directories, syncing or federating them, unifying policy, and governing the whole estate as one.

Machine identity management is the discipline of issuing, governing, and retiring the credentials that workloads, services, APIs, and machines use to authenticate — a population that now outnumbers human users by an order of magnitude. What it is, why machines need managed identities, where the risk concentrates, and the controls that bring workload credentials under lifecycle discipline.

An identity fabric unifies fragmented IAM, IGA, PAM, and directories into one system with unified policy and observability. Its building blocks, and what Avatier ships toward the pattern.

Automated user provisioning creates, updates, and revokes access from a single source of truth as identity events happen. What it is, how it works, and how to implement it.

Deprovisioning is the revoke side of the identity lifecycle: a leaver event that cascades revocation across every connected system so no active account, live session, or token outlives the person.

Most account takeovers don't start with a new exploit — they start with a password the attacker already has, which is exactly why the preventive controls that work look nothing like the ones most programs invest in first.

Every major transformation initiative — cloud migration, remote and hybrid work, mergers and acquisitions — eventually stalls on the same question: who gets access to what, and who decided? The 2026 strategy reference on identity management as the enabler and the bottleneck of digital transformation, the business case executives actually fund, and what modernization does not fix.

Static identity rules catch the attacks that announce themselves. They miss the ones that log in with valid credentials and behave almost normally. The 2026 reference on AI-driven identity monitoring — what behavioral analytics actually detects, the four telemetry sources that make or break the model, and the false-positive economics nobody budgets for.

Identity governance fails when it runs as a security-team-only initiative. The 2026 framework for cross-functional collaboration: four stakeholder groups, three coordination models, and how zero trust makes it a shared discipline.

Infrastructure-as-a-Service breaks identity models built for one directory. The 2026 reference on multi-cloud fragmentation, compliance auditability, and provisioning automation at IaaS scale.

Boards don't fund CVE counts — they fund dollar exposure. A practical framework for turning access sprawl, orphaned accounts, and audit findings into risk language executives actually act on.

A single impersonation call to a help desk — not a firewall failure — triggered a 2023 casino-industry breach that cost roughly $100 million, and the fix is verification discipline, not new firewalls.

The governance lessons enterprises should draw from major identity breaches — not the attack mechanics, but the structural gaps that let one credential become a headline.

Identity and access management is the control layer that decides who and what can reach enterprise systems — and in 2026 it functions as the security program itself, not a supporting utility underneath it.

Attackers rarely break provisioning systems outright — they walk through orphaned accounts, standing privilege, and unrevoked access left behind, and identity governance is what closes it.

Malicious, negligent, and compromised insiders each leave distinct behavioral and access-pattern red flags — and identity governance, not perimeter security, is what actually contains the resulting blast radius.

LDAP is the read-optimized directory protocol still sitting under most enterprise IAM stacks — here is how its structure, bind and search, LDAPS, replication, and schema actually work in production.

Connecting a modern IAM platform to the applications you already run is a connector problem before it's a strategy problem — SCIM, LDAP/AD, SAML/OIDC, and API or agent connectors, matched to what each app can actually speak.

AI-driven provisioning replaces manual tickets and static rules with policy-based access grants triggered by HRIS and identity-graph signals — but only inside guardrails a human still has to own.

Progressive profiling builds a customer identity profile in small, consented steps across sessions instead of demanding it all at registration — here's how the consent mechanics actually work.

Most identity-driven breaches follow the same chain — stolen credential, no MFA, lateral movement, exfiltration — and the controls that break that chain are well understood, if rarely fully deployed.

AI-driven fraud detection in access control catches collusion, synthetic identities, and gamed certifications by modeling relationships and approval patterns, not just individual behavior.

A technical walkthrough of how machine learning models actually detect identity anomalies — baselining, feature signals, unsupervised versus supervised approaches, and false-positive tuning.

Hybrid cloud identity means bridging one on-prem or mainframe estate to a single cloud provider, not spanning multiple public clouds — the architecture, the failure modes, and the limits.

AI-driven adaptive controls cut security friction by moving verification into passive signals instead of adding prompts — the 2026 reference on invisible security.

SCIM is the RESTful, JSON-based standard that automates identity provisioning and deprovisioning between a source of truth and downstream apps. What it is, how it works, and where it fits in IGA.

The cost of identity-management failure is not a single line item — it is a breach that starts with a compromised or over-provisioned credential, the downtime while responders lock the environment down, the compliance penalties that follow inadequate access controls, and the customer and market trust that erodes long after the incident closes. This 2026 reference separates the cost of IAM failure from the cost of the IAM program, gives extractable answers to how each failure channel becomes real money, and covers the controls that lower the risk without ever eliminating it.

A senior practitioner's 2026 comparison of CIAM (customer identity) and workforce identity management — what actually differs, when to use each, how they sit in an enterprise architecture, and the one governance model underneath both.

A break-glass account is a pre-provisioned, tightly governed emergency credential that grants high-privilege access when normal authentication paths are unavailable — during an outage, an admin lockout, or a disaster-recovery scenario. The 2026 reference on what break-glass means in technology, when to invoke it, and the approval, auditing, time-boxing, and rotation controls that keep the emergency credential from becoming a standing back door.

In identity and access management, user experience is not a design nicety layered on top of security — it is the variable that decides whether your controls get used or quietly routed around. The 2026 practitioner guide to why friction drives workarounds, where UX breaks across the identity lifecycle, how to measure it, and the UX-versus-security tradeoff done right.

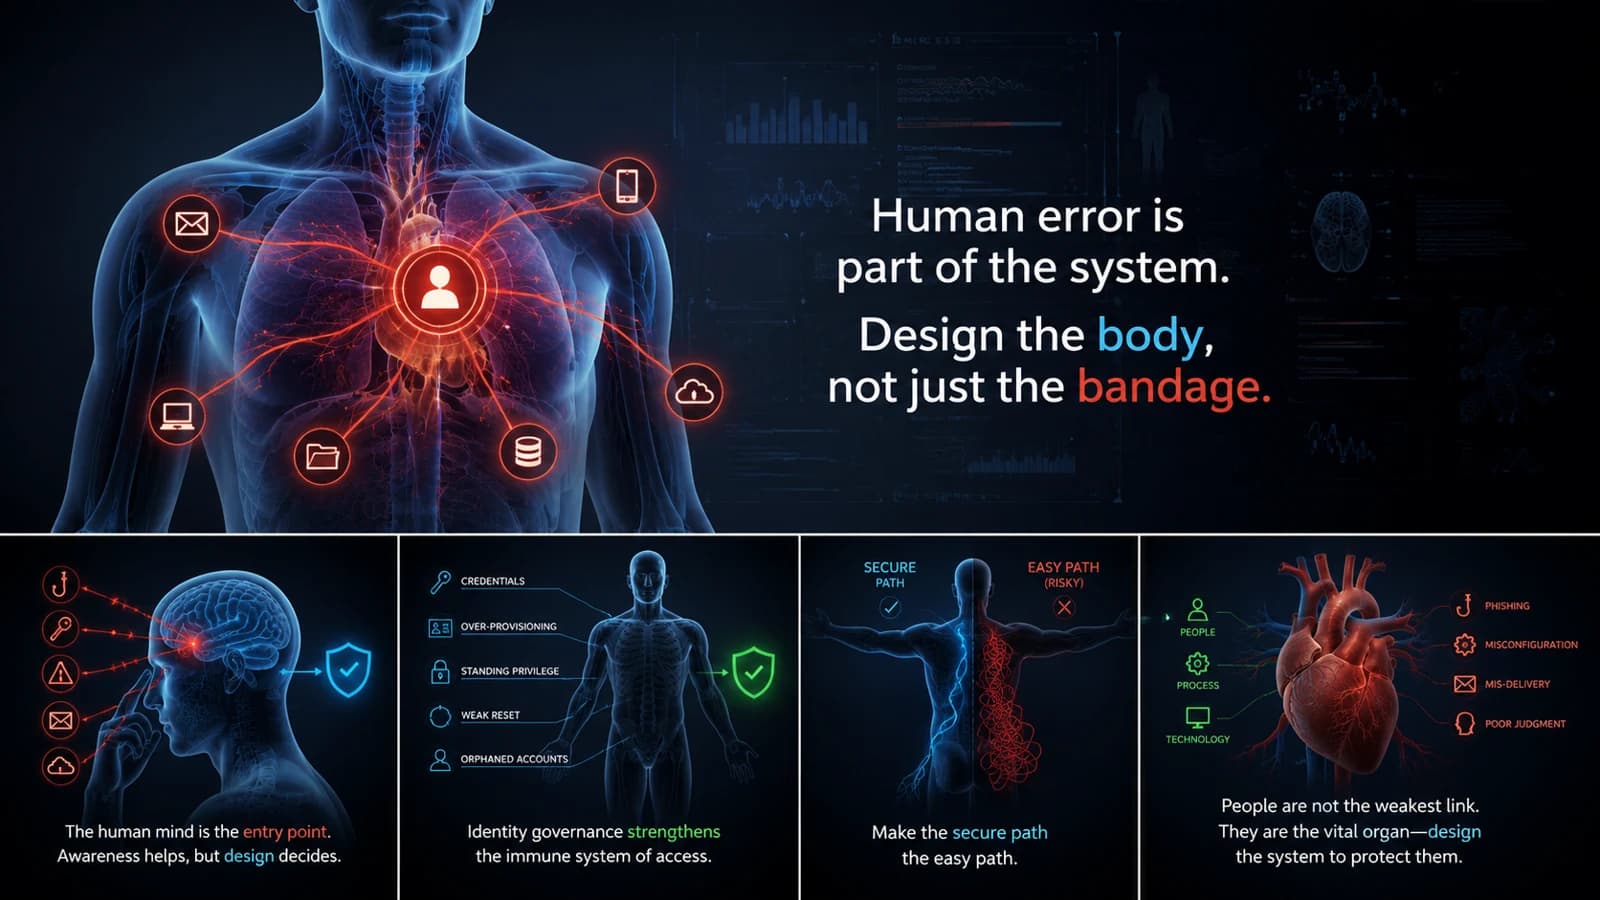
There is no single authoritative percentage for human error in breaches — the honest answer is directional: most breaches involve a human element, and the exact figure depends on who is counting and what they count.

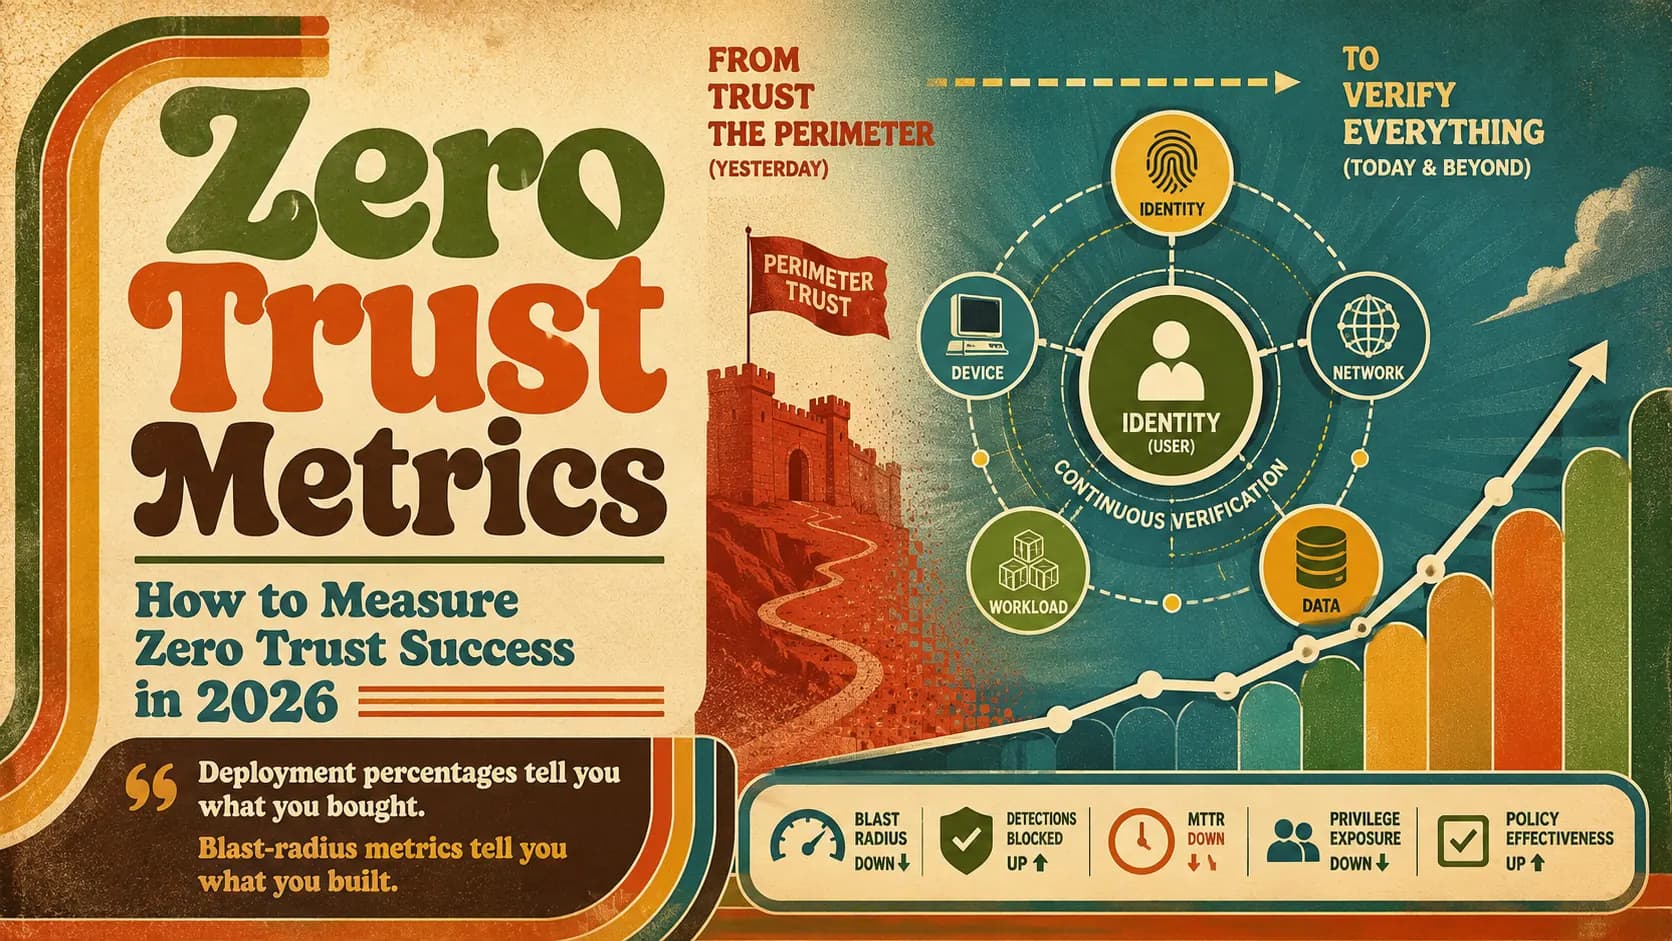
The 2026 reference on zero trust metrics: the five measurement domains, the identity KPIs that predict blast radius, maturity checkpoints, and the numbers that mislead.

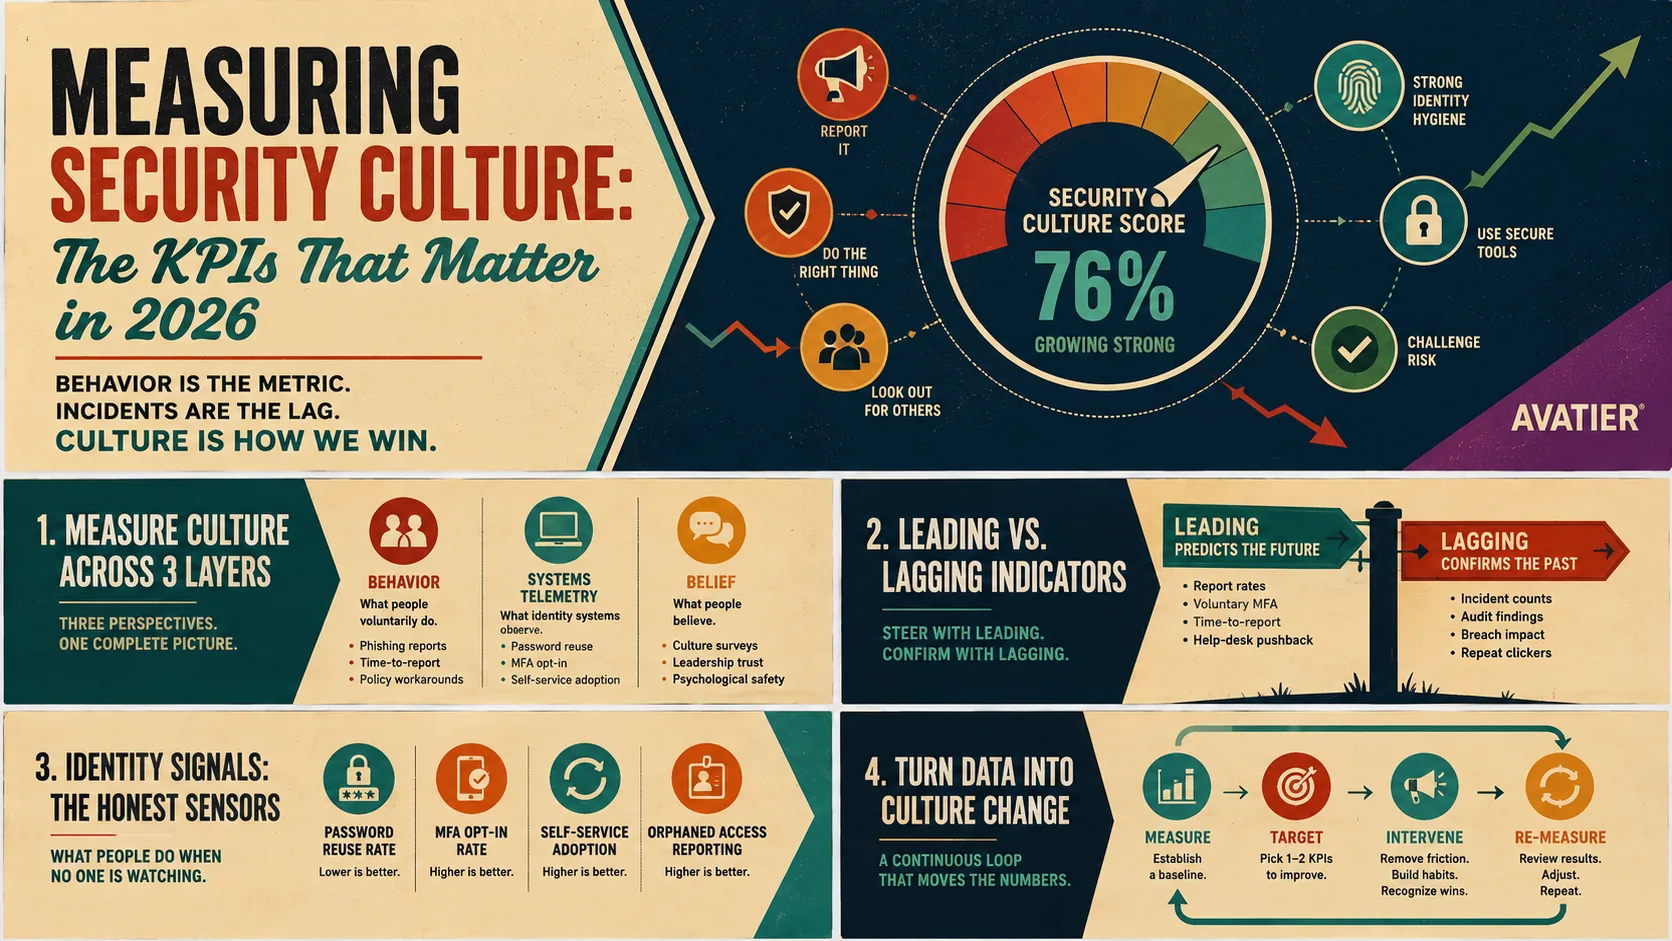
How organizations measure and improve security culture in 2026: leading vs. lagging indicators, behavioral KPIs, identity hygiene signals, survey instruments, and how to actually move the numbers.

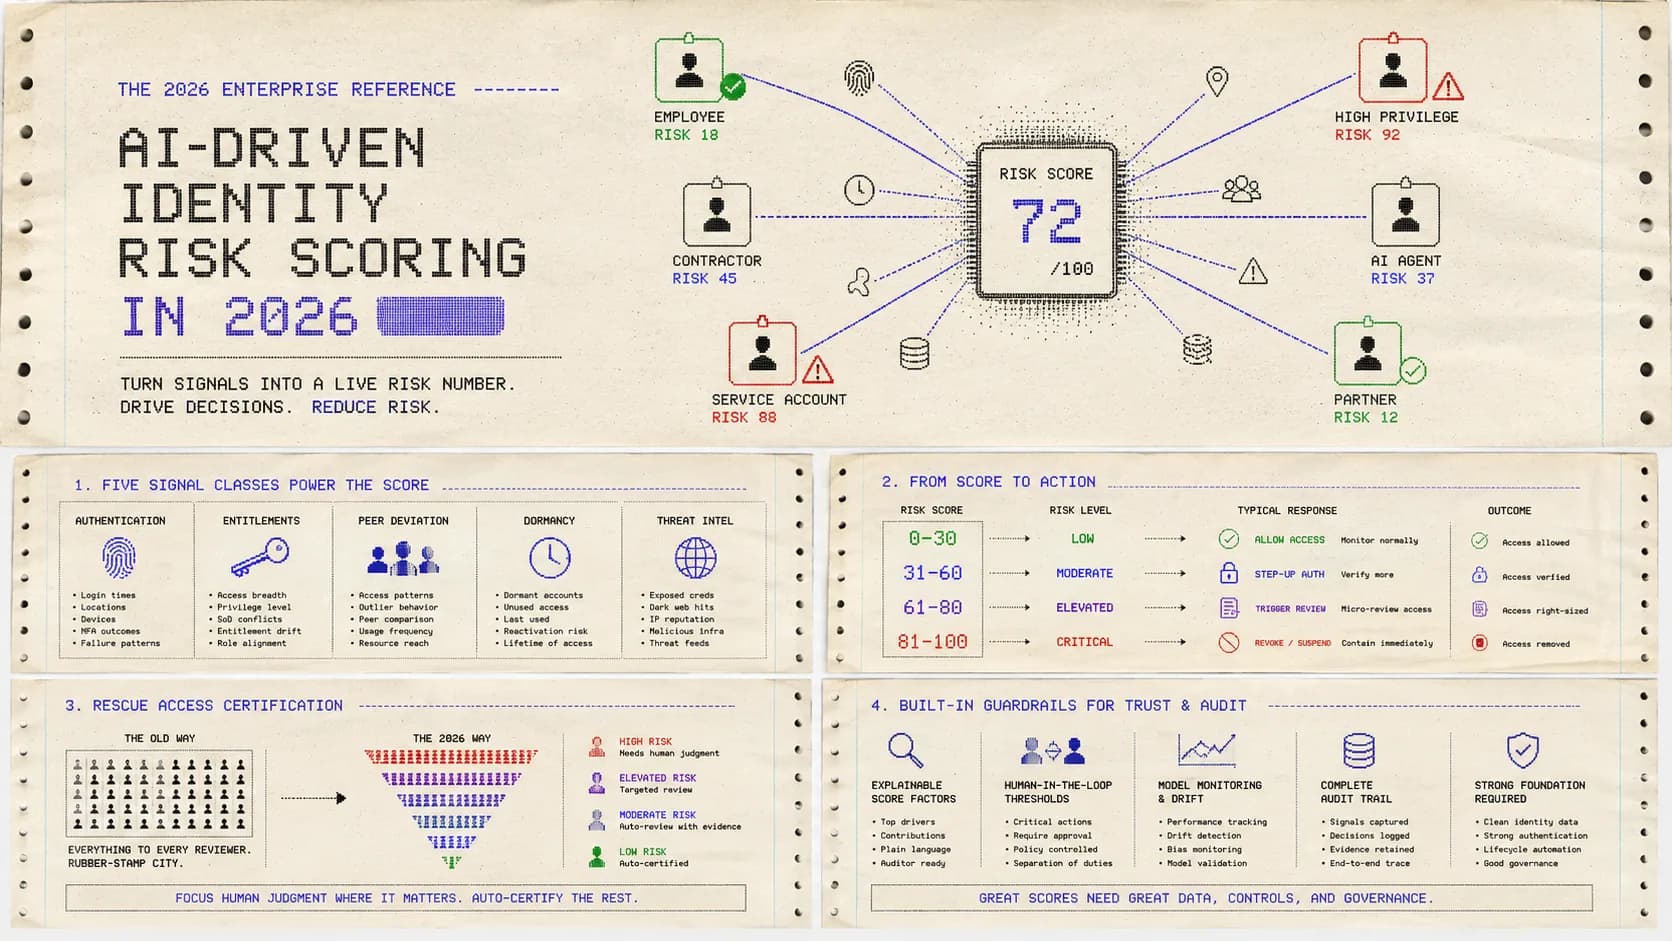
AI-driven identity risk scoring turns authentication, entitlement, and behavior signals into a live per-identity risk number that drives step-up auth, reviews, and revocation. The 2026 reference.

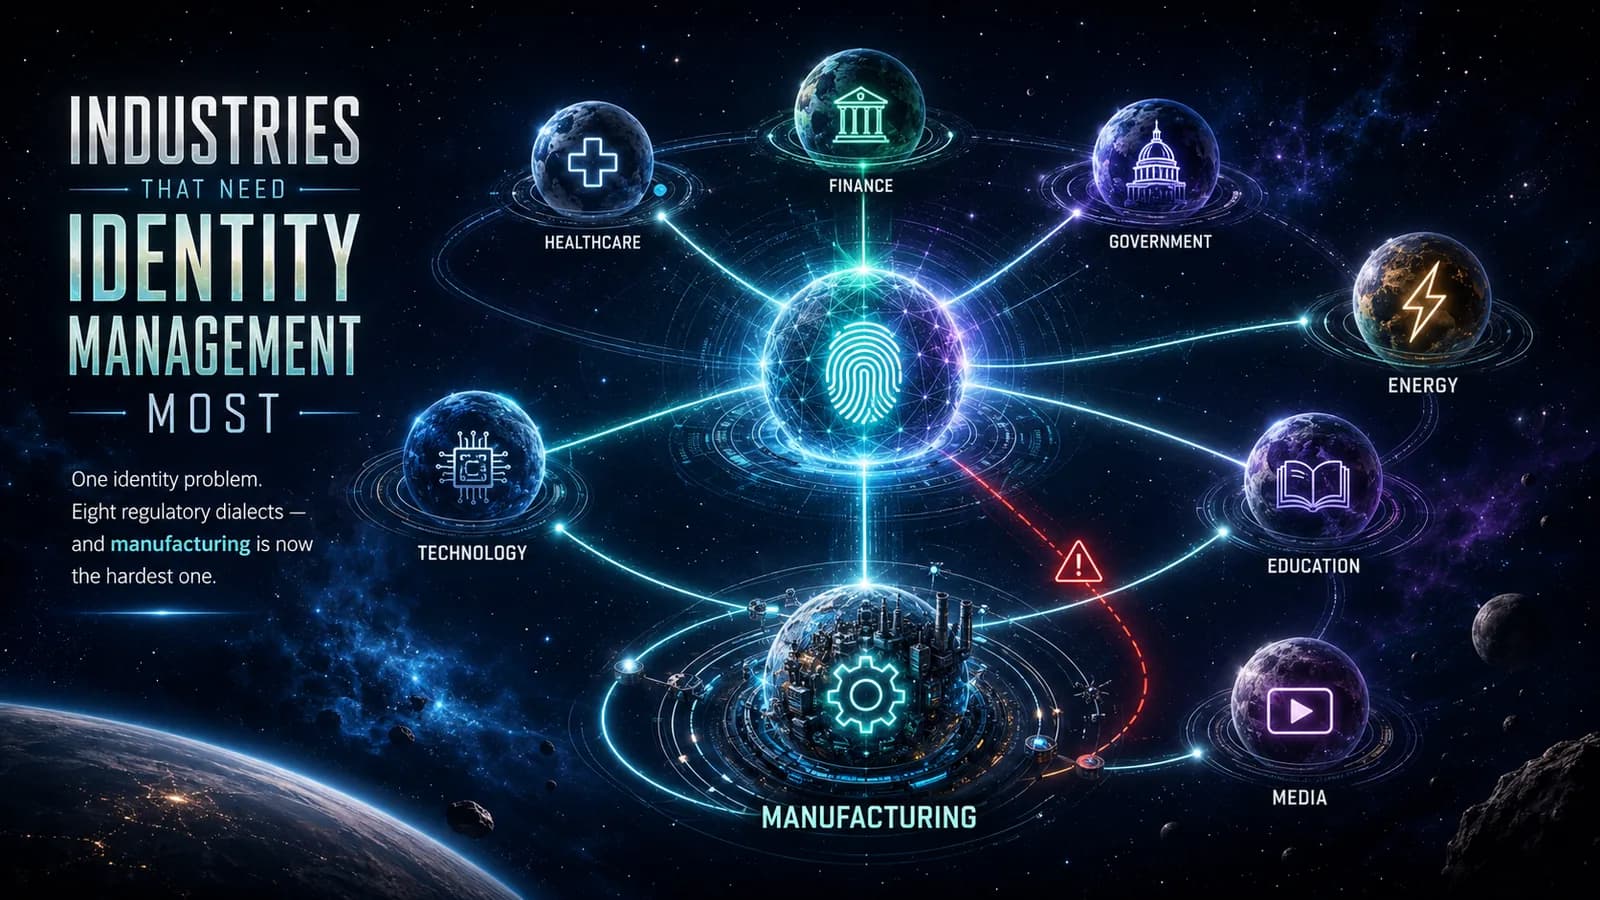
Eight industries carry regulatory or operational pressure that makes identity governance non-optional — and manufacturing has quietly become the hardest of them. The 2026 refresh maps each sector's identity problem, its frameworks, and the state-level mandates (TX-RAMP, StateRAMP, privacy acts) now underneath all of them.

Access governance is the discipline that answers one question continuously: does every identity in the enterprise hold exactly the access it should, right now? The 2026 reference on the five control surfaces, the access governance vs. IGA distinction, and where reviews collapse into rubber-stamping.

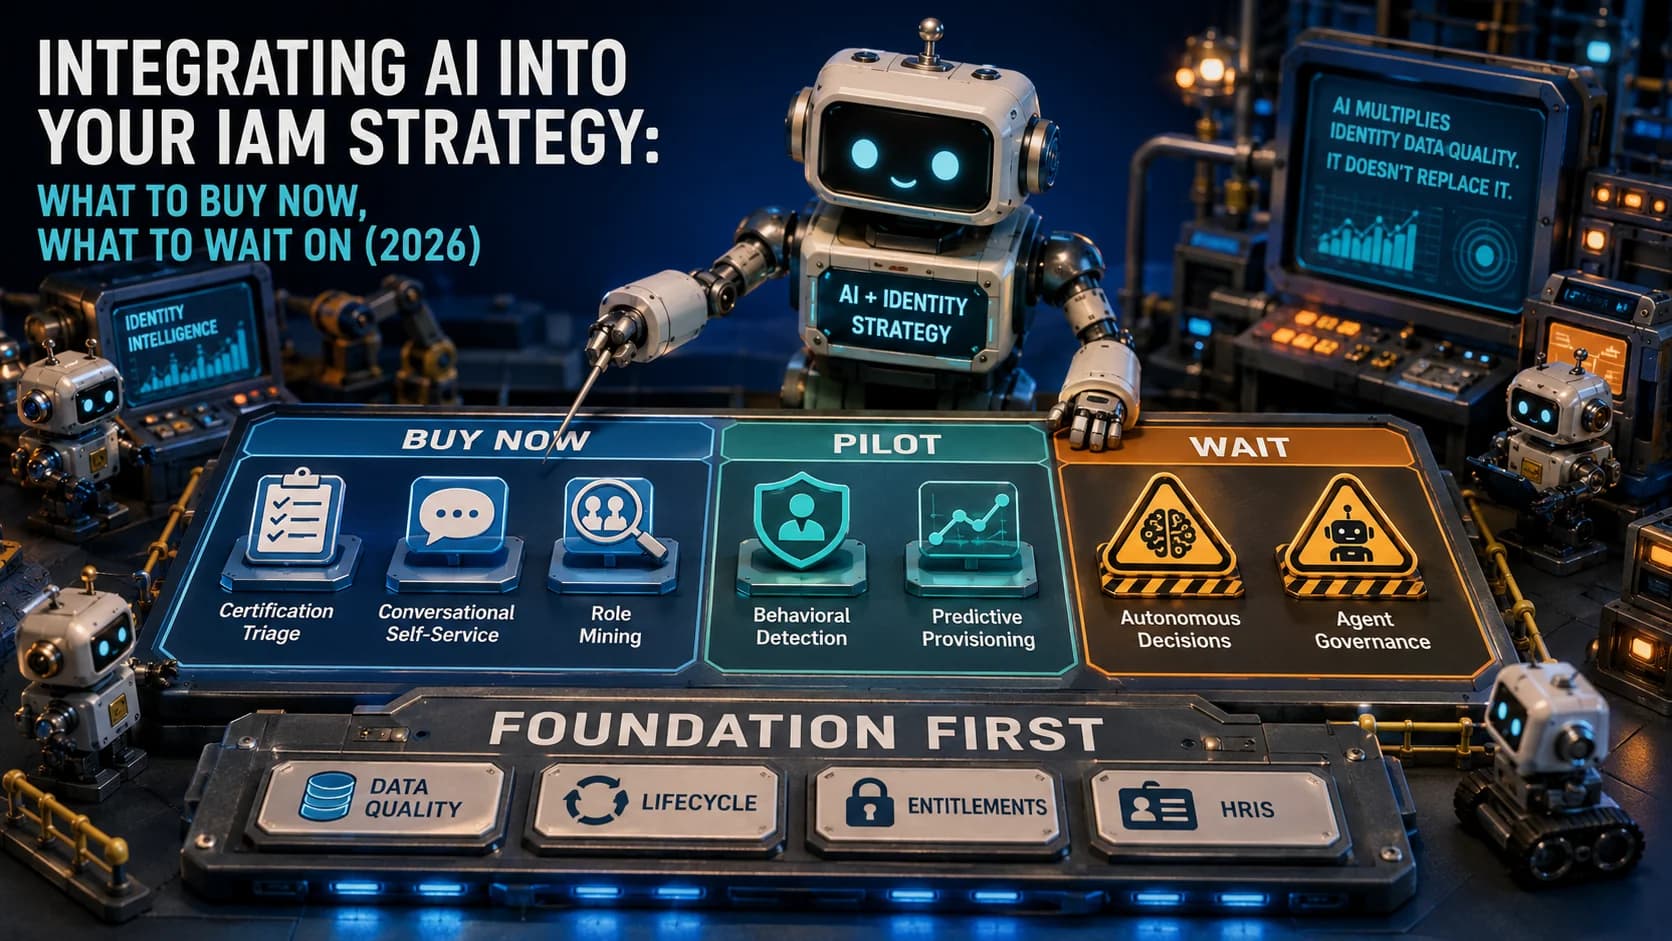
Every identity vendor's 2026 roadmap says AI. Most enterprises can't tell which parts will pay for themselves next quarter and which are demos with a release date attached. After three decades building identity automation, my read: three AI capabilities are worth buying today, two are worth piloting, and one category is worth refusing until the vendors can answer five questions. Plus the readiness test that decides whether any of it works for you — and the ordering mistake that wastes more AI budget than any bad vendor choice.
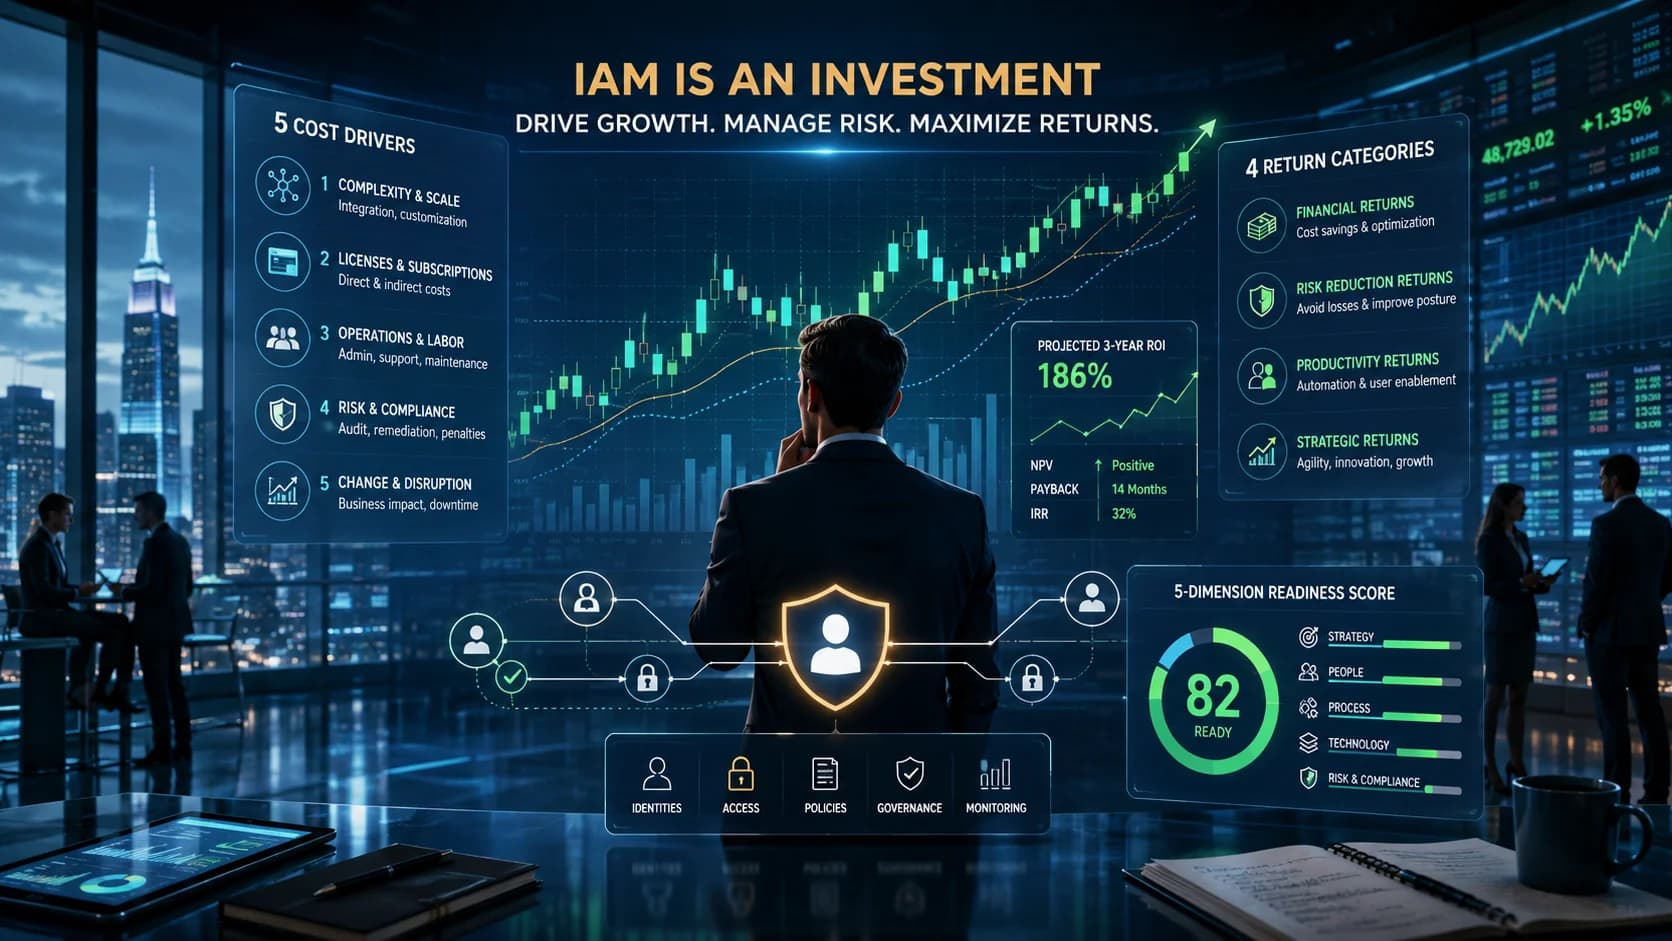
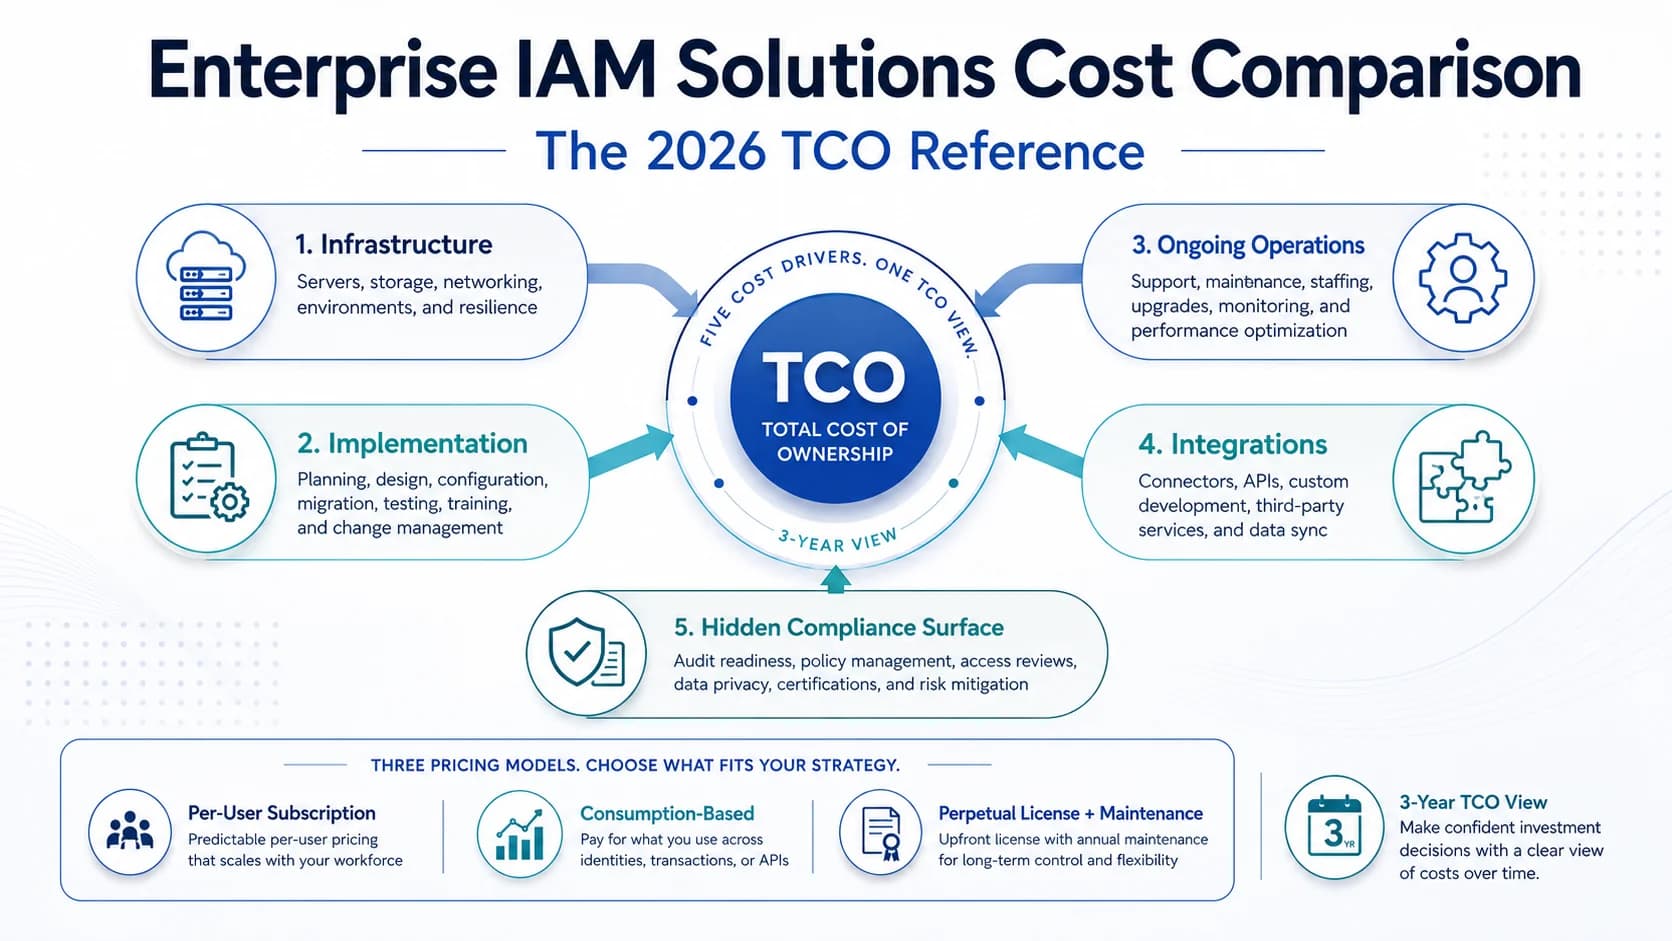
IAM investment questions rarely fail on the ROI math — the math works. They fail on readiness: enterprises buy governance platforms before the identity data, ownership model, and process discipline exist to use them. The 2026 reference on what IAM actually costs across its five cost drivers, what the investment returns and when, and the five-dimension readiness assessment that predicts whether your organization will realize the ROI or join the roughly half of IGA programs that stall.
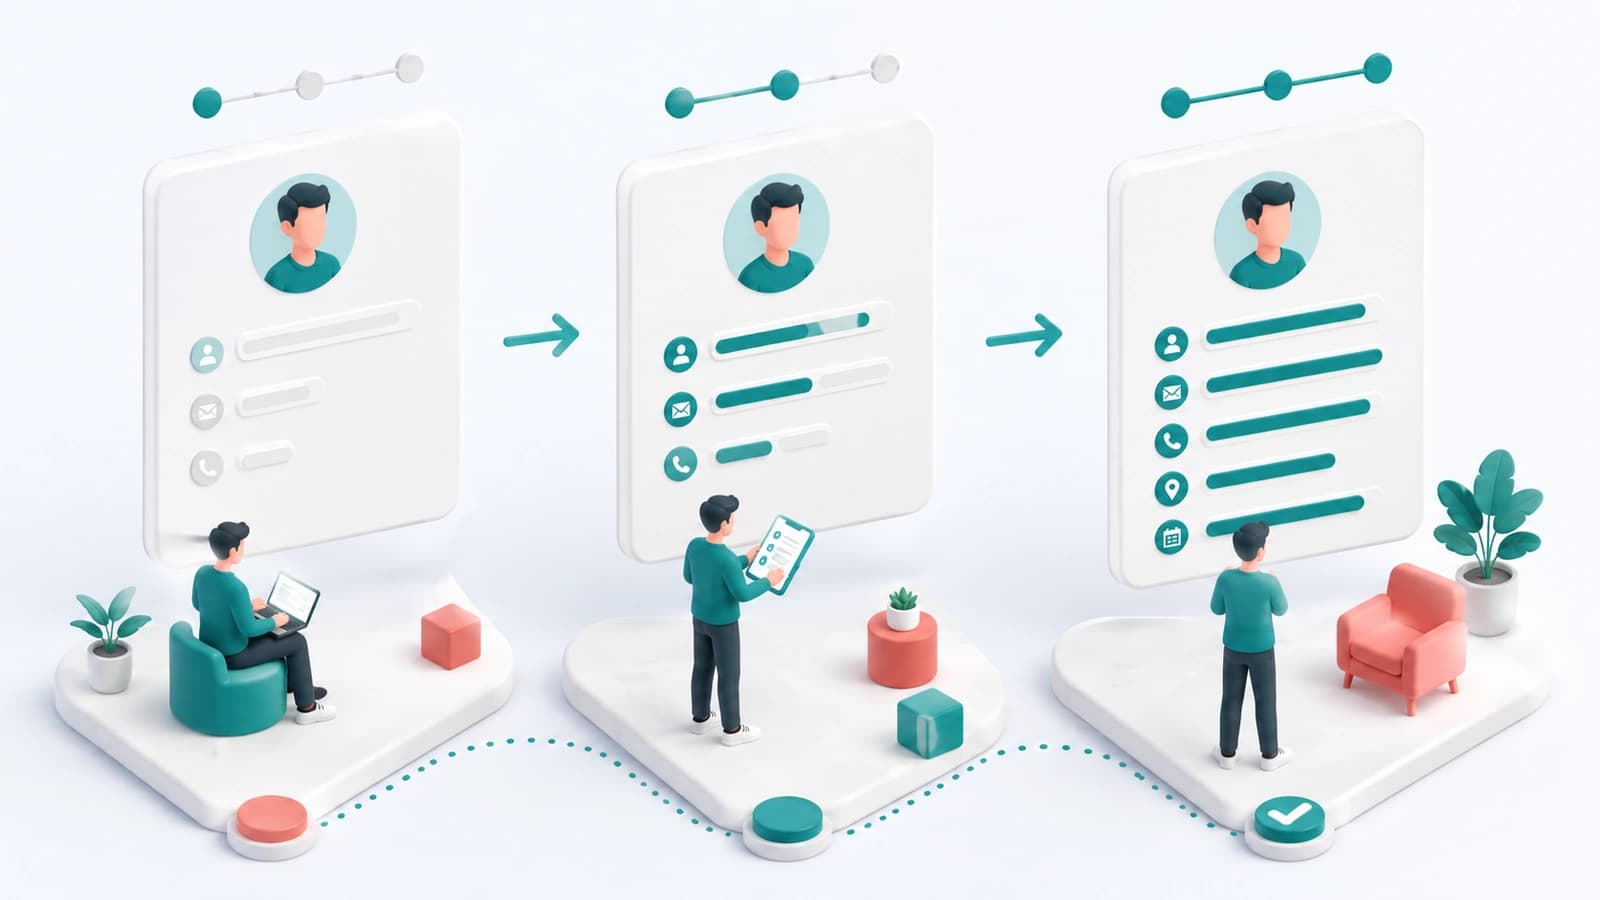
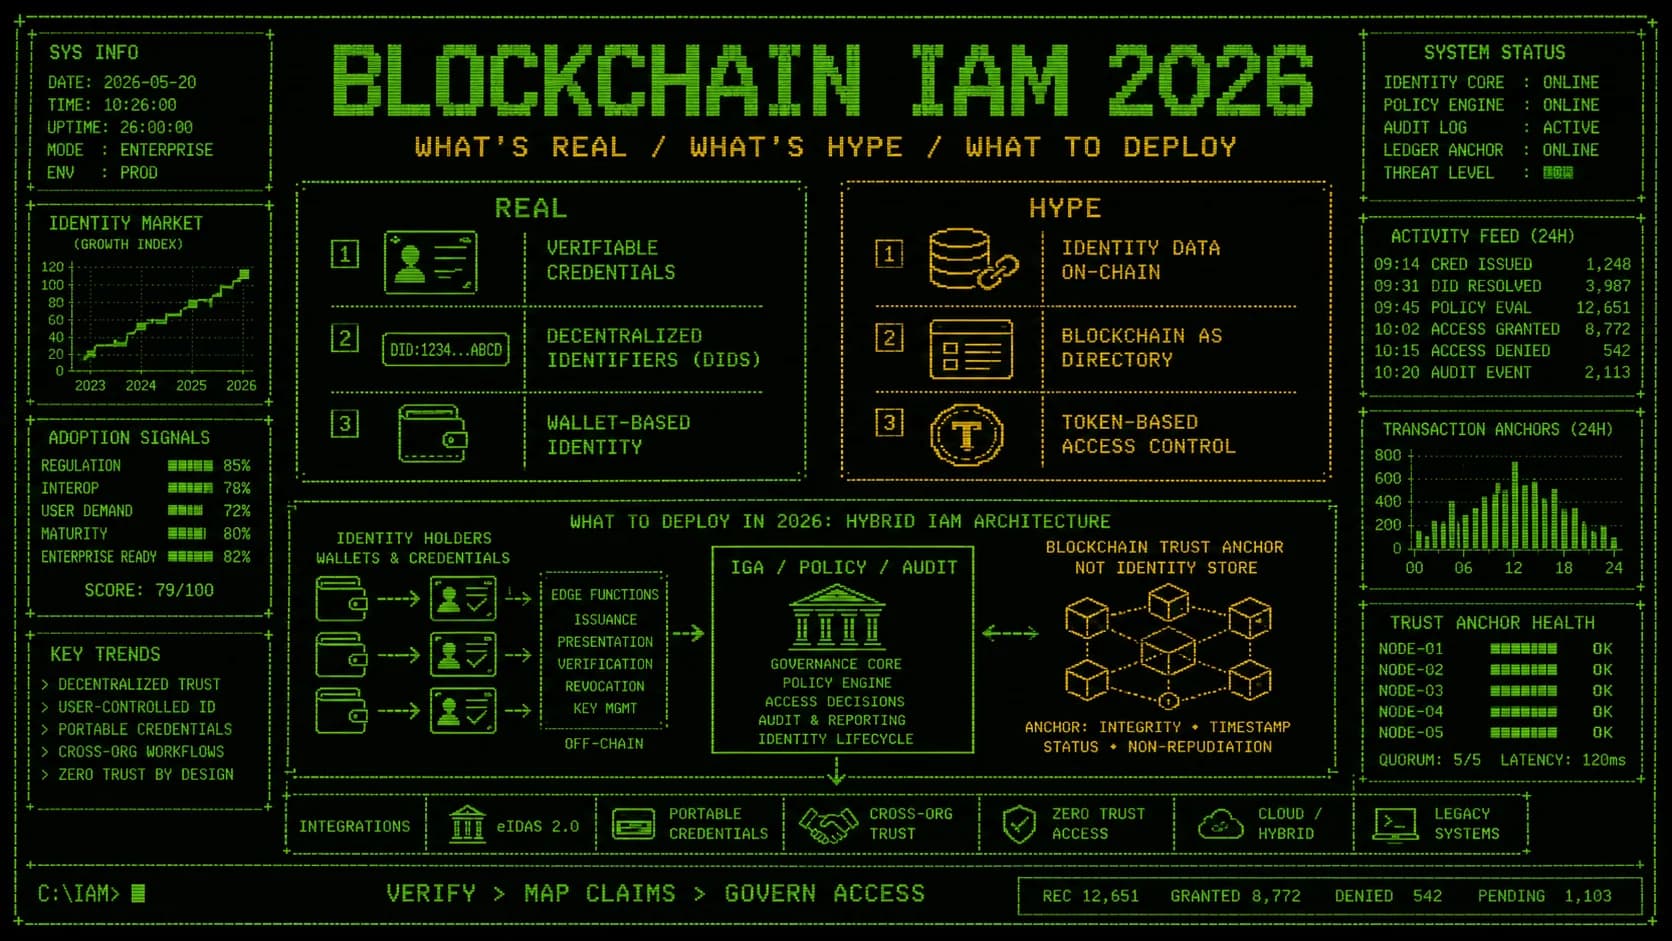
A decade after the first blockchain identity white papers, the technology has sorted itself into two piles: a small set of patterns that genuinely work — verifiable credentials, decentralized identifiers, and wallet-based identity now backed by the EU's eIDAS 2.0 mandate — and a large pile of abandoned projects that tried to put identity itself on a chain. The 2026 enterprise reference on where blockchain-based IAM delivers (portable workforce credentials, reusable verification, cross-organization trust), where it never will (replacing your directory, lifecycle, or governance), and the architecture pattern that connects decentralized credentials to centralized accountability.
Ai4 2026 lands in Las Vegas August 4-6 with three full tracks on AI agents, a cybersecurity track, and an oversight track on AI governance and model risk. The agenda is telling you something: the enterprise AI conversation has shifted from what models can do to what agents are allowed to do — and that is an identity question. Avatier will be at Booth #1053 with live demos, product announcements, and a point of view on why every autonomous agent needs the same lifecycle, governance, and least-privilege discipline you apply to human identities.

Access governance and user lifecycle management are two identity disciplines that only produce defensible IAM posture when they're integrated as one continuous workflow — HRIS-driven lifecycle events triggering access changes, certification campaigns reasoning against lifecycle state, and remediation workflow that closes the loop through lifecycle rather than parallel to it. The 2026 enterprise reference on the integration architecture, the failure modes when lifecycle and governance run as silos, and the operational discipline that produces audit-ready posture.

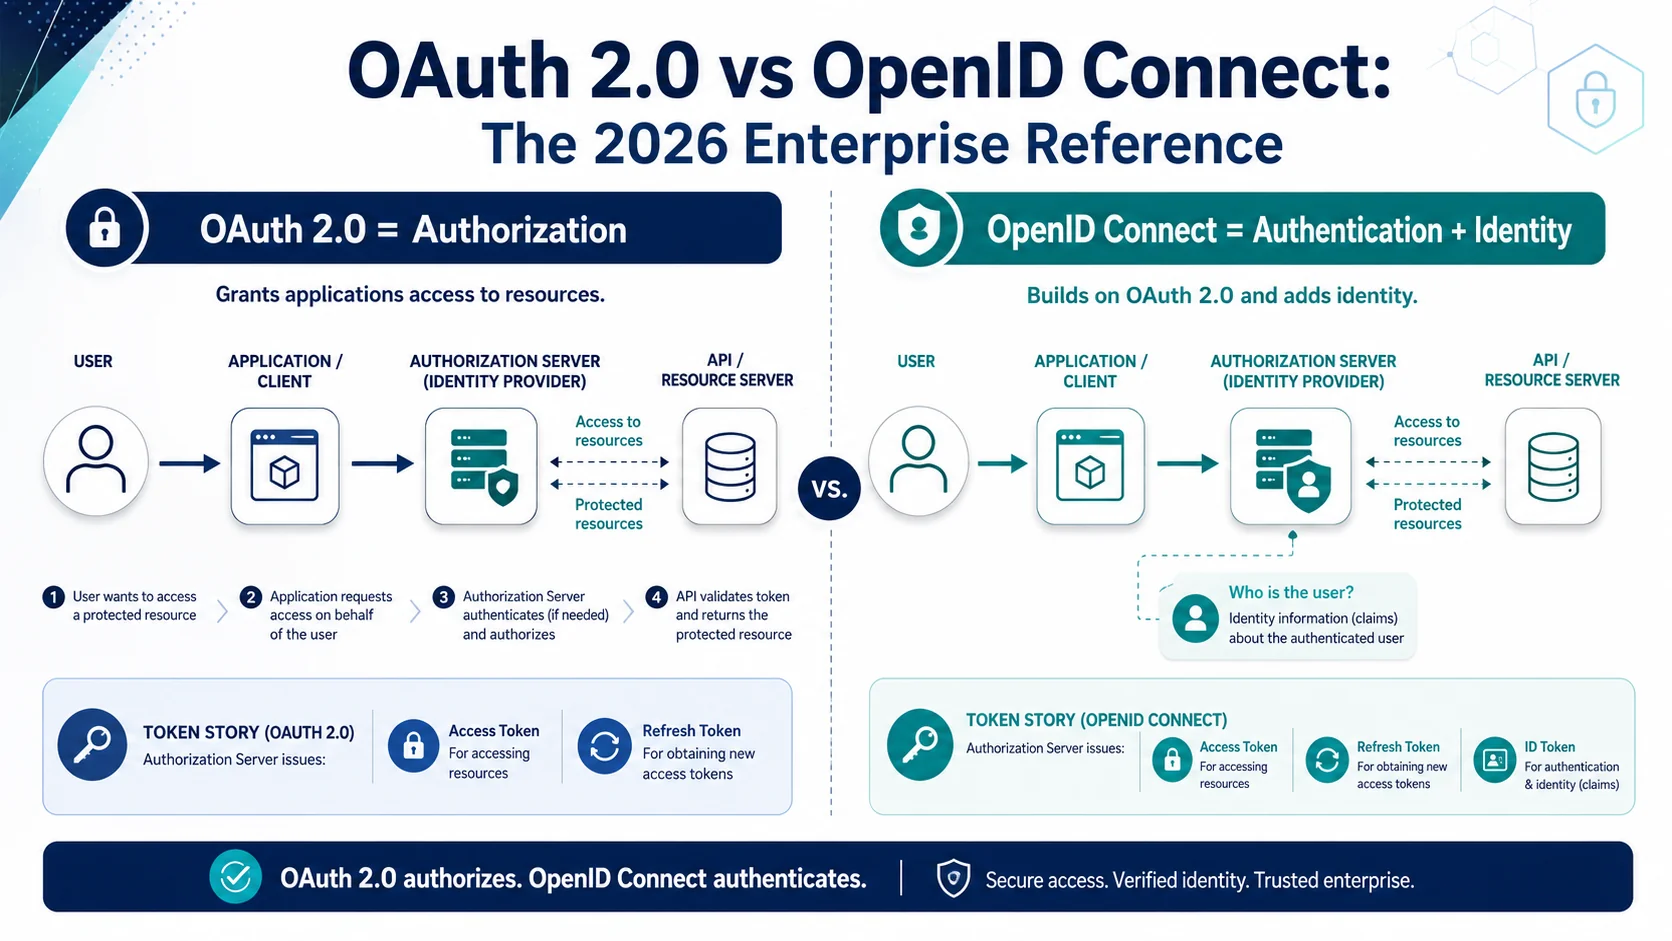
OAuth 2.0 and OpenID Connect are routinely confused in enterprise IAM conversations — they solve different problems and shouldn't be substituted for each other. The 2026 enterprise reference on what each actually does, the token types each issues, the four enterprise use cases and which protocol fits each, the common misuse patterns that produce security incidents, and the composition patterns that let both protocols do the job they're actually good at.

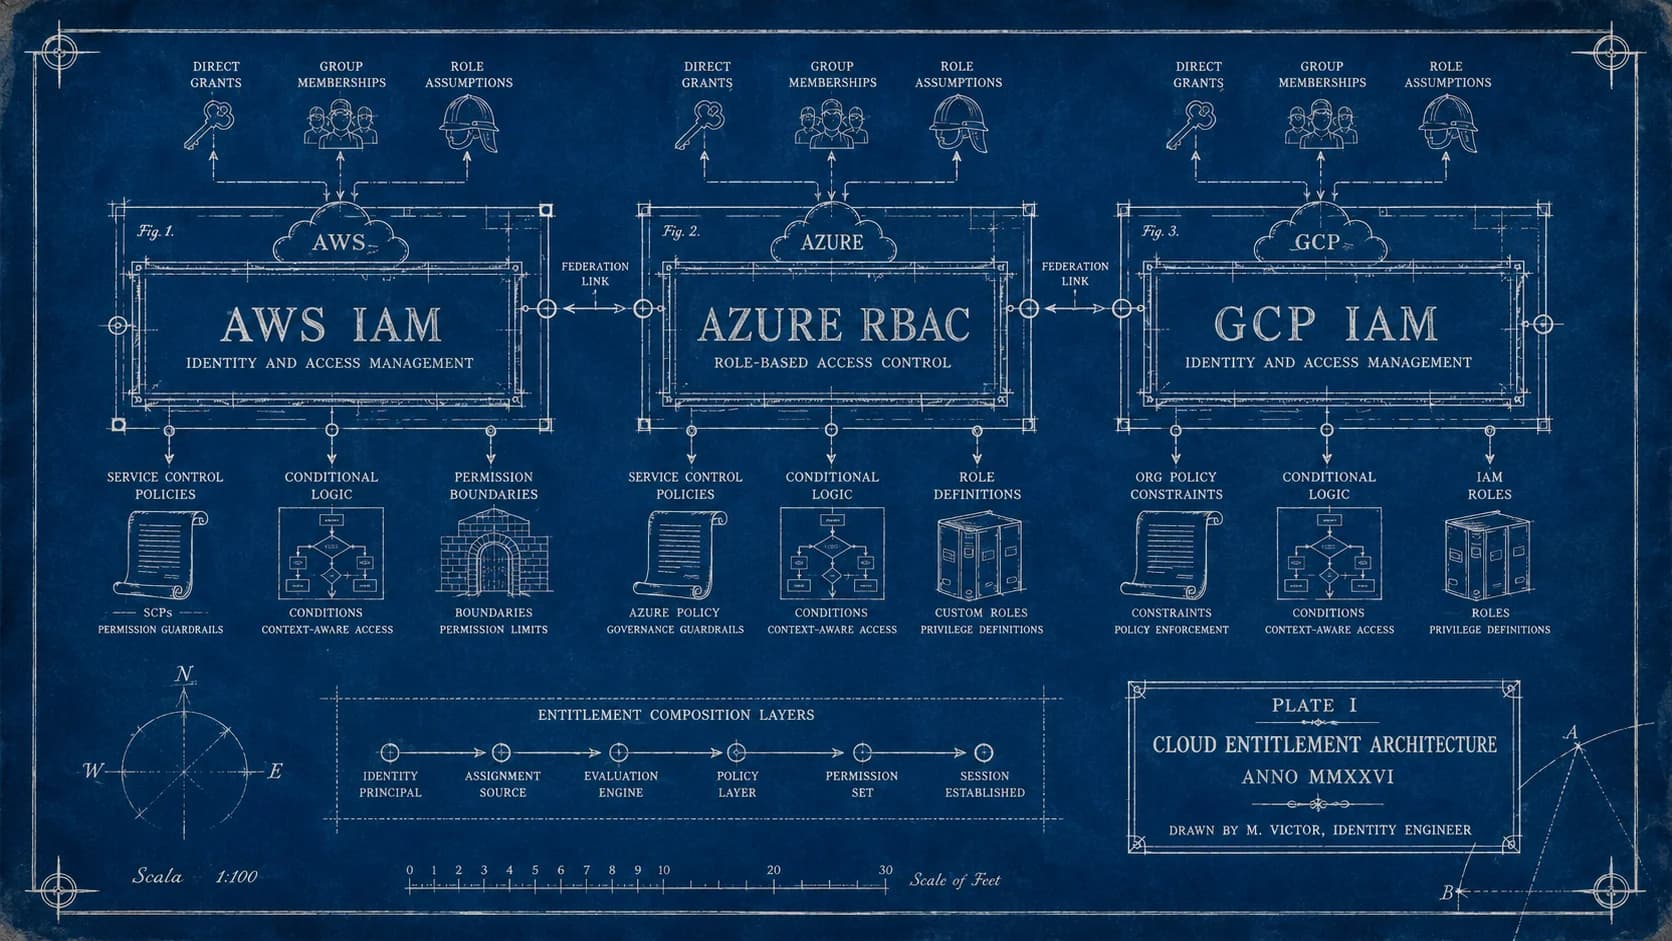
Multi-cloud identity management is where every enterprise IAM program actually lives in 2026 — federated humans and workload identities spanning AWS, Azure, GCP, and the SaaS estate, with wildly different native IAM primitives per cloud. The 2026 enterprise reference on the federation-first architecture that keeps this coherent, the human-vs-workload identity split, the four multi-cloud anti-patterns that produce audit findings, and the operational pattern that scales without producing per-cloud identity silos.

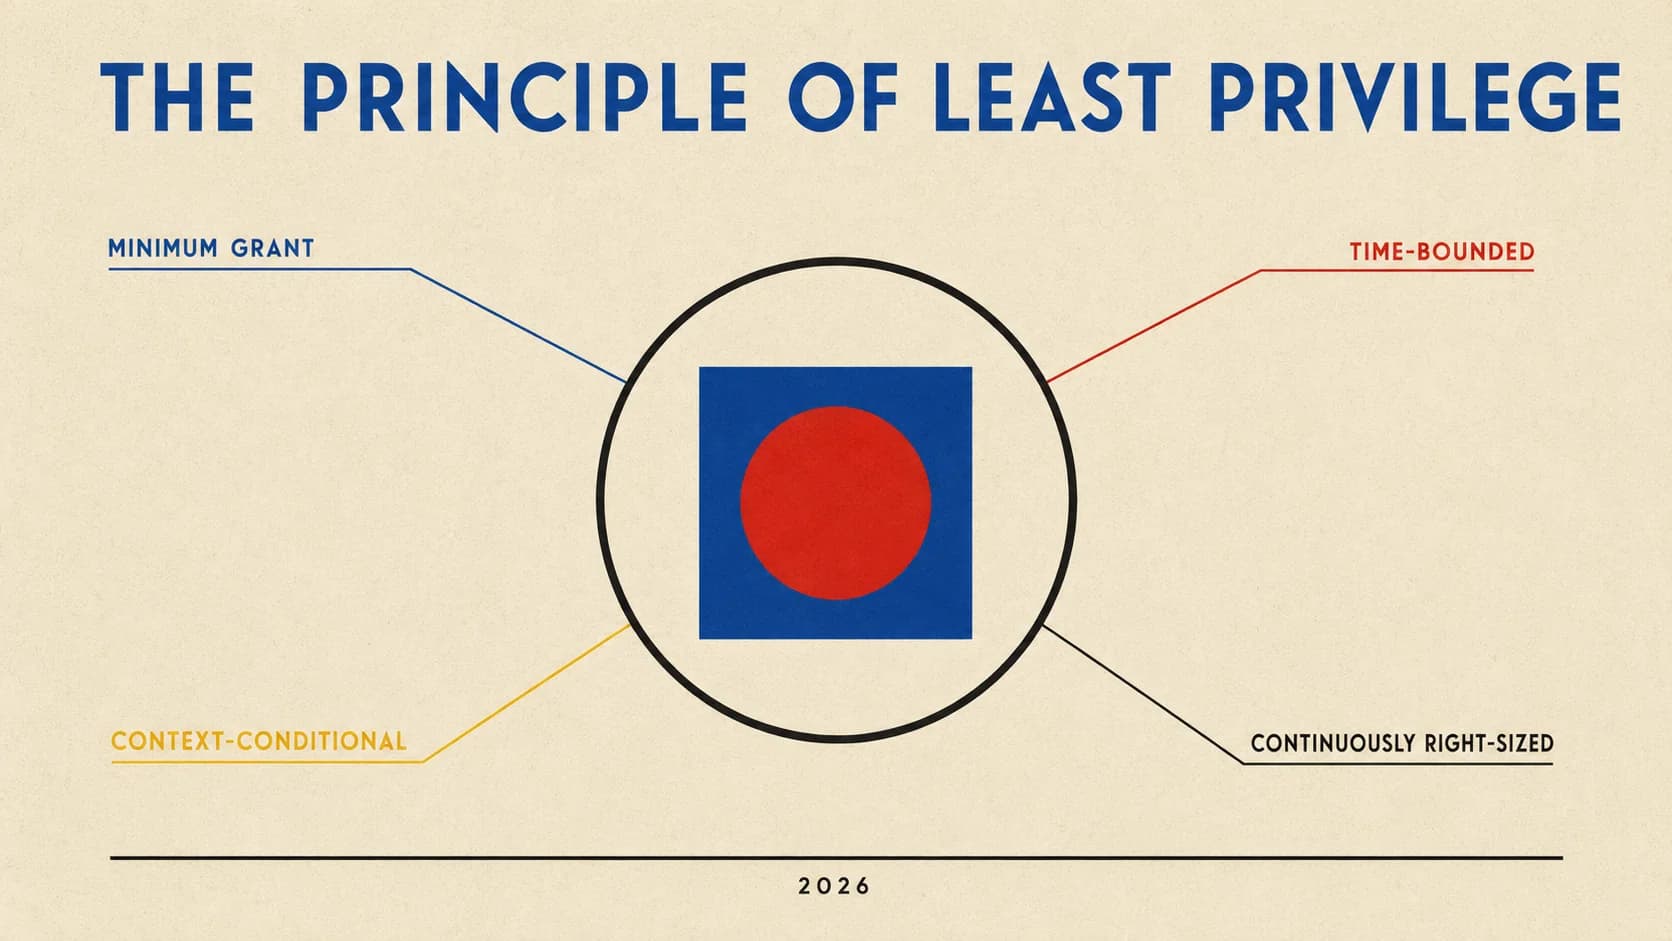
Least privilege is the oldest and most durably-relevant access-control principle in enterprise identity. The 2026 enterprise reference on what 'minimum necessary access' actually means operationally, the four surfaces where it applies (human, privileged, service, agentic), and the architecture that produces defensible least-privilege posture across all four.

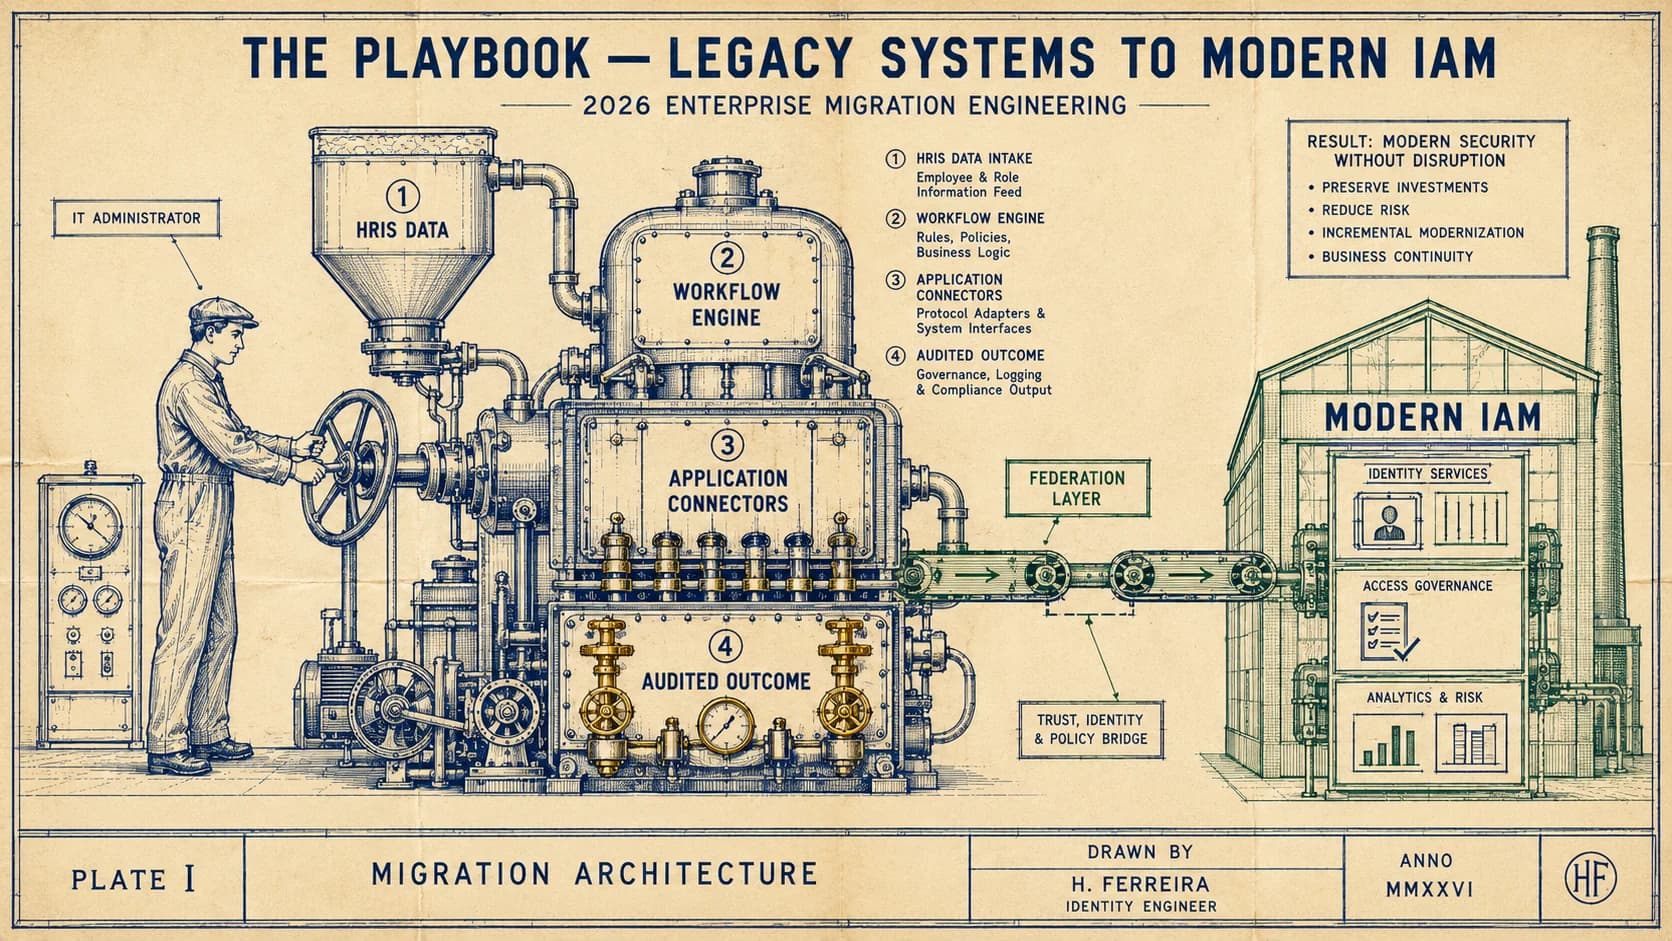
Most enterprises don't have modern IAM — they have some modern IAM layered on top of legacy IAM that never got retired. The 2026 enterprise reference on the 5-phase migration playbook that actually finishes the job: HRIS-driven lifecycle foundation, federation and SSO, phishing-resistant MFA, IGA workflow and certification, and the risk-evaluation layer above.

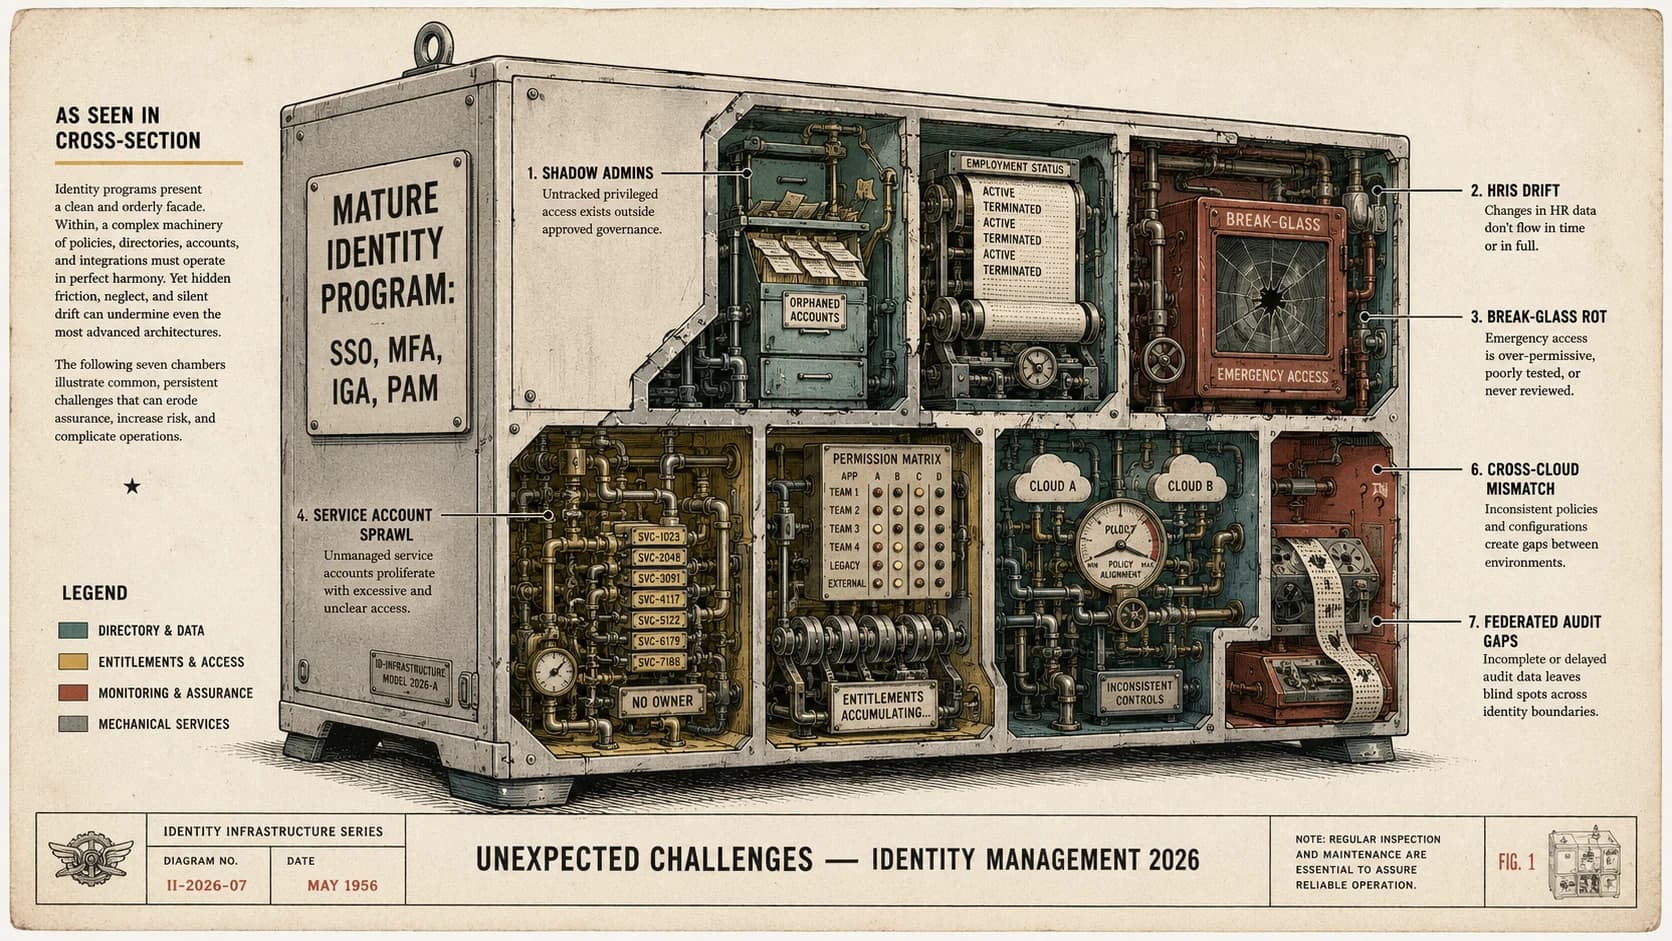
Every mature identity program clears the obvious hurdles — SSO is live, MFA is enforced, IGA is deployed, PAM covers privileged accounts. And every mature identity program still gets breached through a set of hidden failure modes that don't appear on the architecture diagram. The 2026 enterprise reference on the seven challenges that undermine identity programs after the obvious problems are solved — shadow admins, HRIS-drift orphans, break-glass credential rot, service account sprawl, permission drift over time, cross-cloud entitlement mismatch, and federated audit-trail gaps.

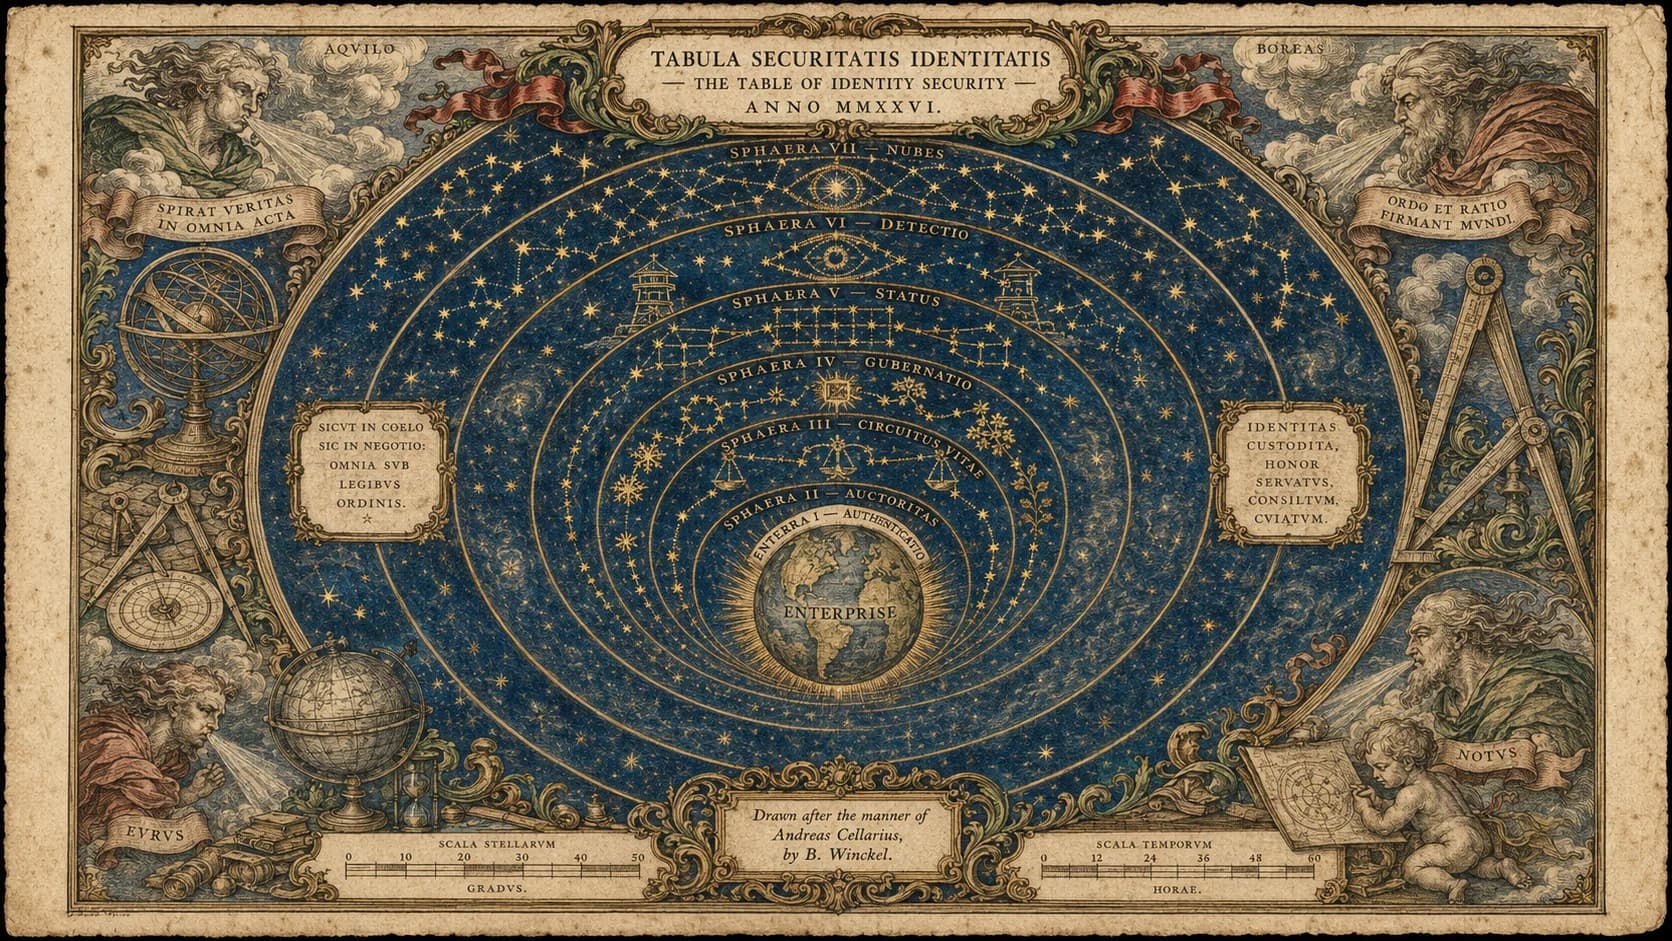
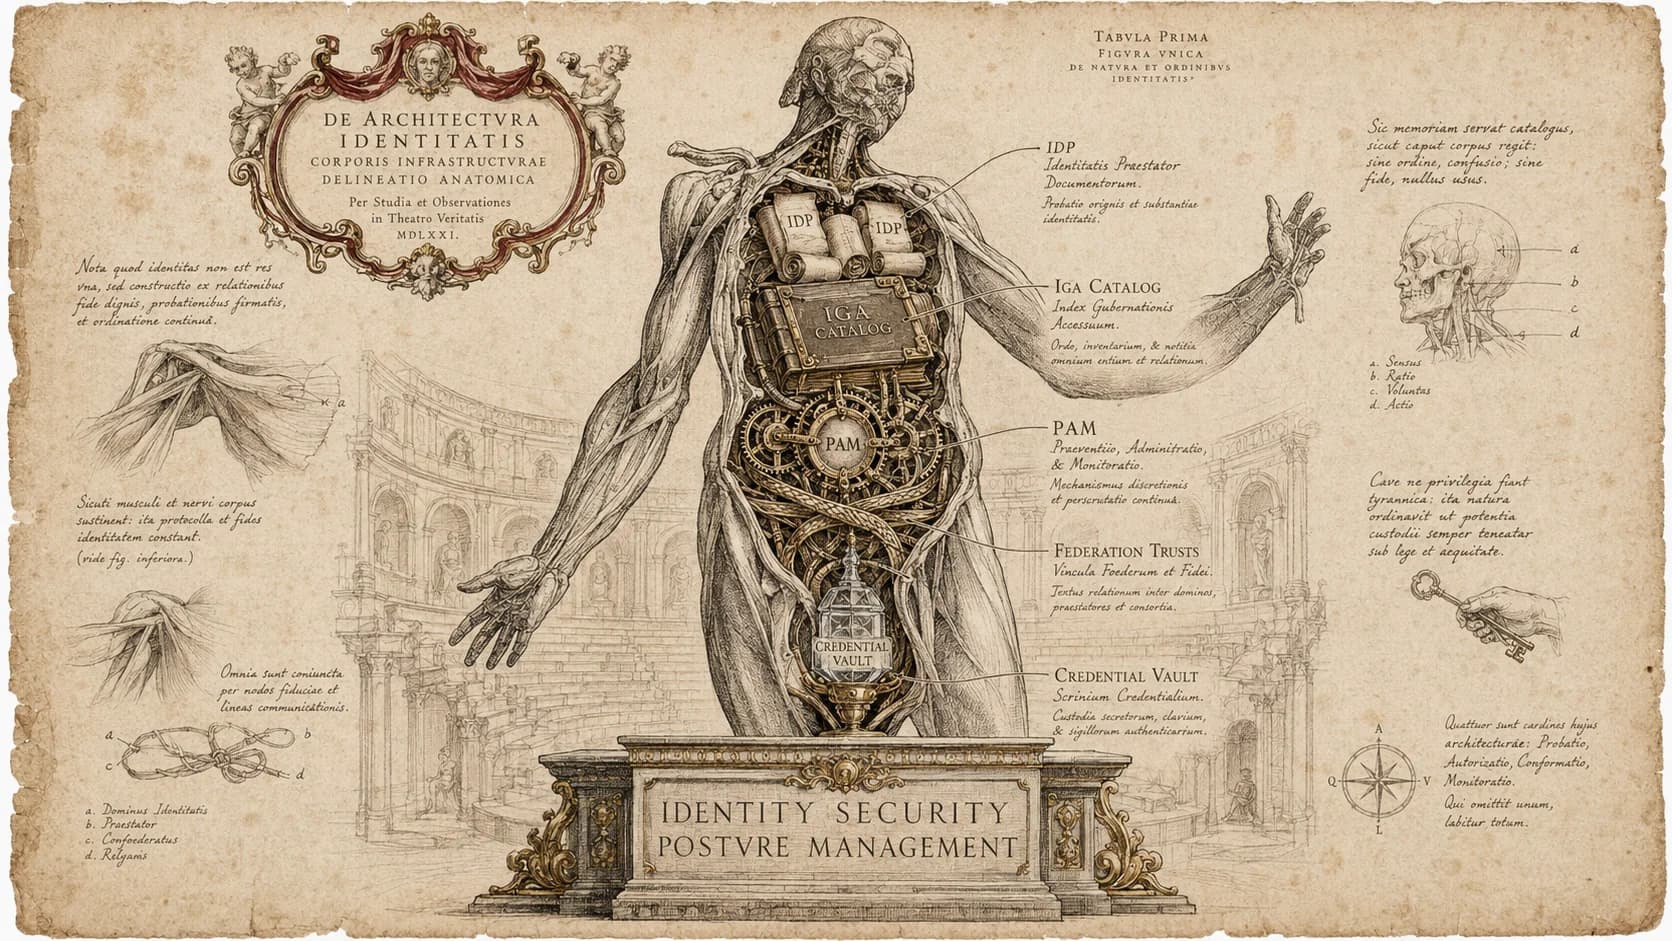
Identity and Access Management isn't a single product, a single category, or a single architectural decision. It's a layered envelope of capabilities — authentication, authorization, lifecycle, governance, posture, detection — that compose into the security foundation of modern enterprise IT. The definitive 2026 enterprise reference.

Traditional IGA was built for workforce identity in defined business systems. Cloud infrastructure is a different problem — thousands of permissions per cloud account, machine-identity dominance, inheritance through nested groups and policies, scale that no human reviewer can certify manually. CIEM is the emerging analyst category that handles this complexity. The 2026 enterprise reference on the four CIEM domains, the vendor landscape, and the architectural composition with IGA, PAM, and ISPM.

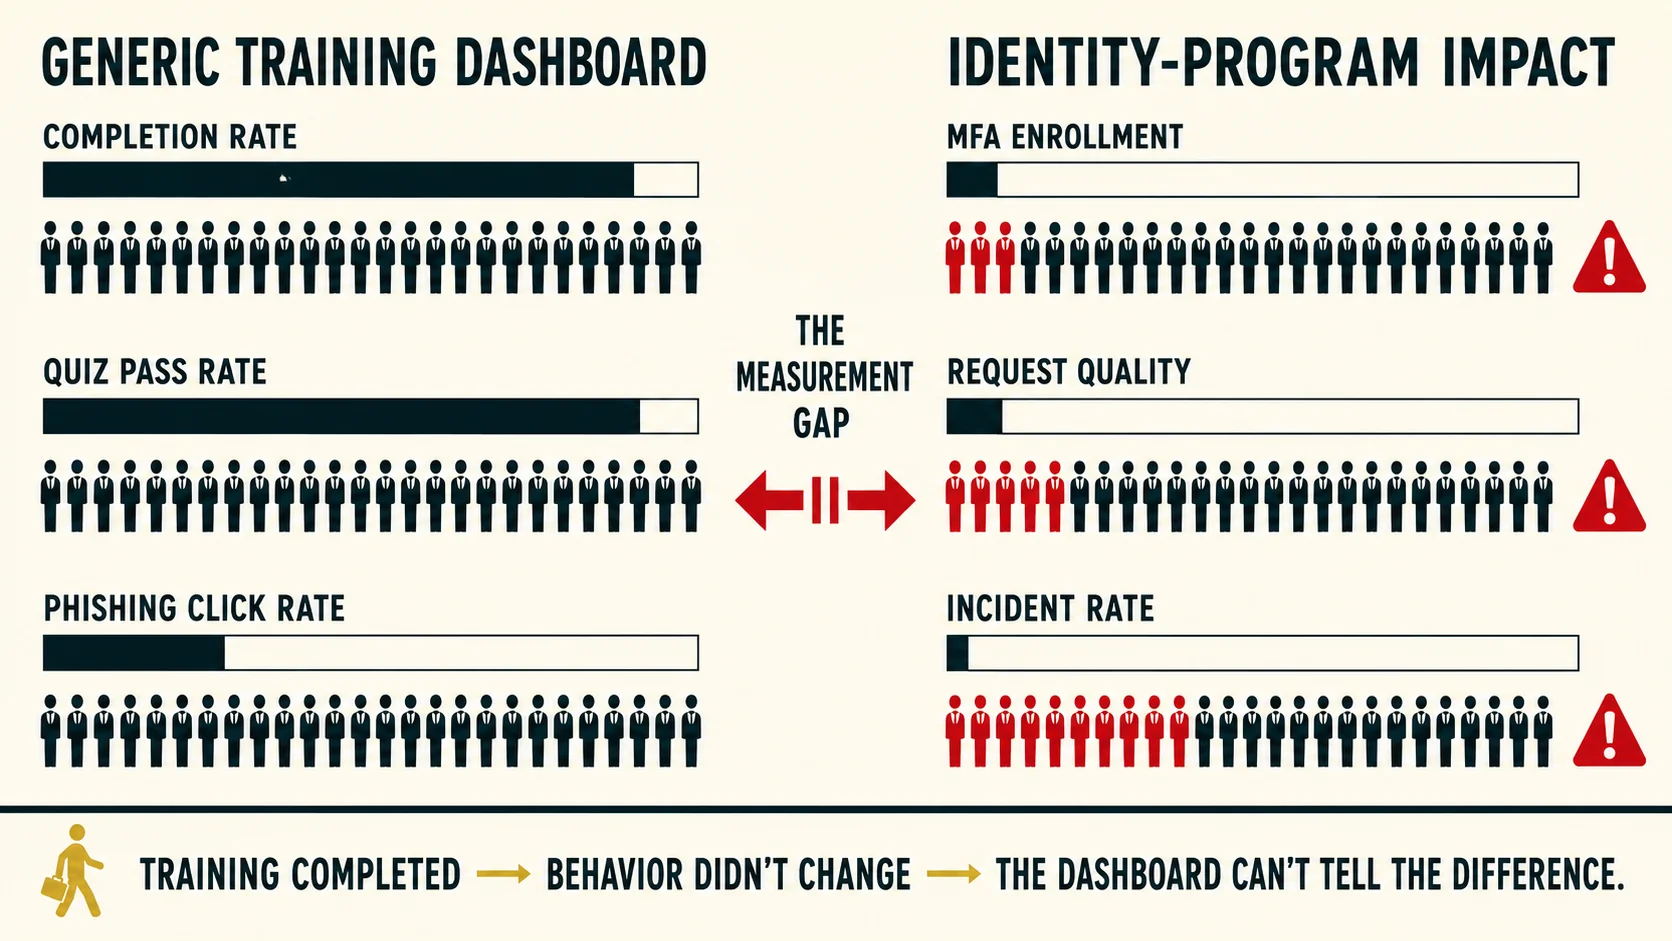
Most security awareness training dashboards measure participation and quiz scores. Identity programs need to measure something different — whether the training actually changed the credential-handling, MFA-adoption, and access-request behaviors that determine the identity-attack surface. The 2026 enterprise reference on the five identity-specific KPI categories, the telemetry integration that makes them measurable, and where most training measurement programs break.

60% of IGA deployments stall. The platform is in production, the consultants left, the certification campaigns happen on paper but produce nothing actionable, and leadership wants to know why the program isn't delivering. The 2026 enterprise reference on the four failure patterns that produce stalled IGA, when to restart vs continue, and what a phased recovery actually looks like.

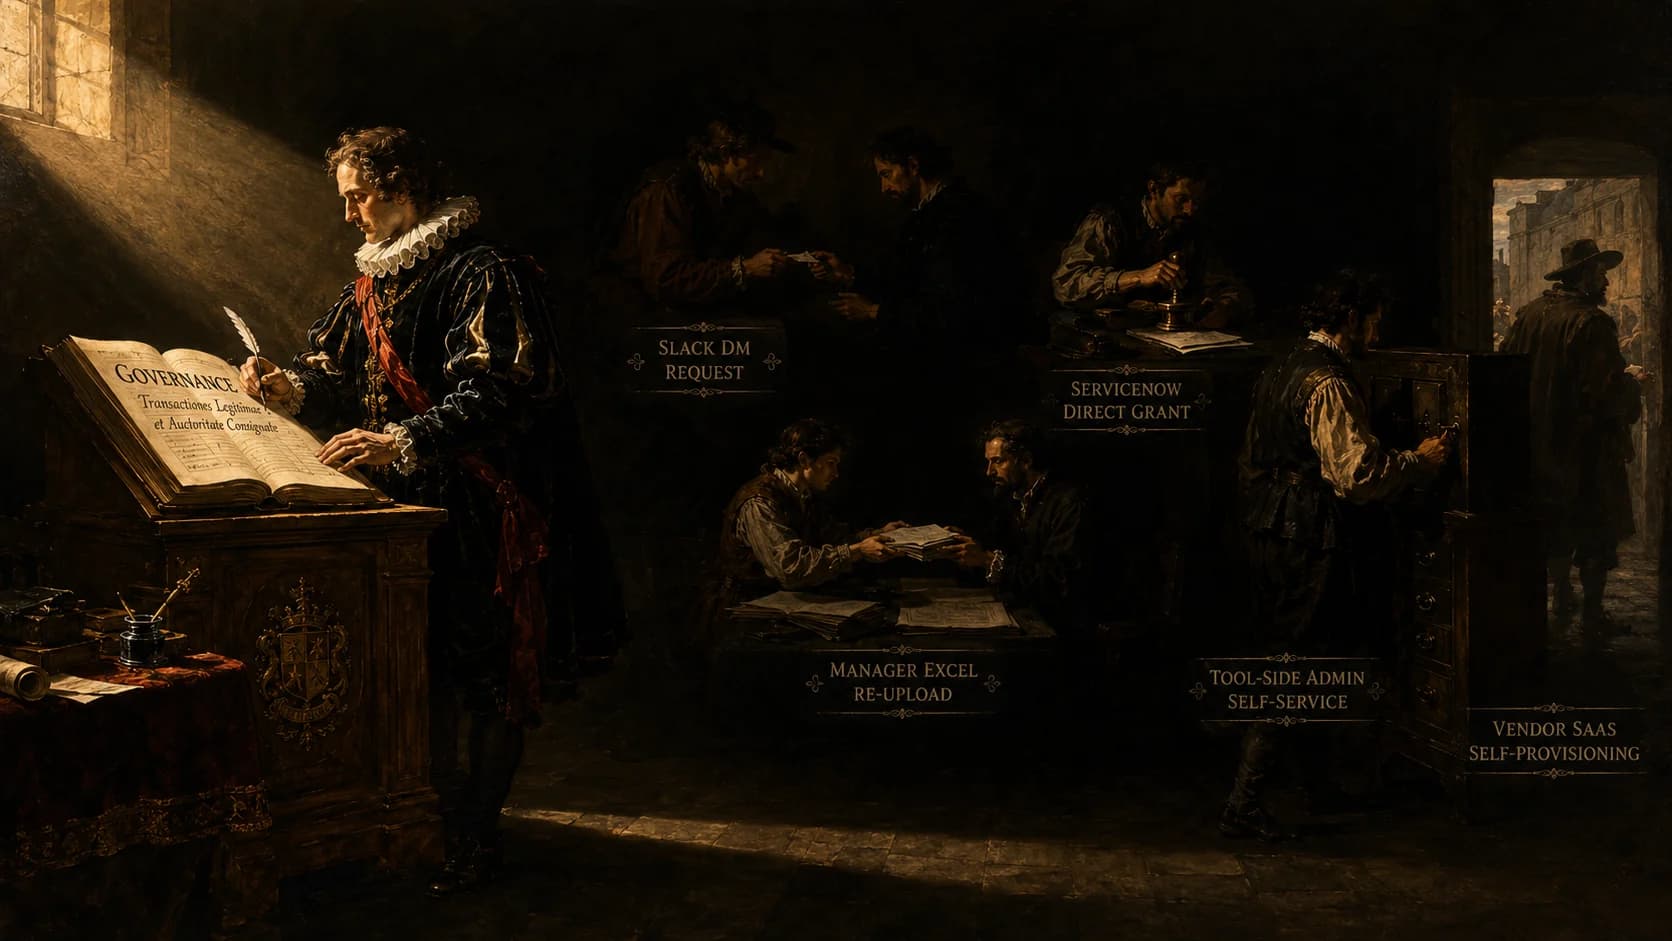
Most enterprise access doesn't flow through the IGA platform — it flows through Slack DMs, ServiceNow tickets routed to direct grant, manager spreadsheets, tool-side admin self-service, and vendor SaaS self-provisioning. The 2026 enterprise reference on shadow IT provisioning, why it bypasses even mature IGA programs, and the architectural pattern that captures it without breaking the operational flow.

ISPM is the emerging analyst category that sits above IGA and beside ITDR — the preventive posture audit, drift detection, and identity-asset inventory layer that answers 'is our identity infrastructure currently configured the way our policy says it should be.' The 2026 enterprise reference on the evaluation domains, vendor landscape, and integration architecture.

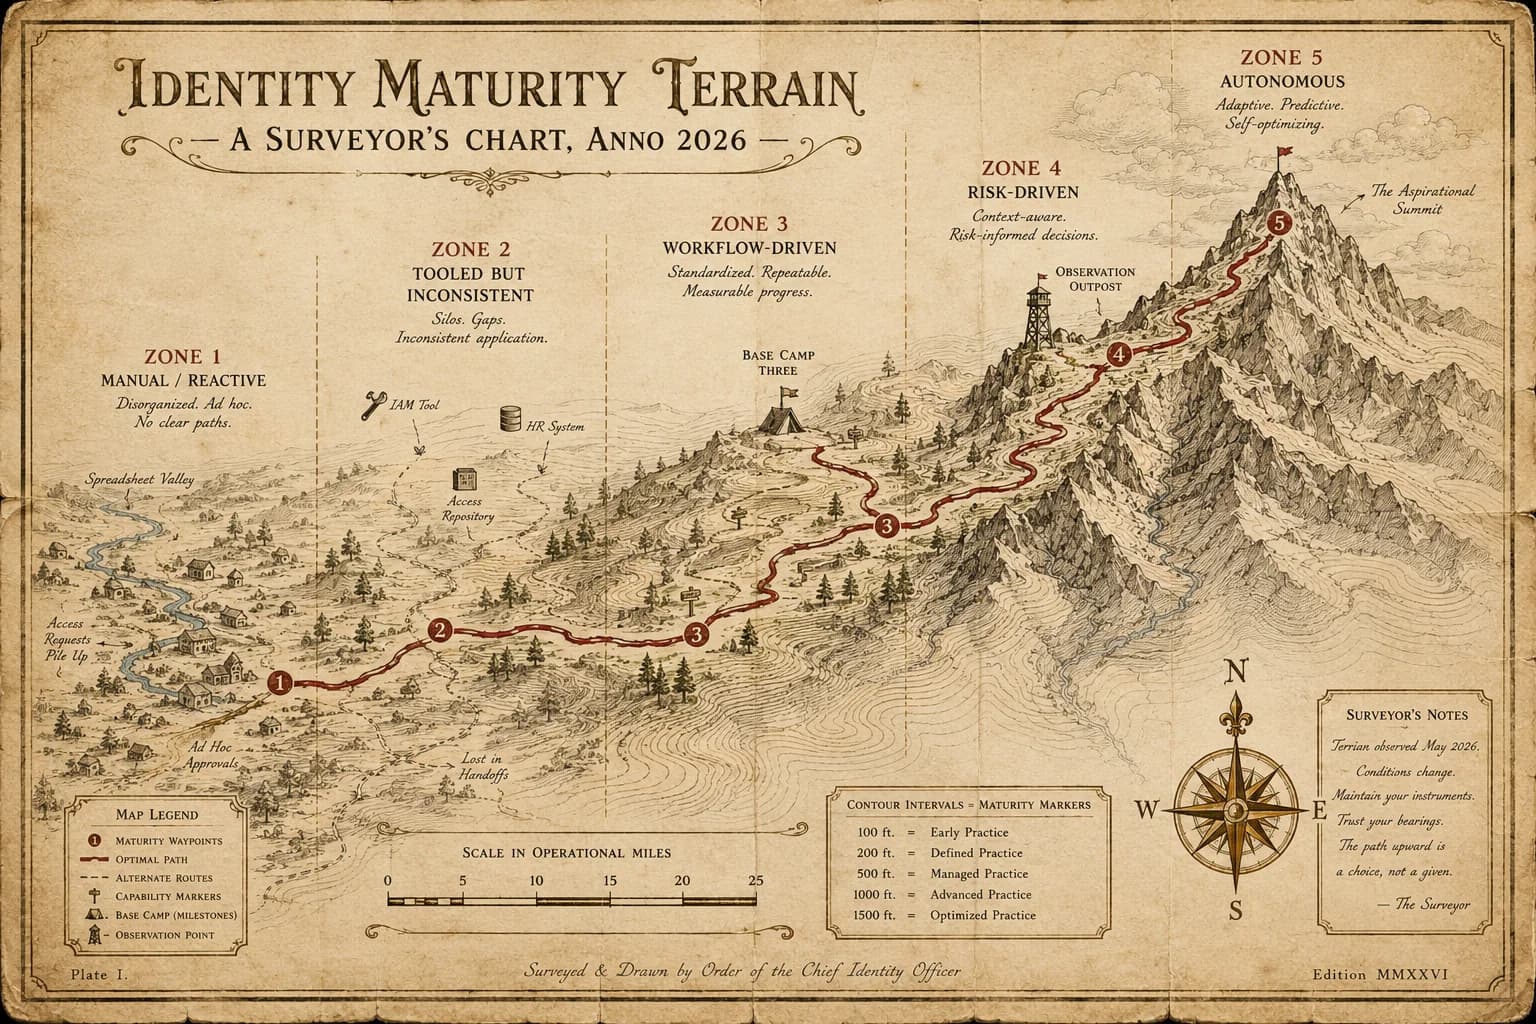
Every enterprise identity program sits at one of five maturity stages — from manual and reactive at Stage 1 to autonomous and AI-augmented at Stage 5. The 2026 enterprise reference on the five-stage model, the self-assessment criteria that locate where you stand, and the operational moves that get you to the next stage.

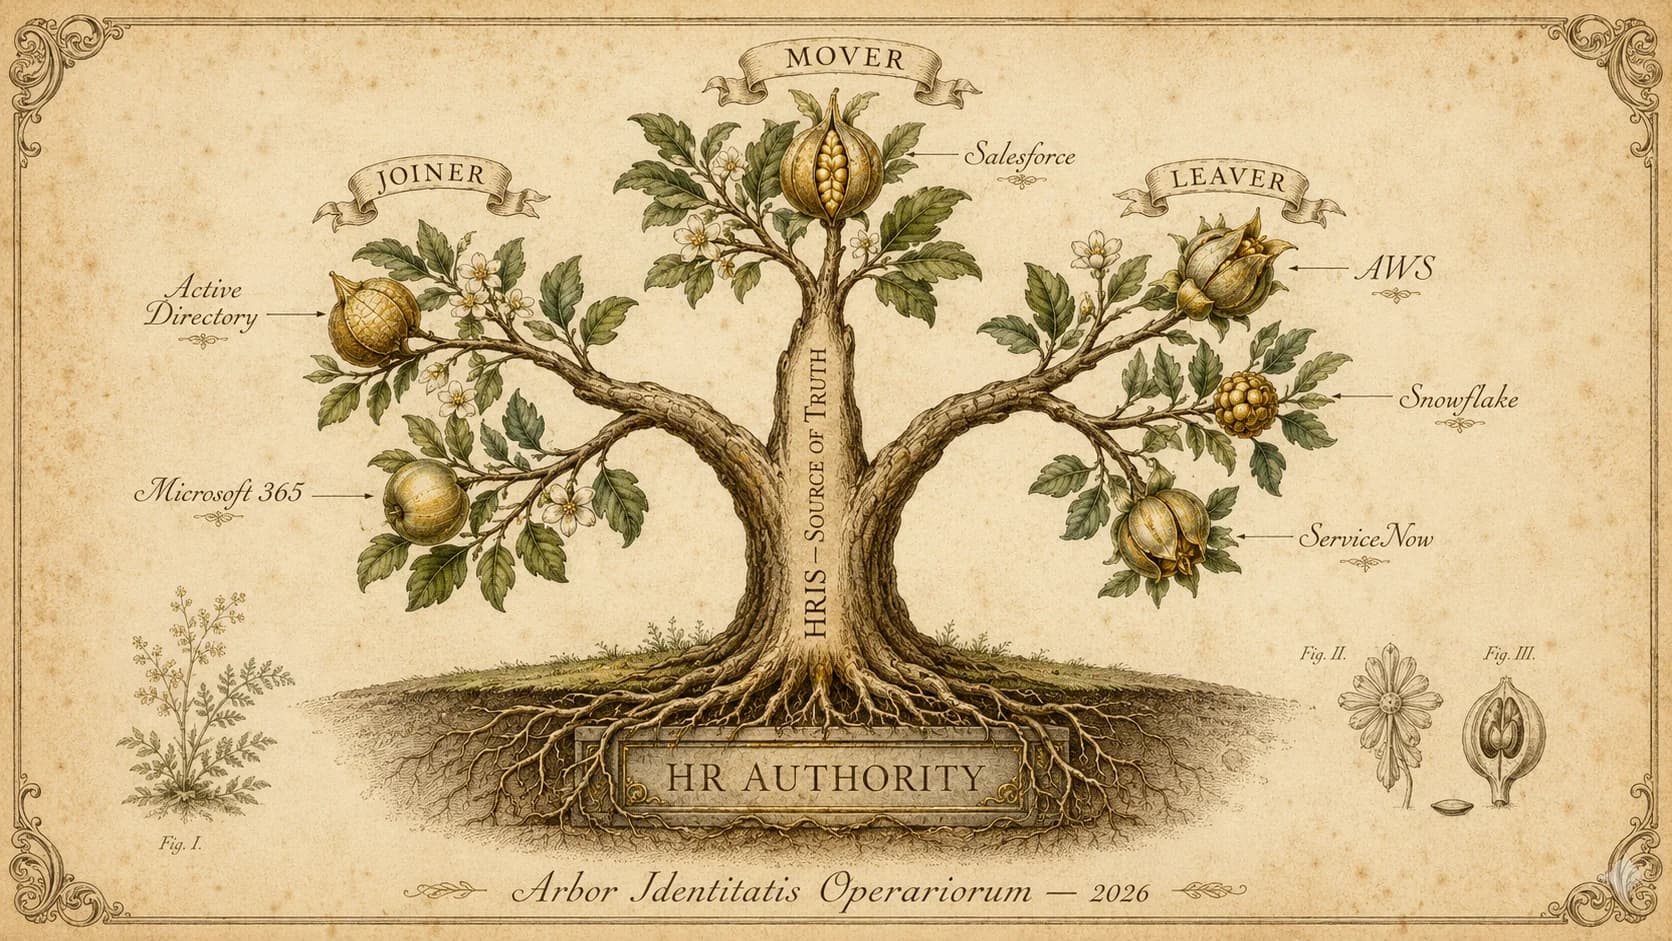
Modern identity governance treats the HRIS — SAP SuccessFactors, Workday, BambooHR, ADP — as the authoritative source of truth for who works at the organization, what role they hold, and when their access should change. The 2026 enterprise reference on the integration patterns, schema discipline, and architecture that survives HRIS upgrades.

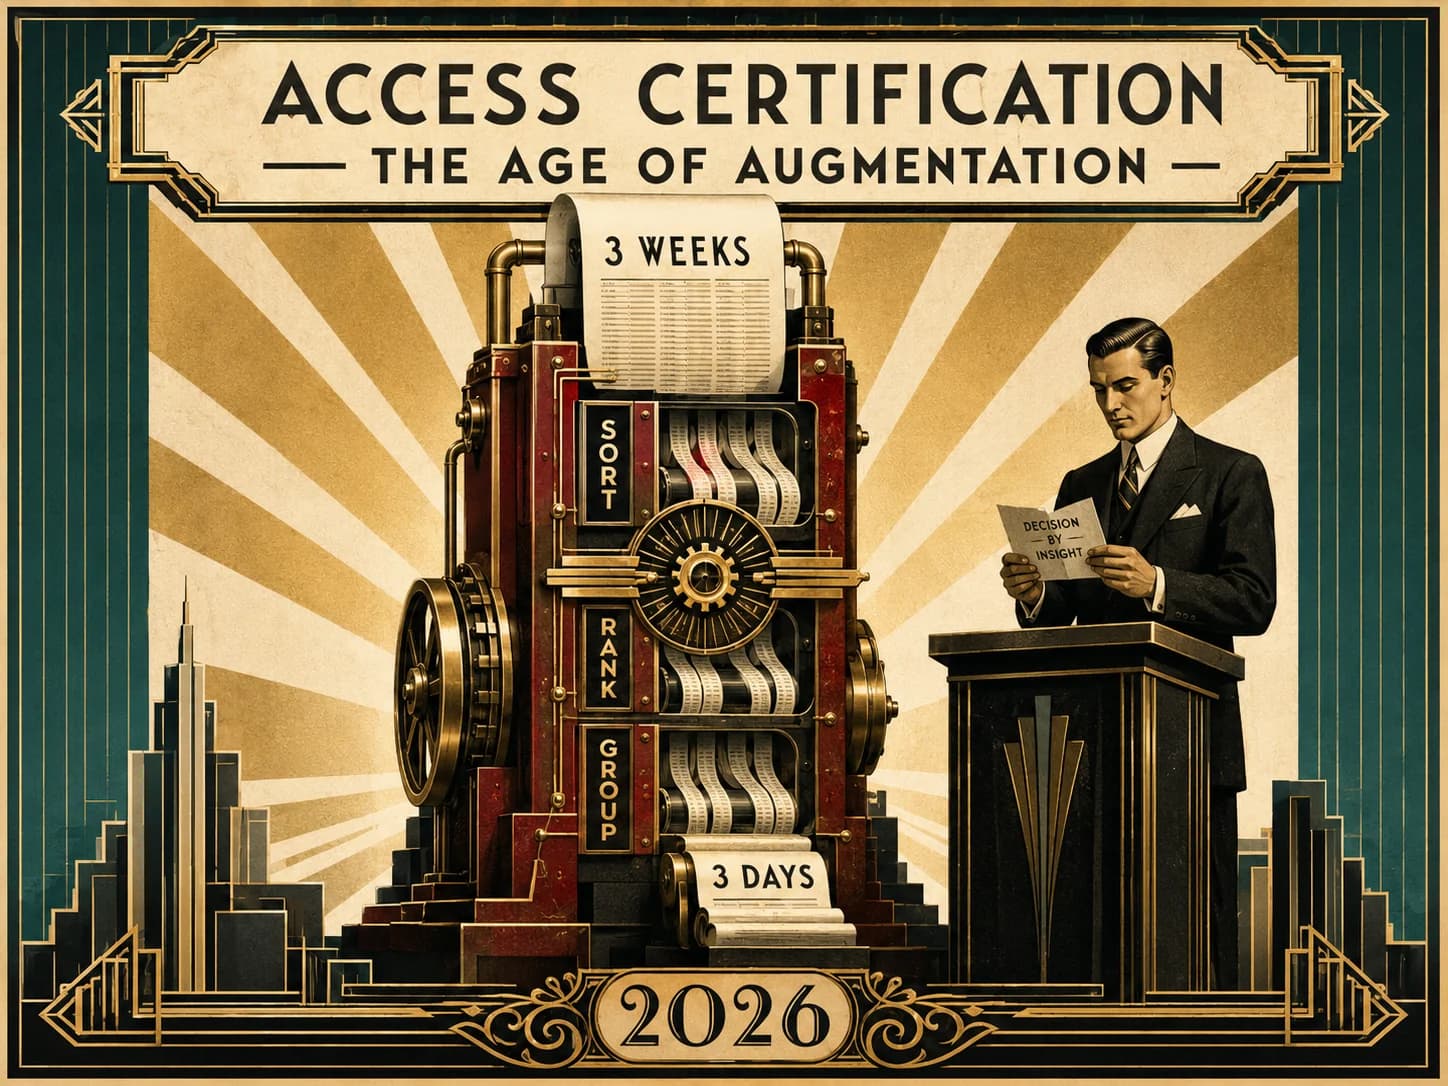
Quarterly access certification campaigns are the operational backbone of IGA — and the place where certification fatigue does the most damage. The 2026 enterprise reference on what AI actually automates in certification (not the vendor-marketing version), where the time savings come from operationally, and where AI-augmented certification breaks if you skip the architectural discipline.

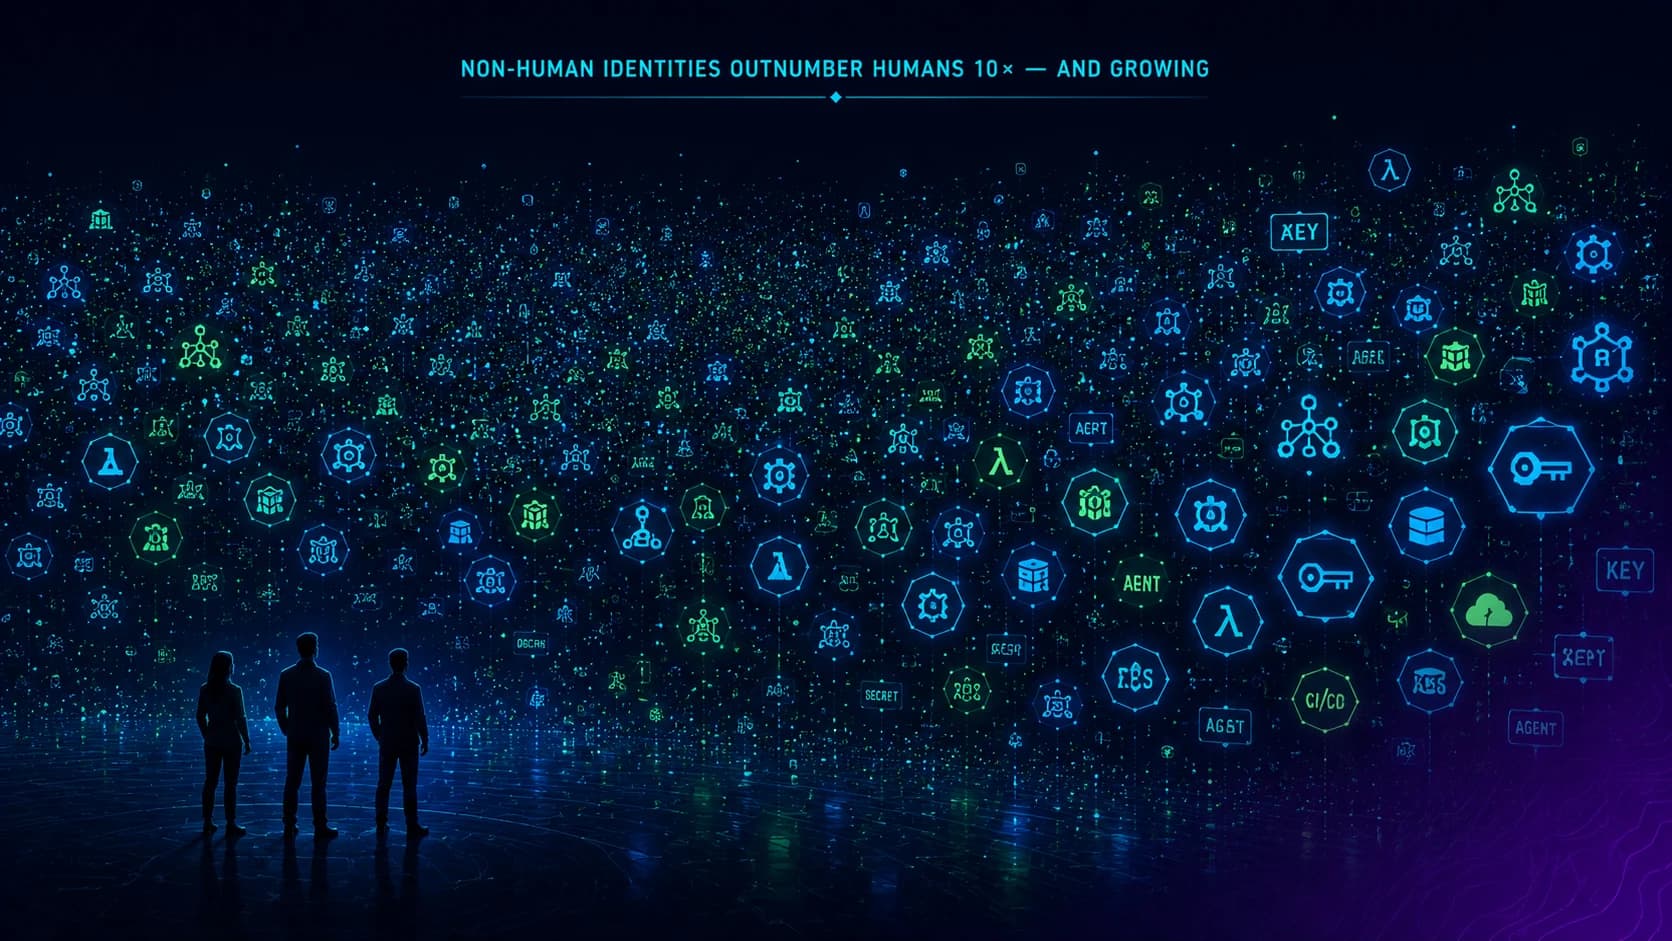
Non-human identities — service accounts, workload identities, API credentials, automation agents, and the rapidly growing population of AI agent identities — now outnumber human identities in most 2026 enterprises by 10× or more. The reference on what NHI is, where the governance gaps are, and the architecture that brings non-human credentials under the same lifecycle discipline as humans.

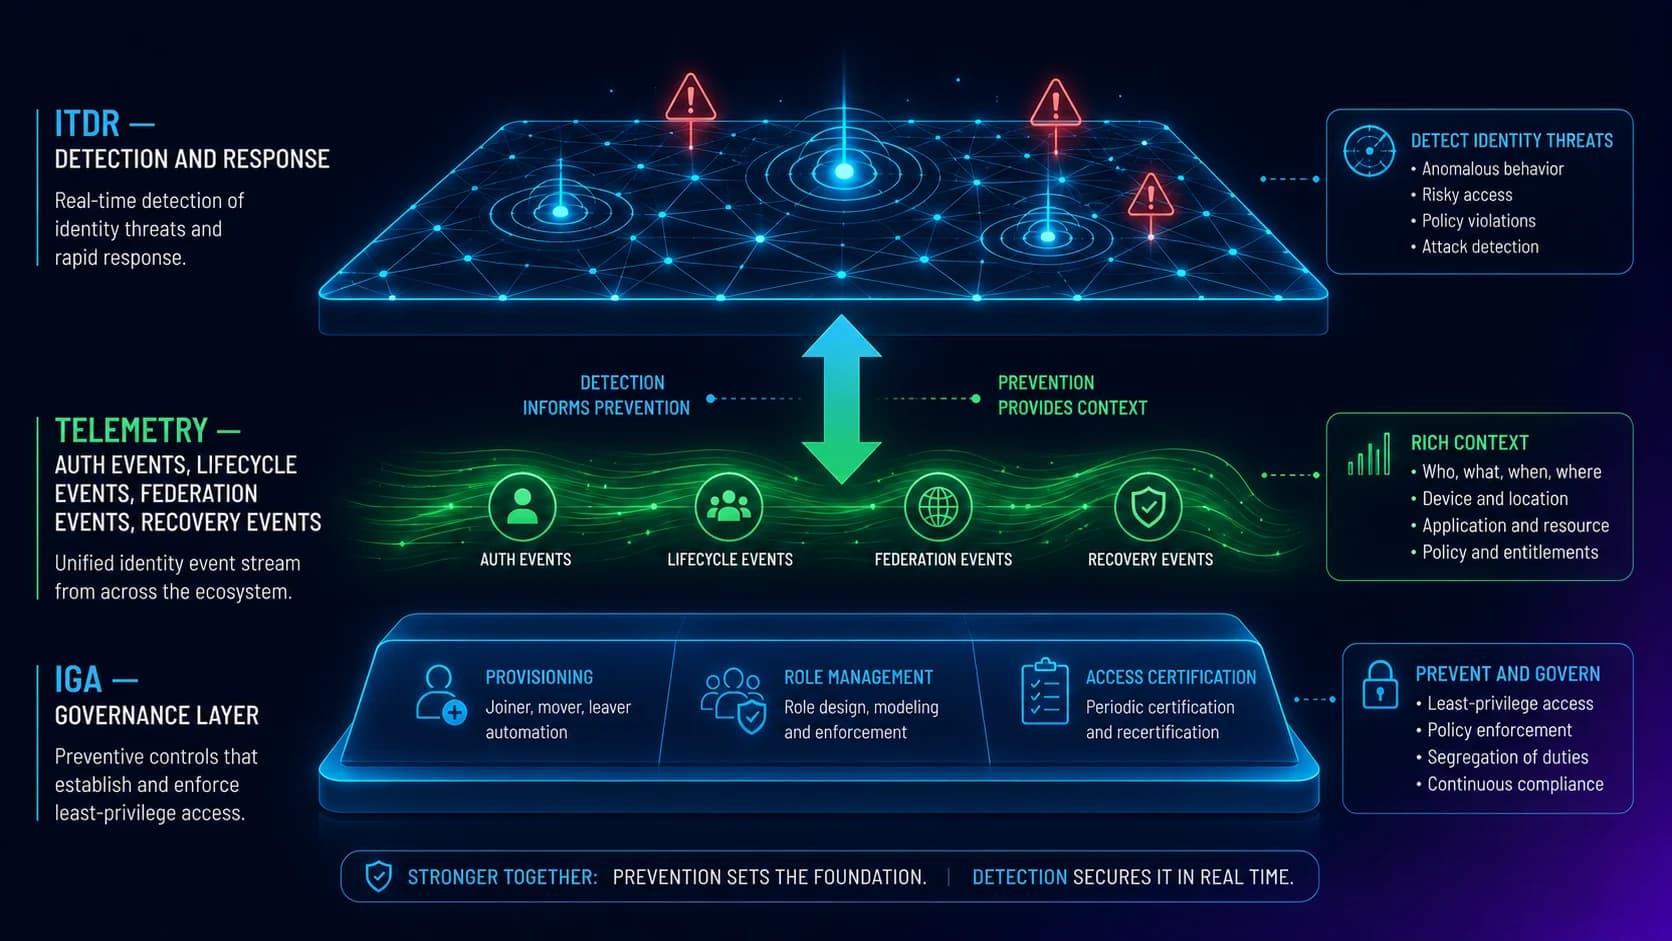
ITDR is the buzzy adjacent category to IGA — and in 2026 it has become a load-bearing layer for any enterprise that wants to detect identity-based attacks instead of just preventing them. The honest guide to what ITDR is, where it fits relative to IGA, and the architecture that ties identity governance to identity detection.

Identity systems generate a lot of suspicious-looking events that aren't actually attacks. The 2026 architecture for separating real signal from noise — without losing the signal.

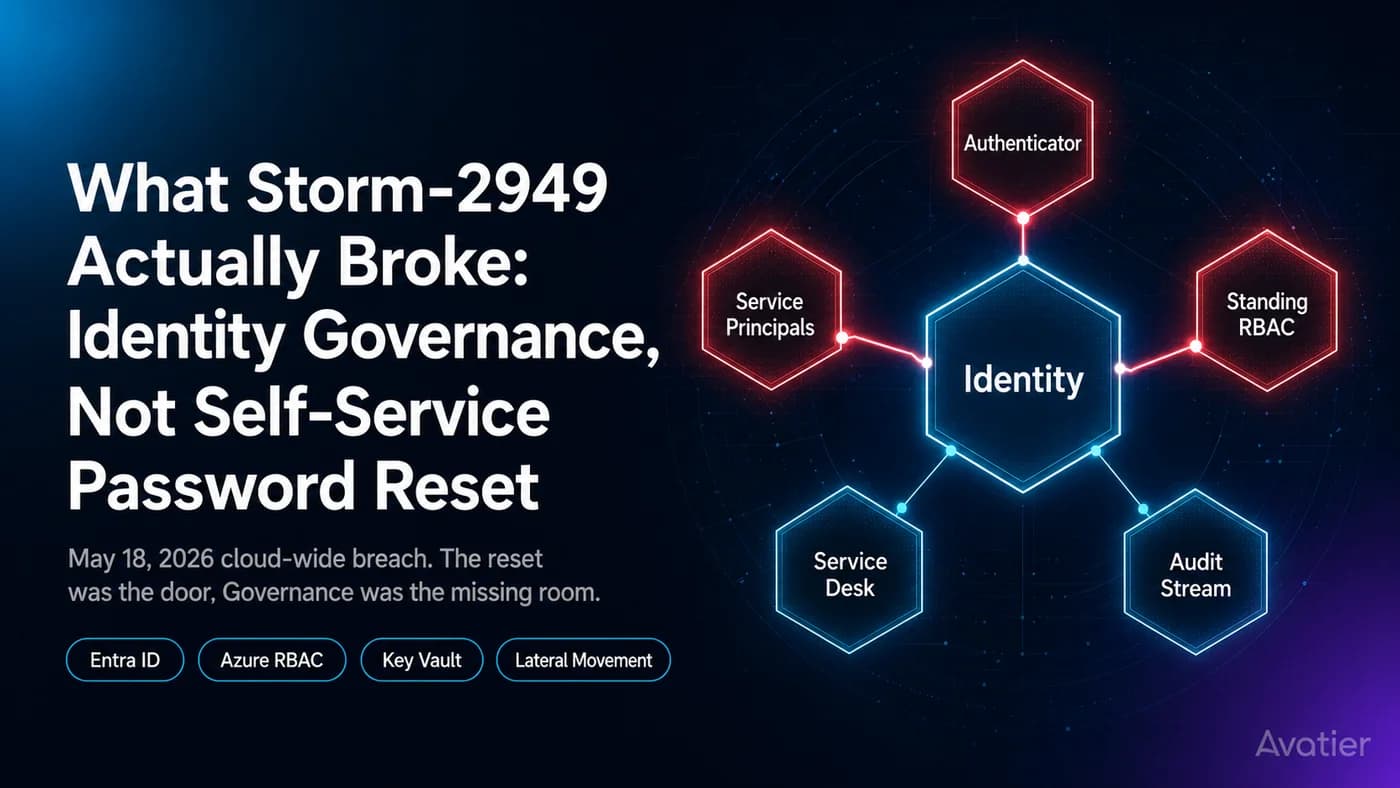
Microsoft's Storm-2949 disclosure exposed an identity governance gap, not a password gap. What service-principal hygiene, JIT RBAC, and lifecycle attestation would have caught.

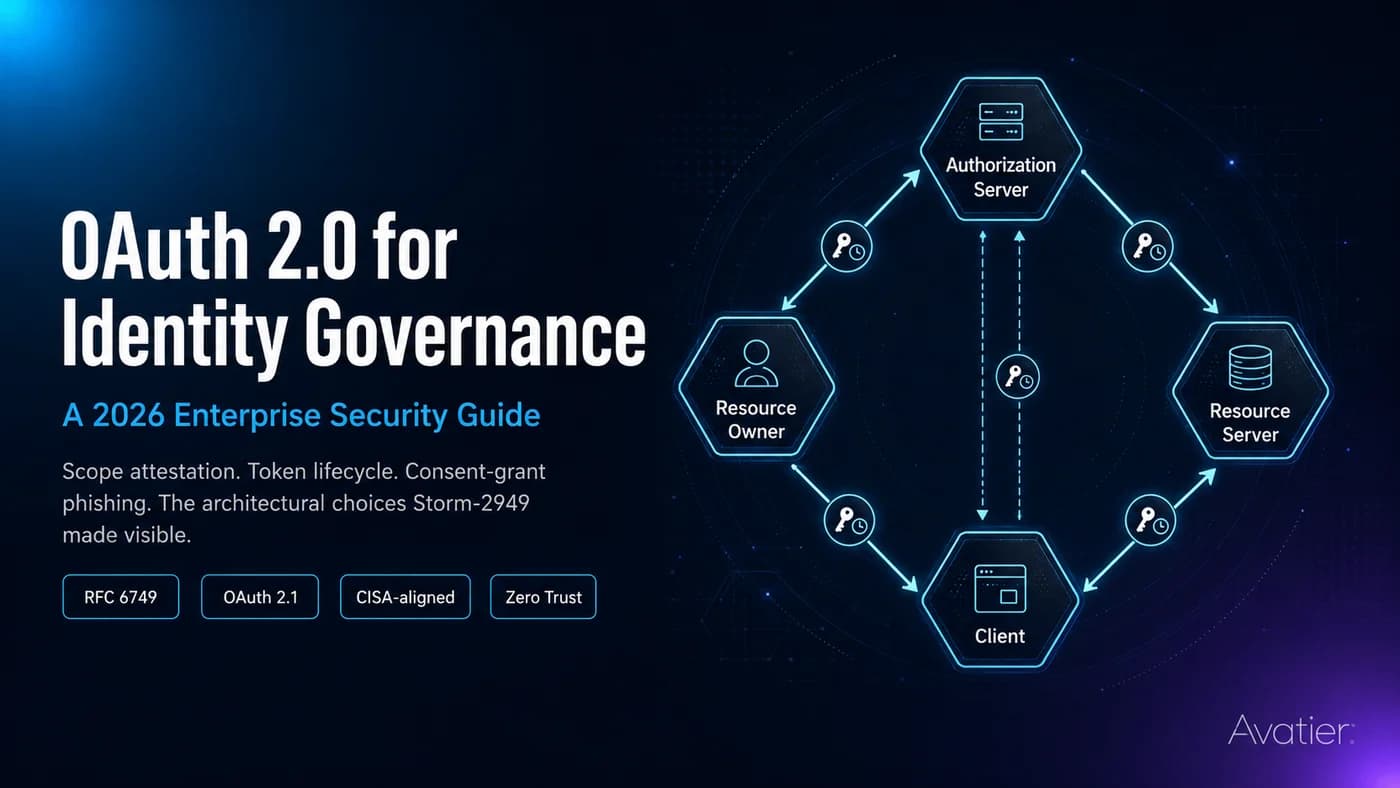
OAuth 2.0 in 2026 enterprise identity governance — scope attestation, token lifecycle, consent-grant phishing, and the architectural choices Storm-2949 made visible.
Savings Calculator
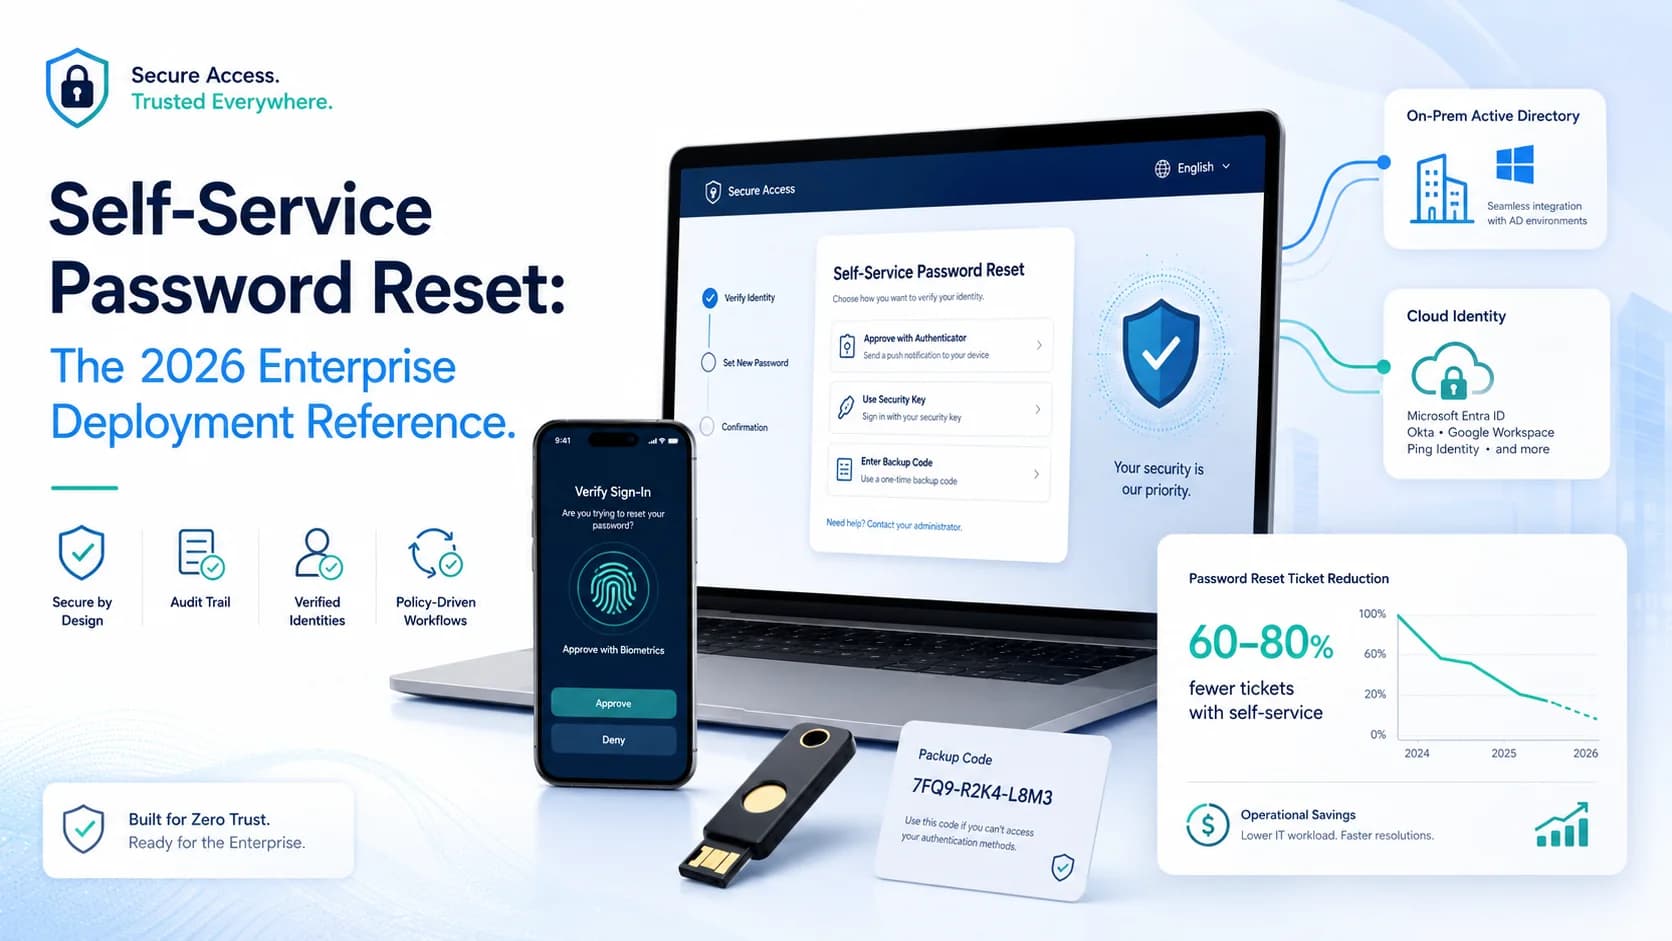
Enter your company size and see how much your help desk spends on password resets — and how much Avatier Credential Governance saves.
Avatier Credential Governance reduces your cost by
Over 1 year